PREEMPTIVE IDENTITY EXPOSURE MANAGEMENT

The preemptive identity security platform

Reduce identity exposure before attackers exploit it. Saporo connects human and non-human identities, permissions, relationships, and activity across your hybrid environment.

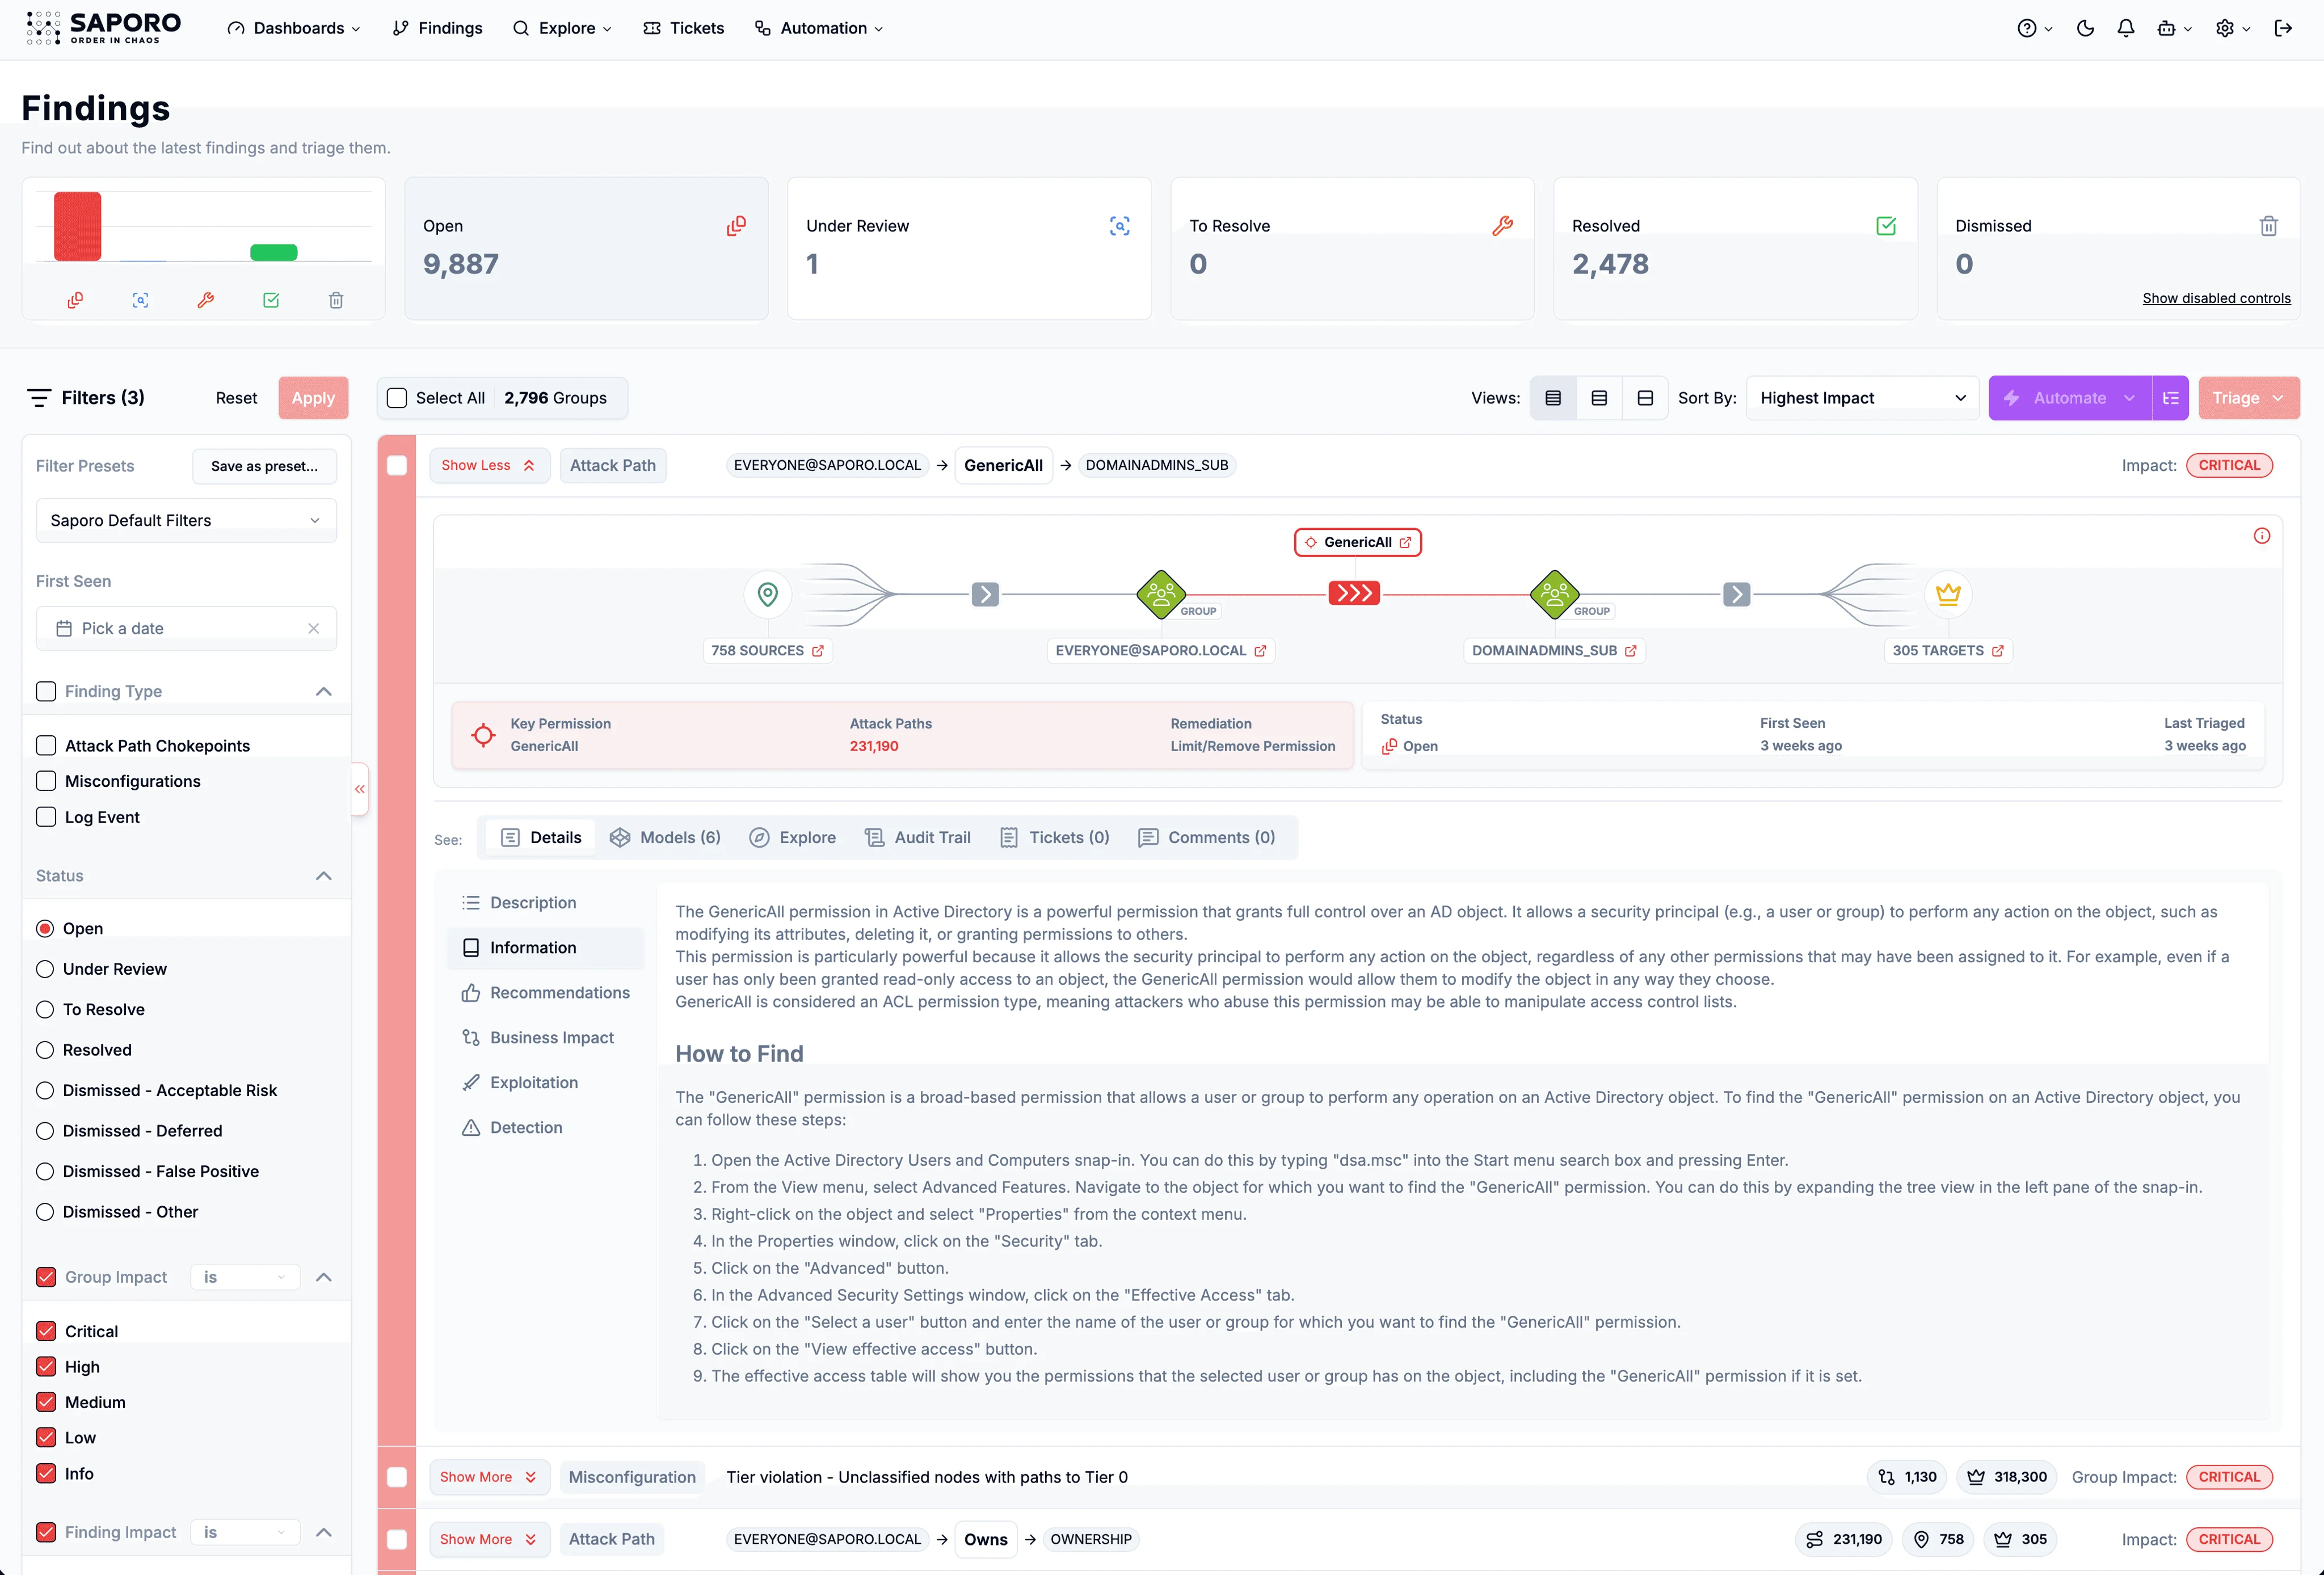
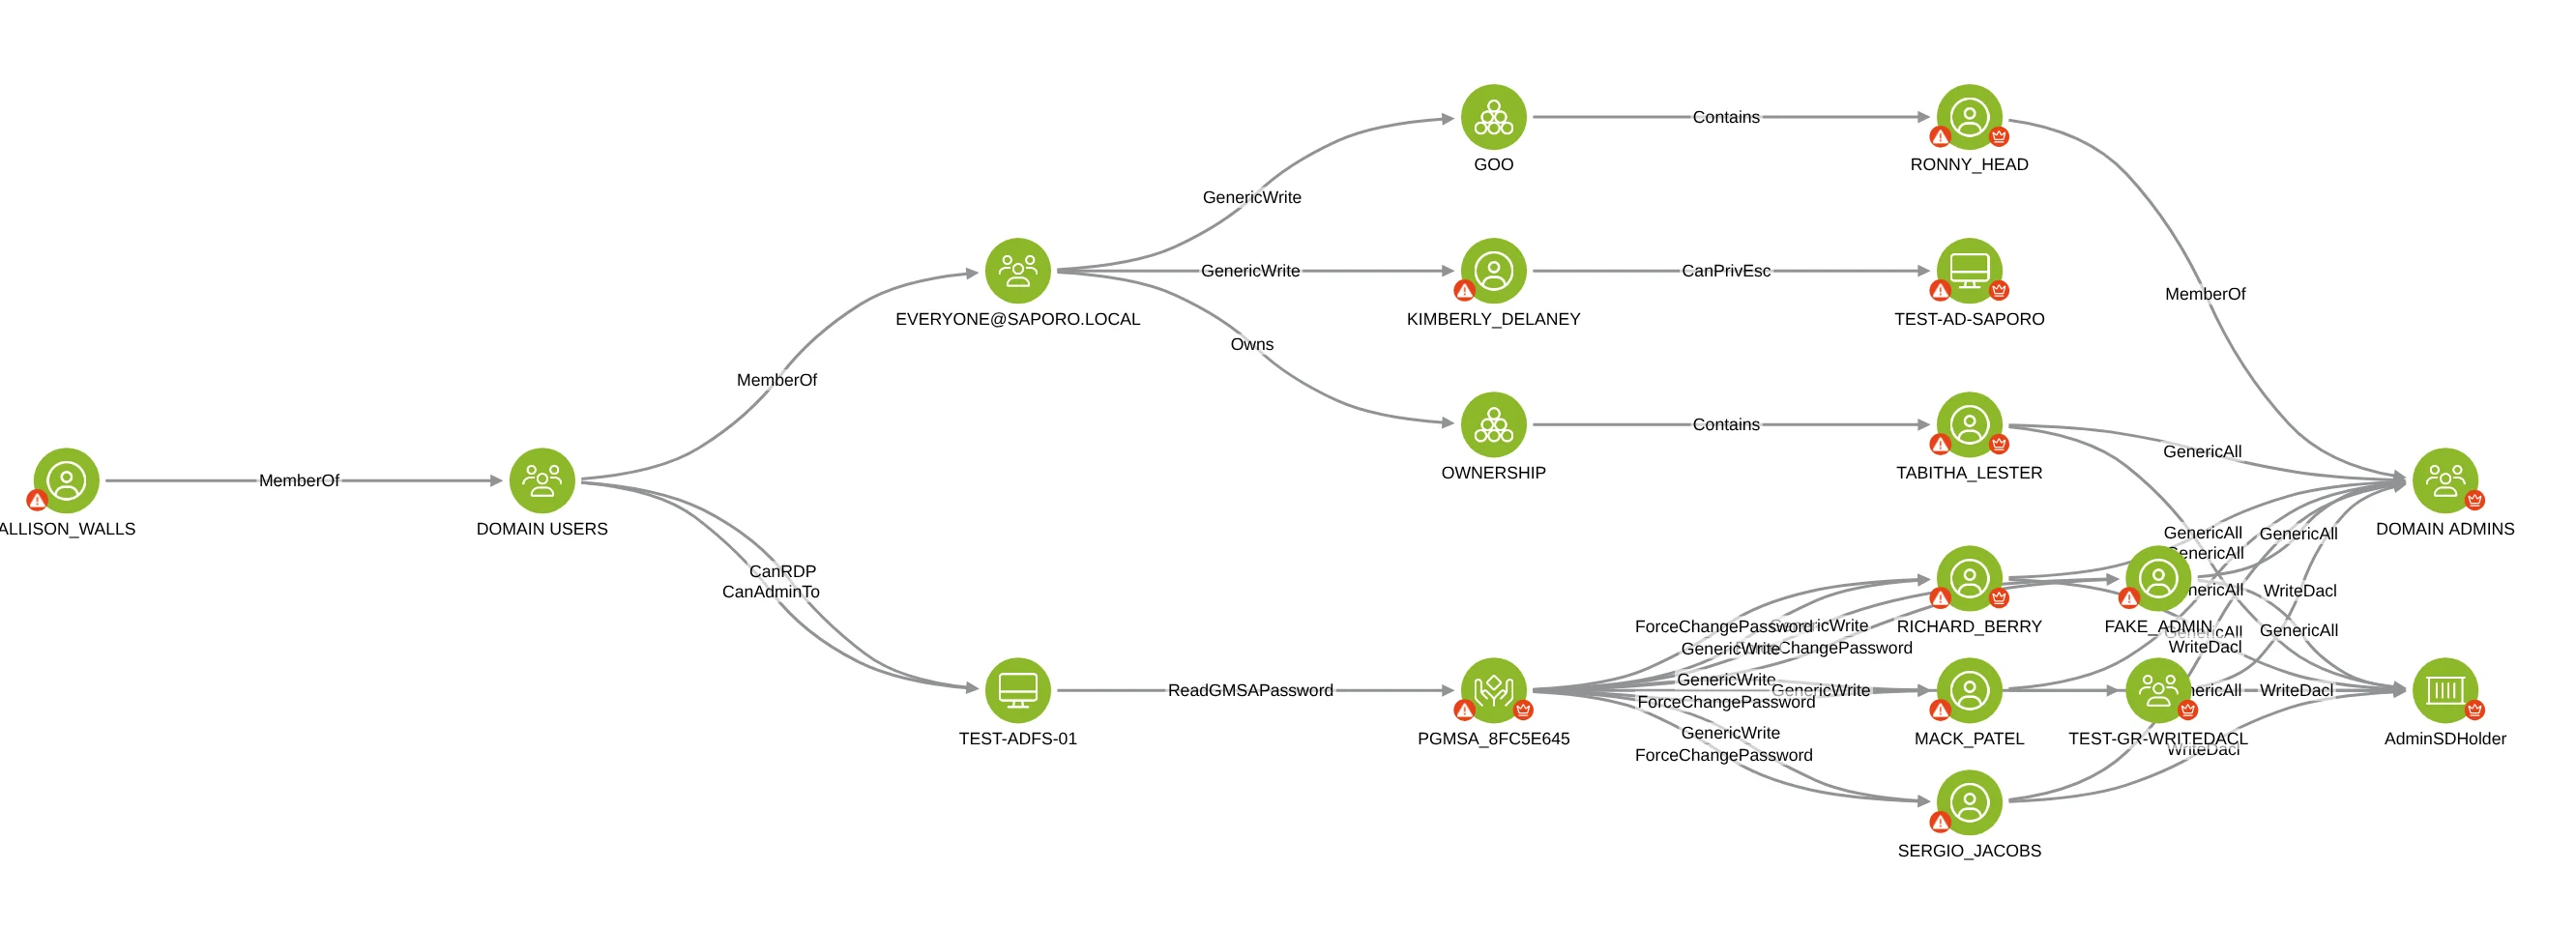
It reveals attack opportunities, including attack paths, misconfigurations, and flagged events, and prioritizes action by reachability, blast radius, and impact on critical assets. Reduce exposure through guided remediation and governed automation, with progress measured over time.

From reactive to preemptive

Reduce attack opportunities before attackers exploit them

Preemptive security

Discover. Prioritize. Remediate.

Saporo helps you remove attack opportunities before attackers can use them. Fix misconfigurations, reduce excessive permissions, and break attack paths, closing off the options attackers would use to reach critical assets.

Attack opportunity removed

Reactive security

Detect. Investigate. Respond.

Alerts surface suspicious activity. Teams investigate what attackers are doing and respond to contain the threat, limit its impact, and stop further movement toward critical assets.

Attacker activity detected

Saporo complements detection and response by reducing attacker options and providing context on what they could reach.

The operating cycle

A complete lifecycle for reducing identity exposure

Scope

01

What identities and systems make up our attack surface?

Build a unified identity view

Connect identities, permissions, relationships, and activity across supported on-premises and cloud sources to build a unified view of exposure.
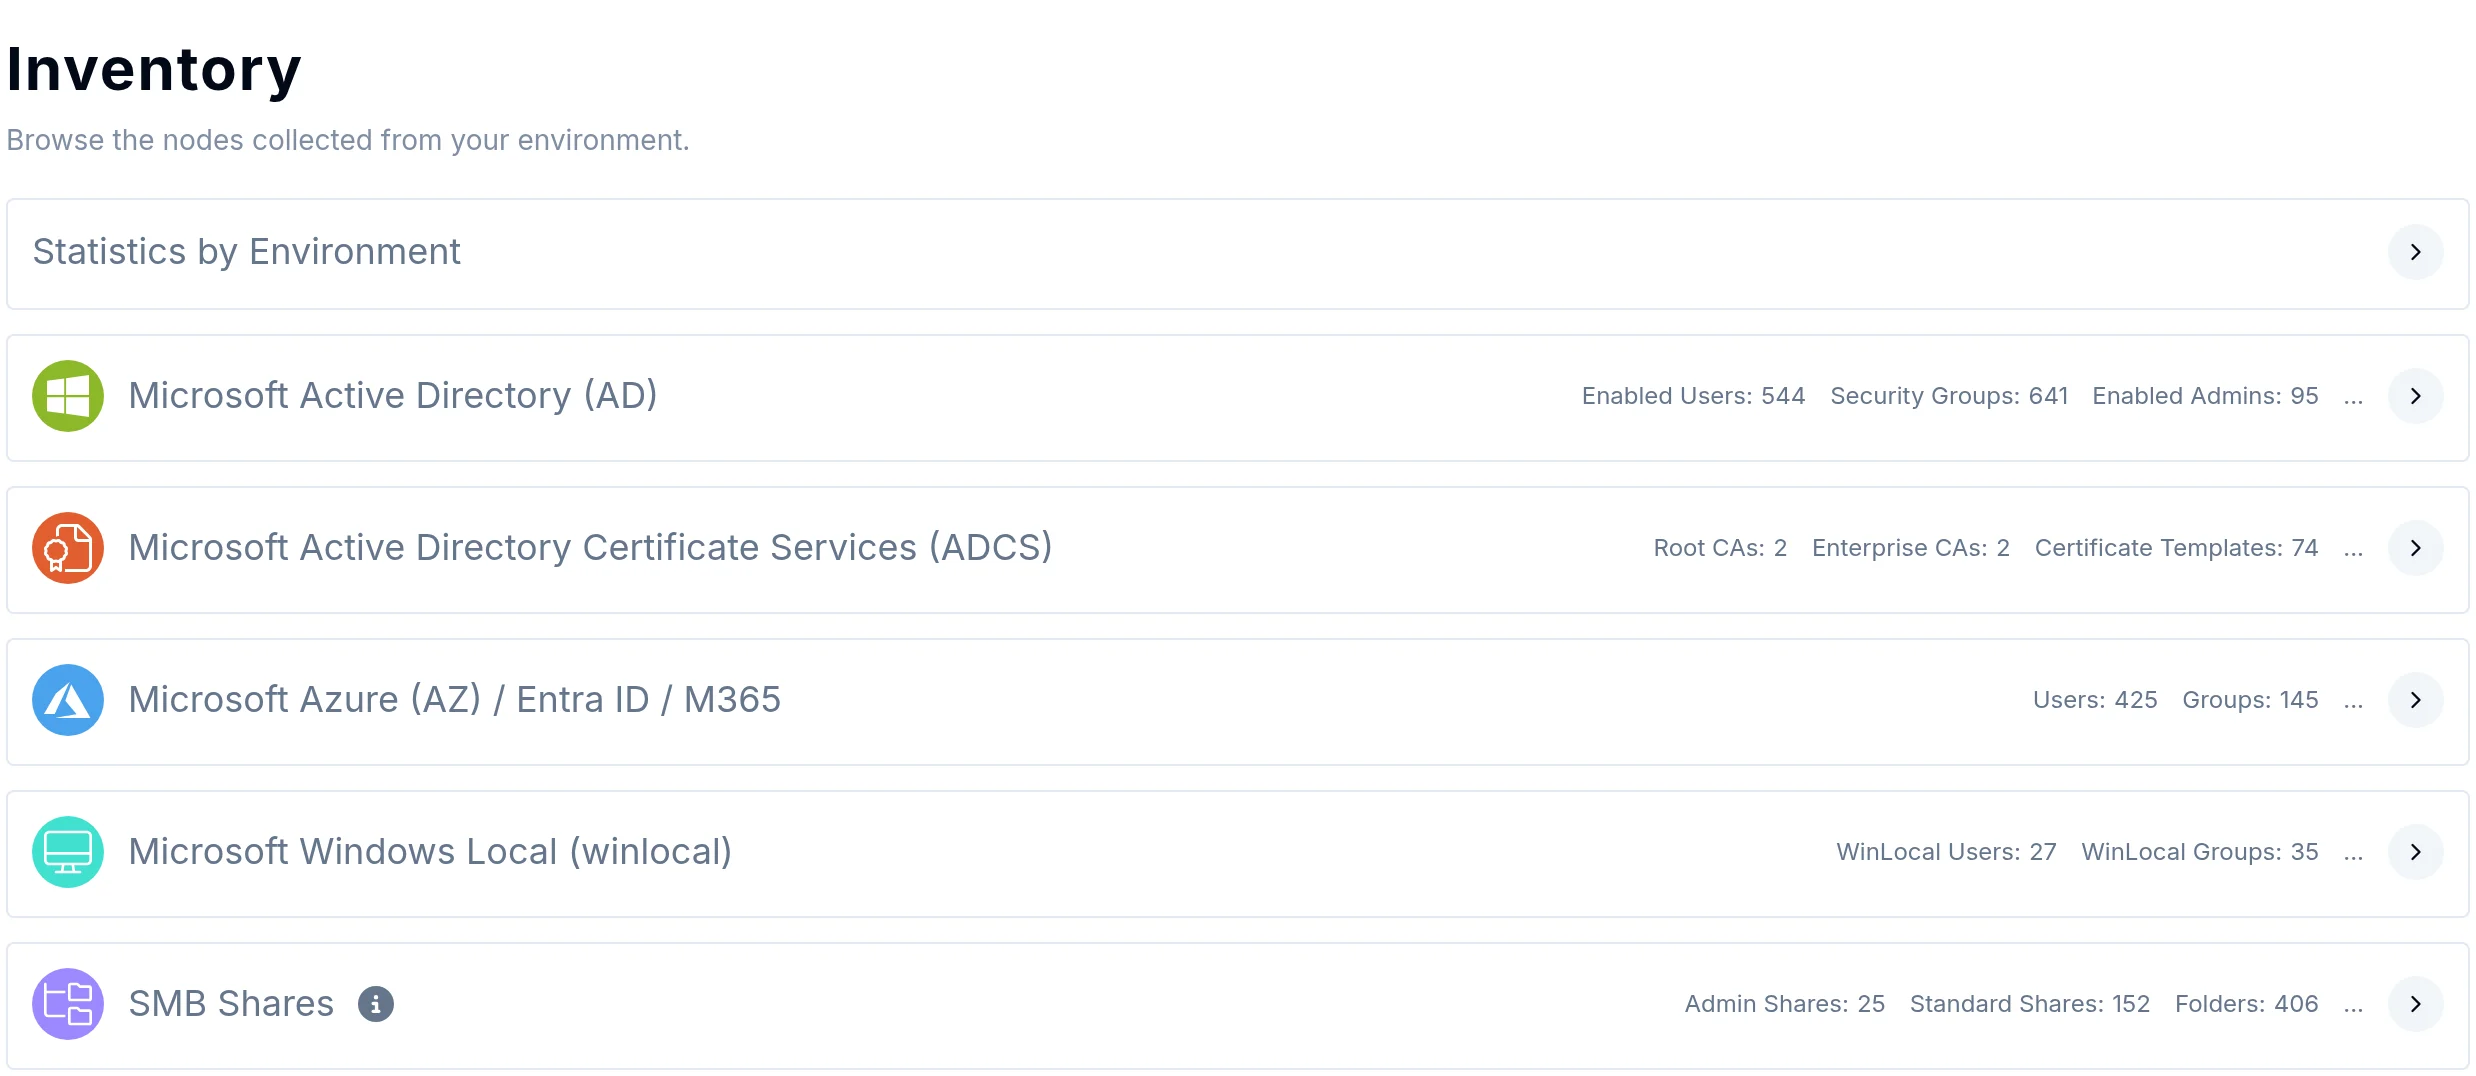
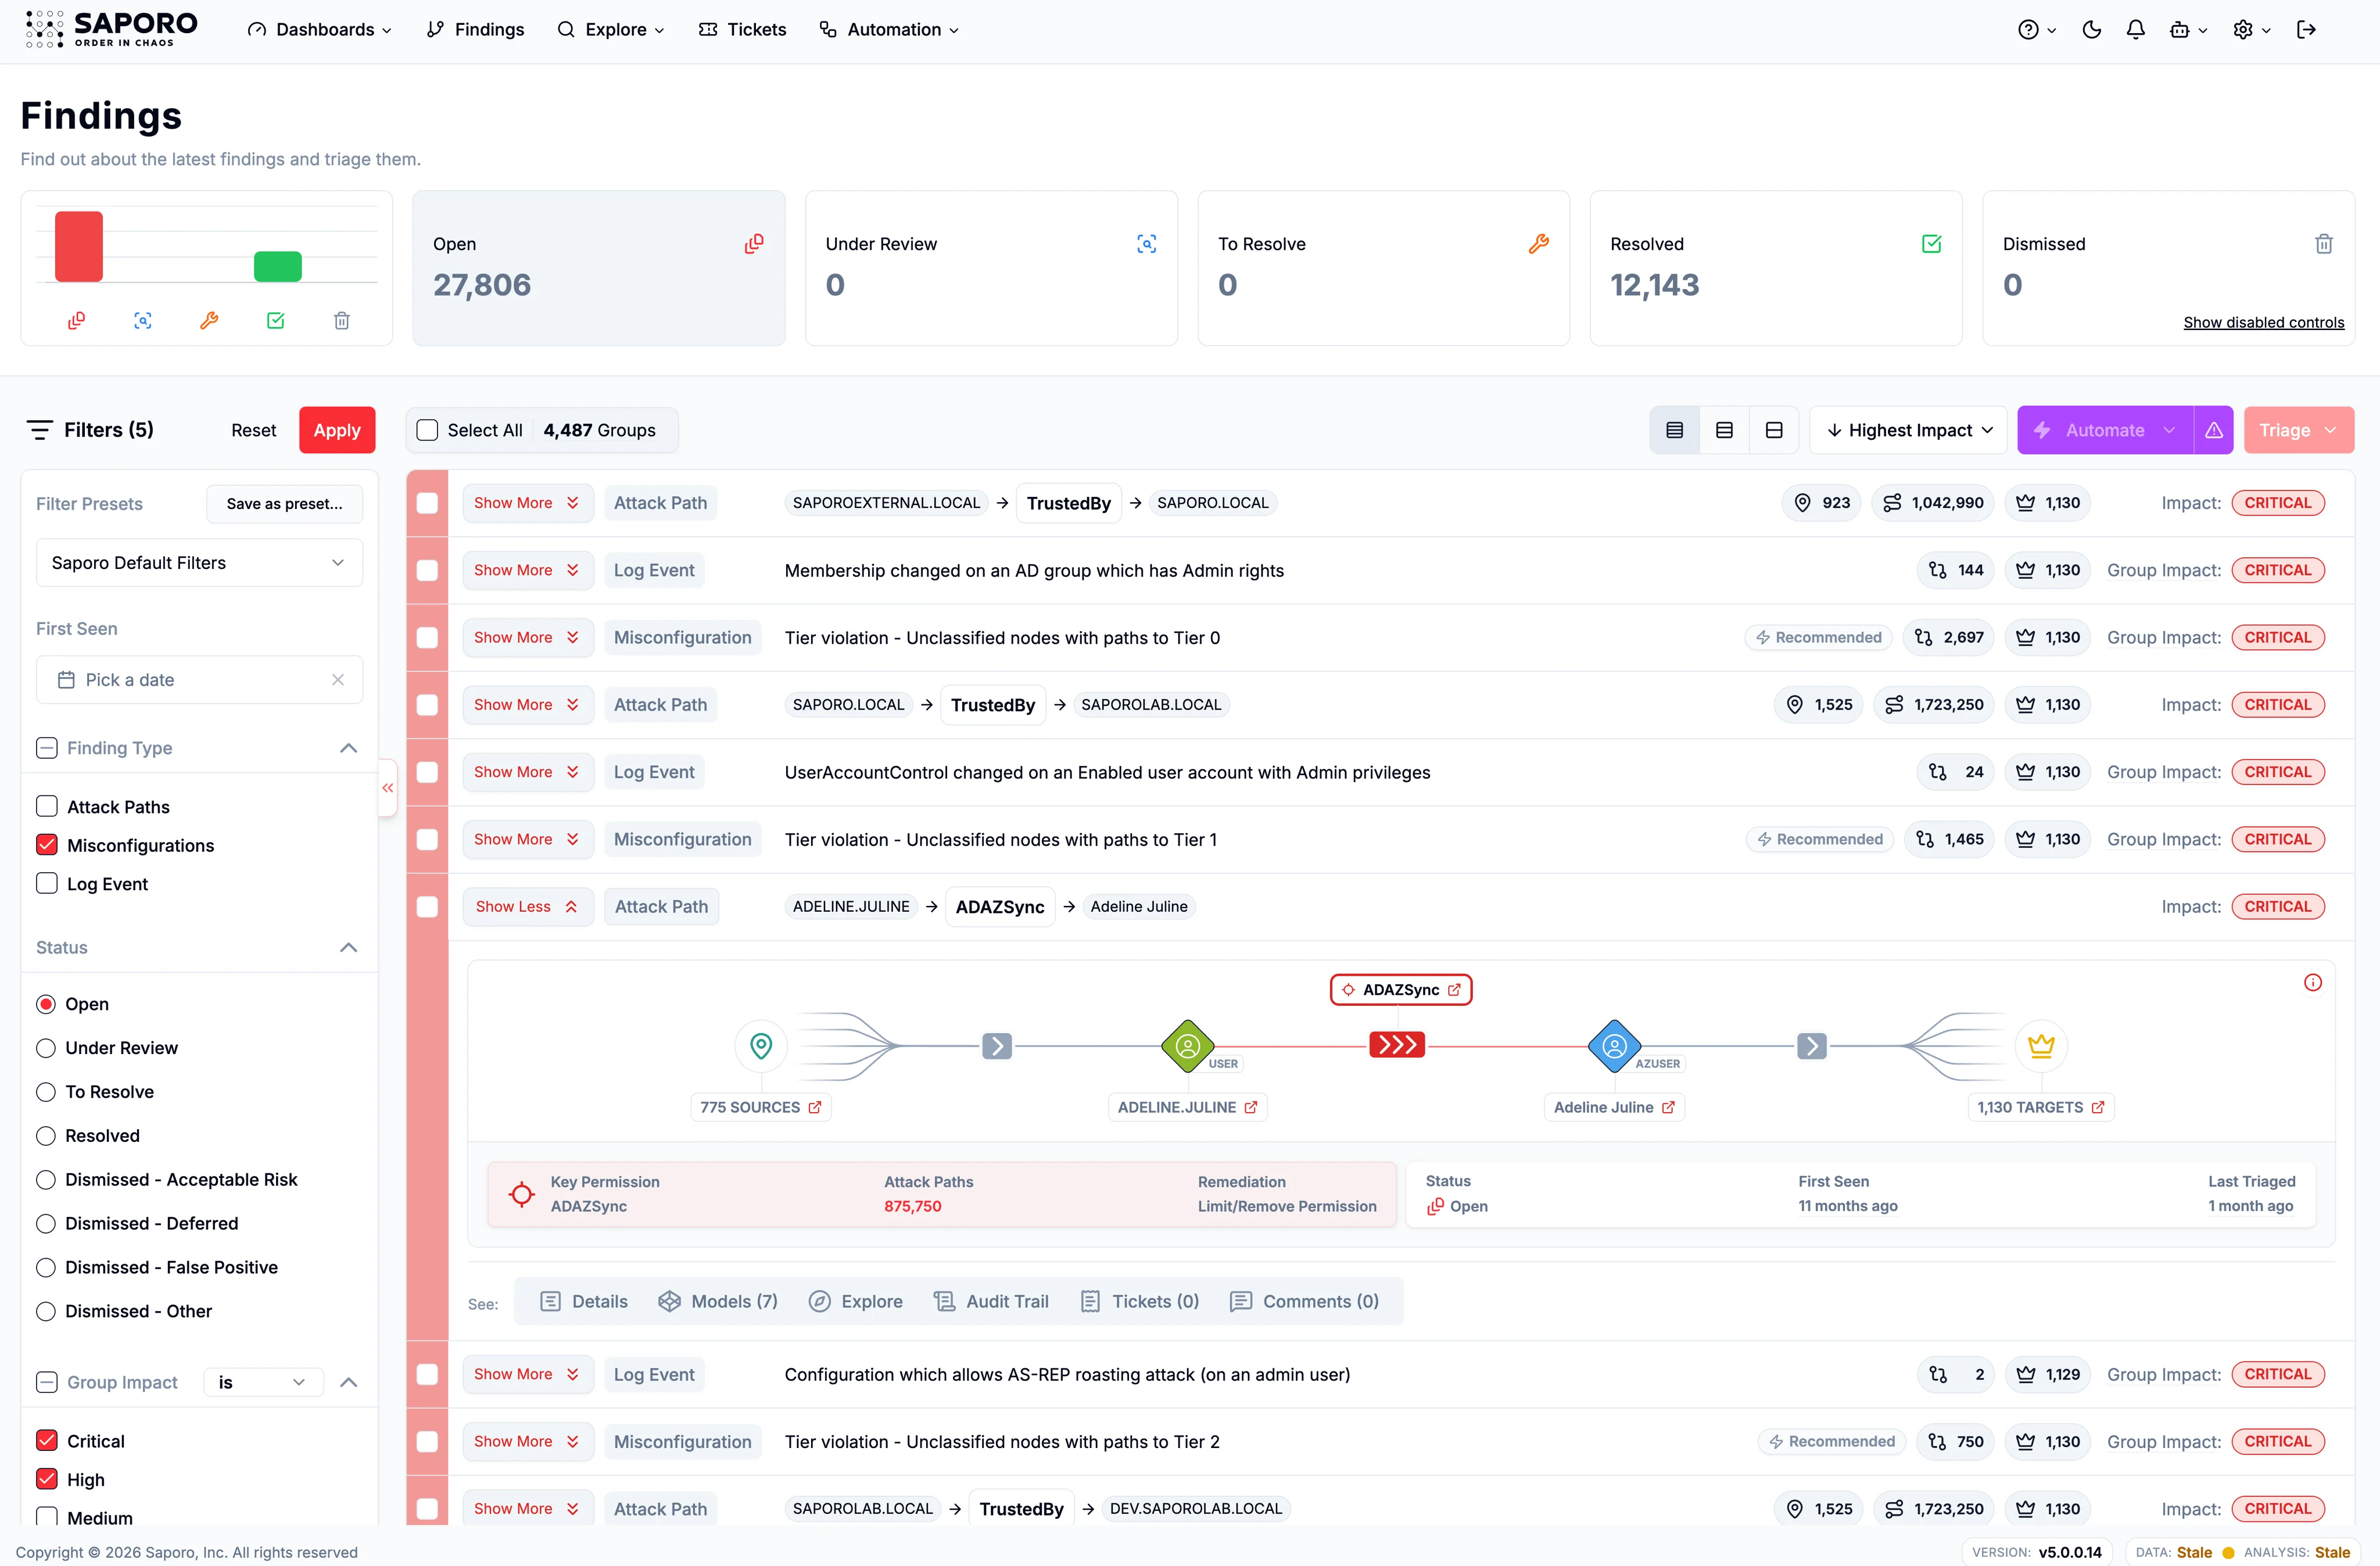
Saporo Inventory listing the nodes collected from Microsoft Active Directory, Active Directory Certificate Services, Azure, Entra ID and Microsoft 365, Windows Local, and SMB Shares, with counts for each source, in an example environment
Inventory / Connected identity sourcesFocused product view. Example environment and data.

One model, multiple outcomes

One exposure model. Six ways to reduce risk.

Unified Identity Visibility

Unify human and non-human identity exposure across on-premises and cloud in one graph.

Explore solution

Attack Path Reduction

Identify critical chokepoints where one targeted change can remove many attack paths to critical assets.

Explore solution

Tiering & Segmentation

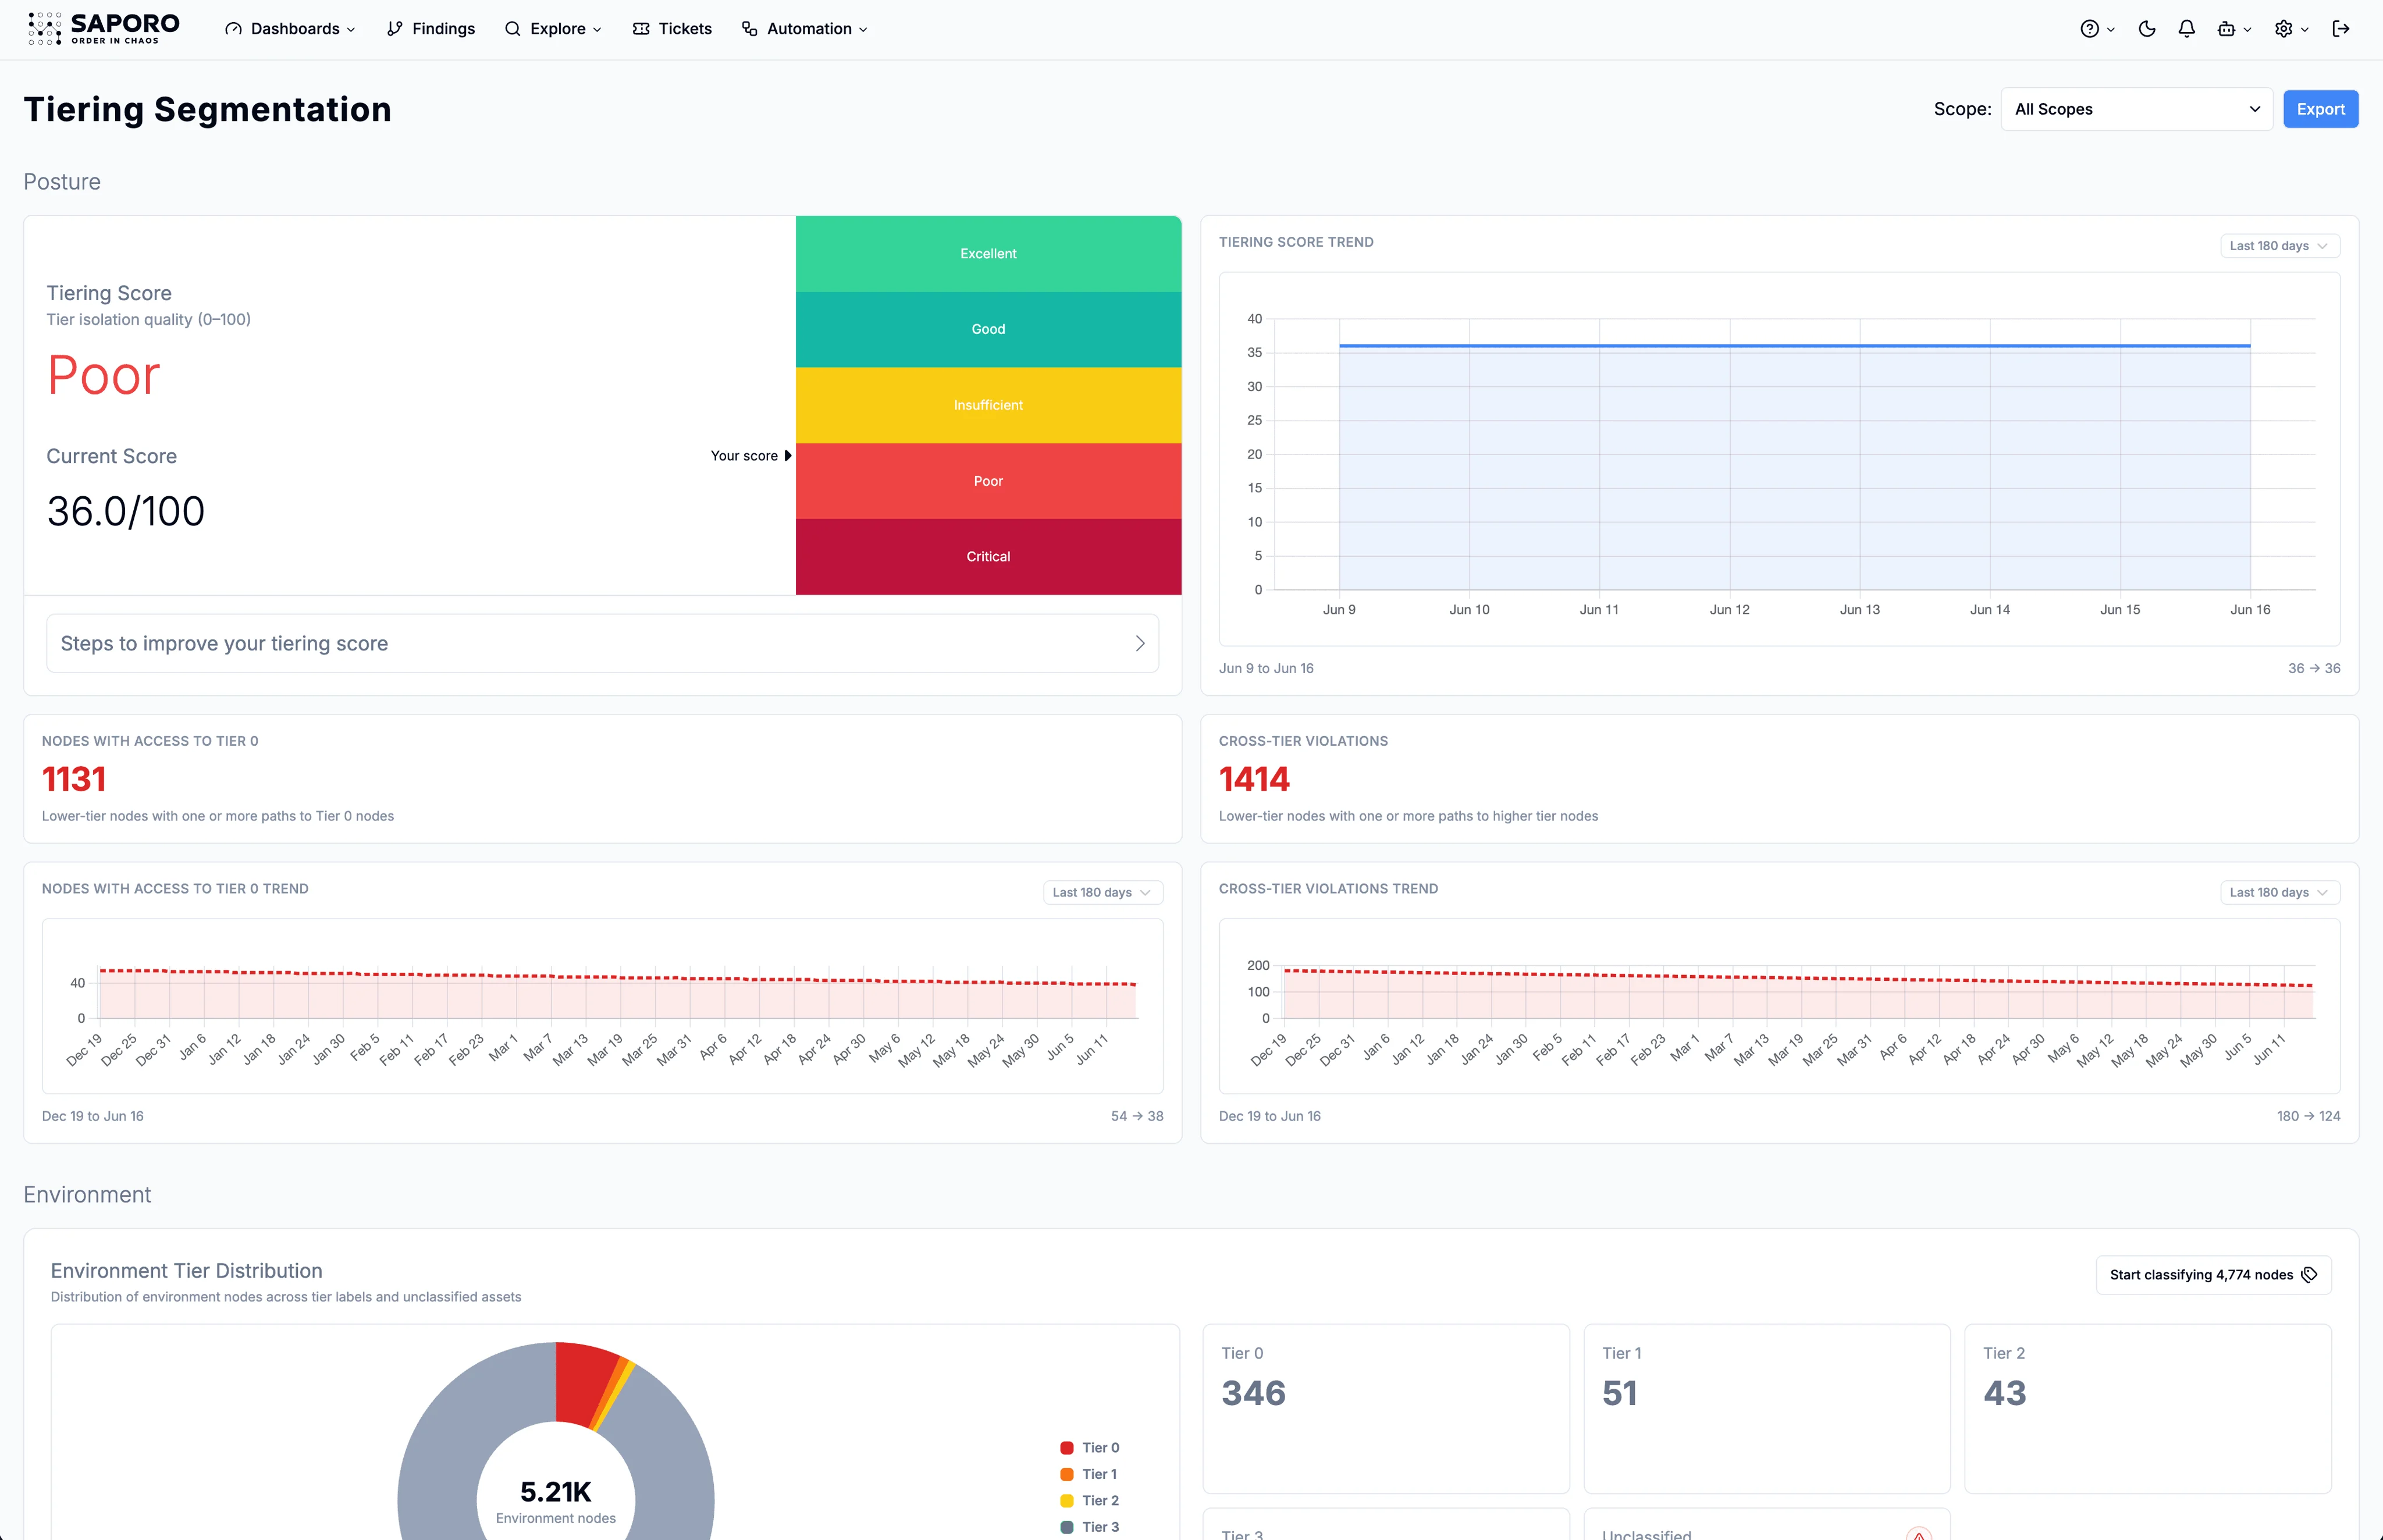
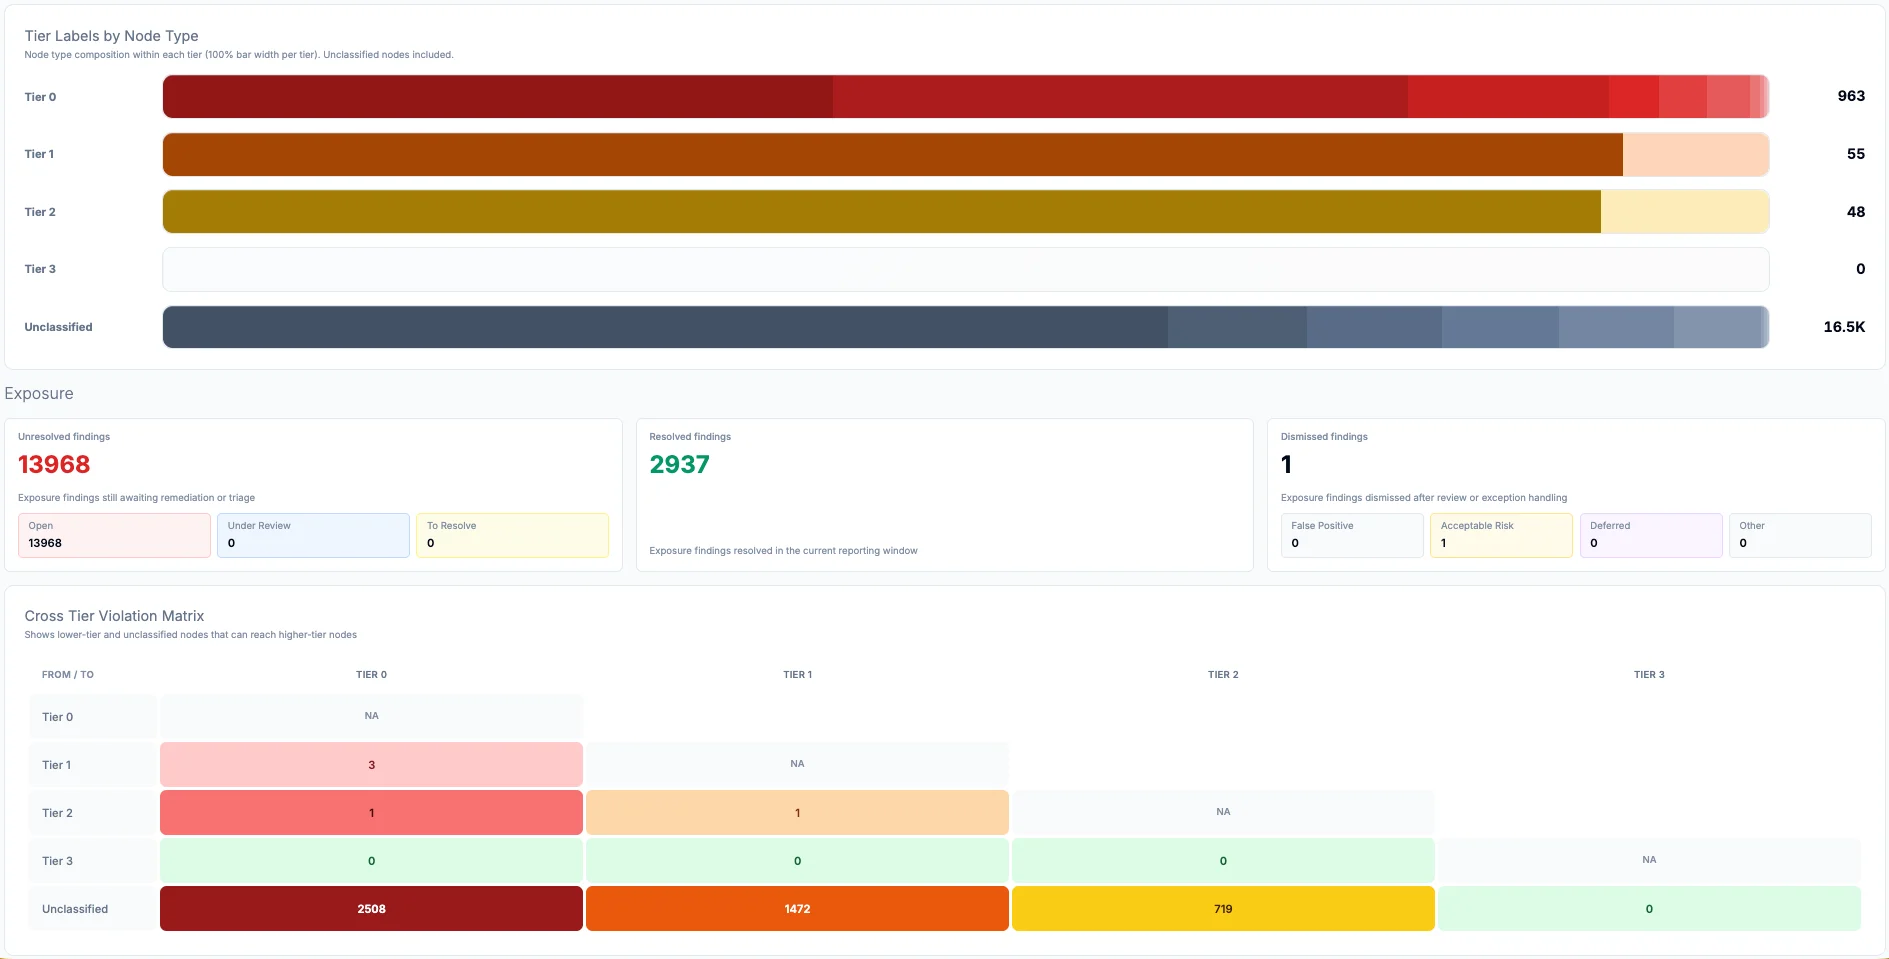
Apply a consistent tiering model across identities to define boundaries around privileged identities and critical systems.

Explore solution

Compliance Readiness

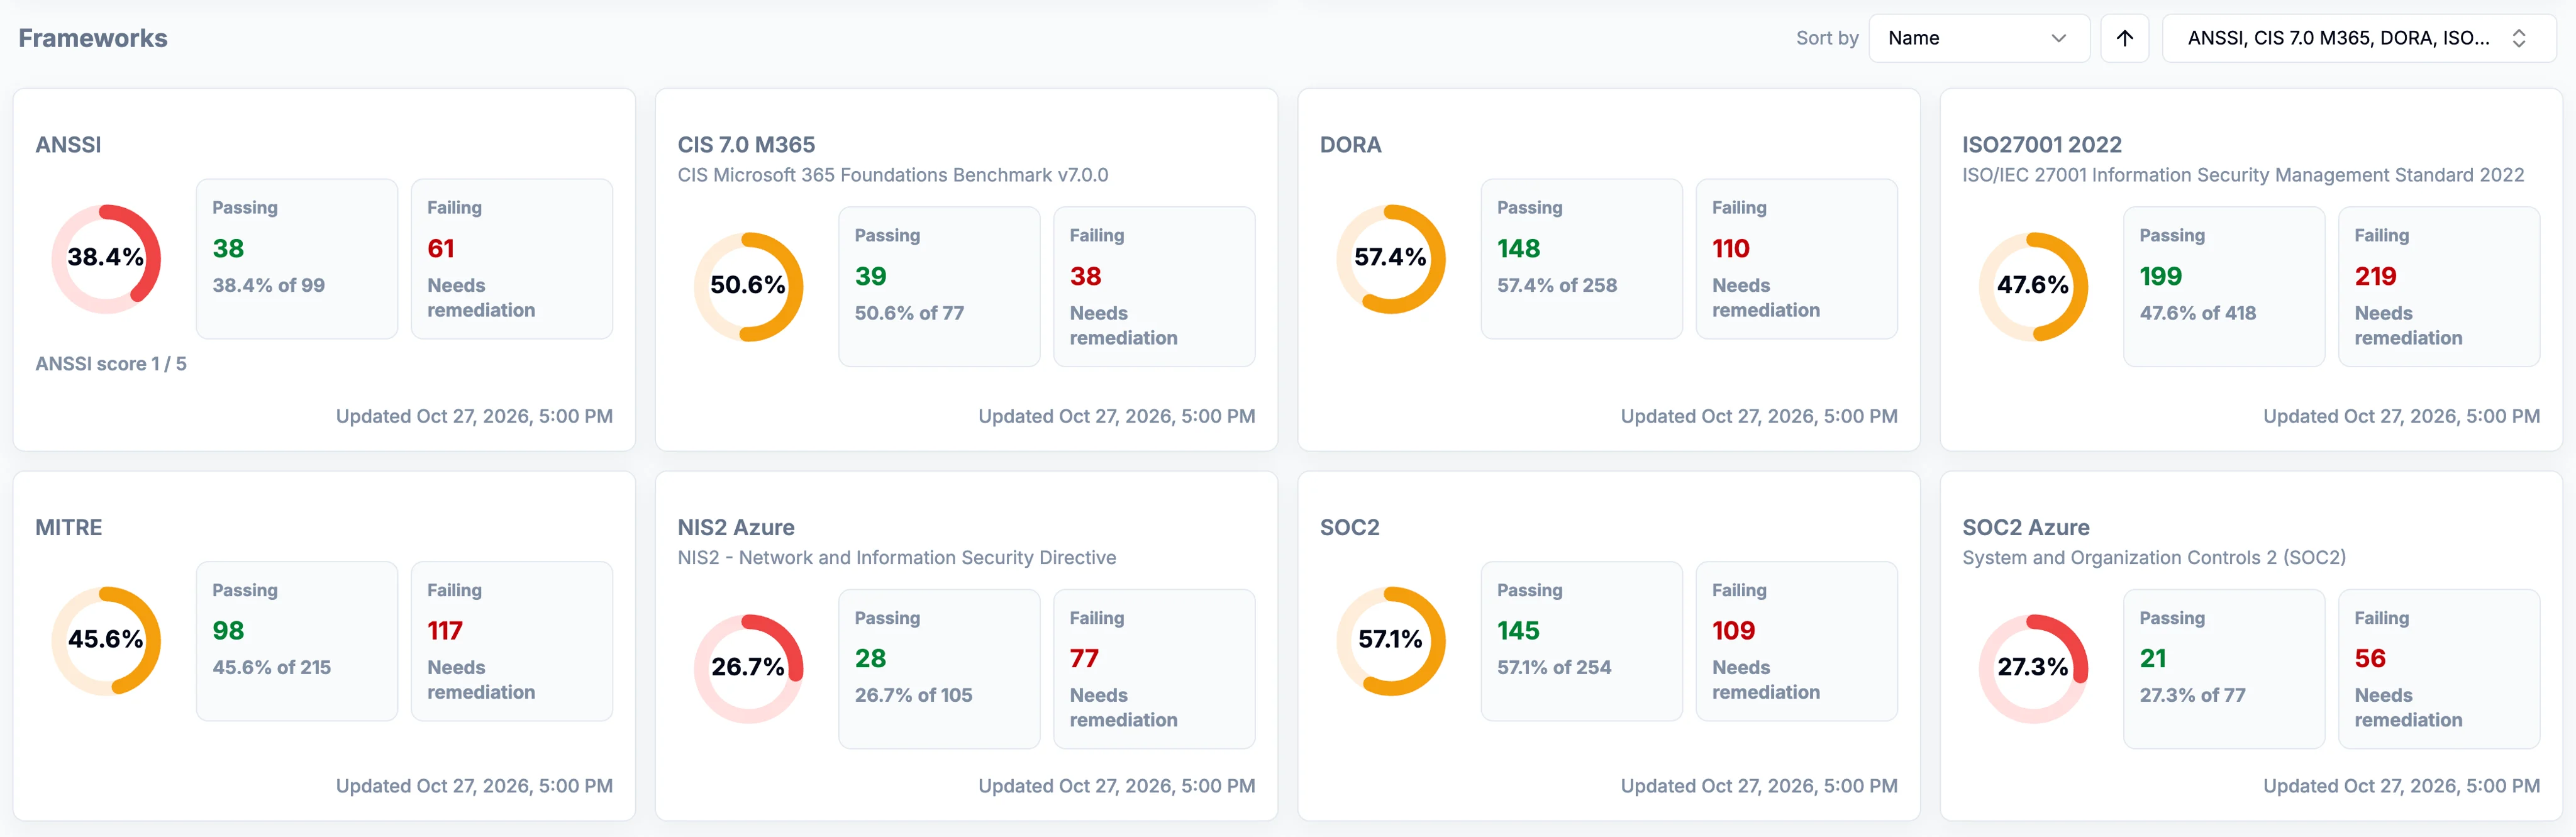
Map misconfiguration findings to 40+ framework versions, including ANSSI, NIS2, MITRE, and ISO 27001.

Explore solution

Hardening Automation

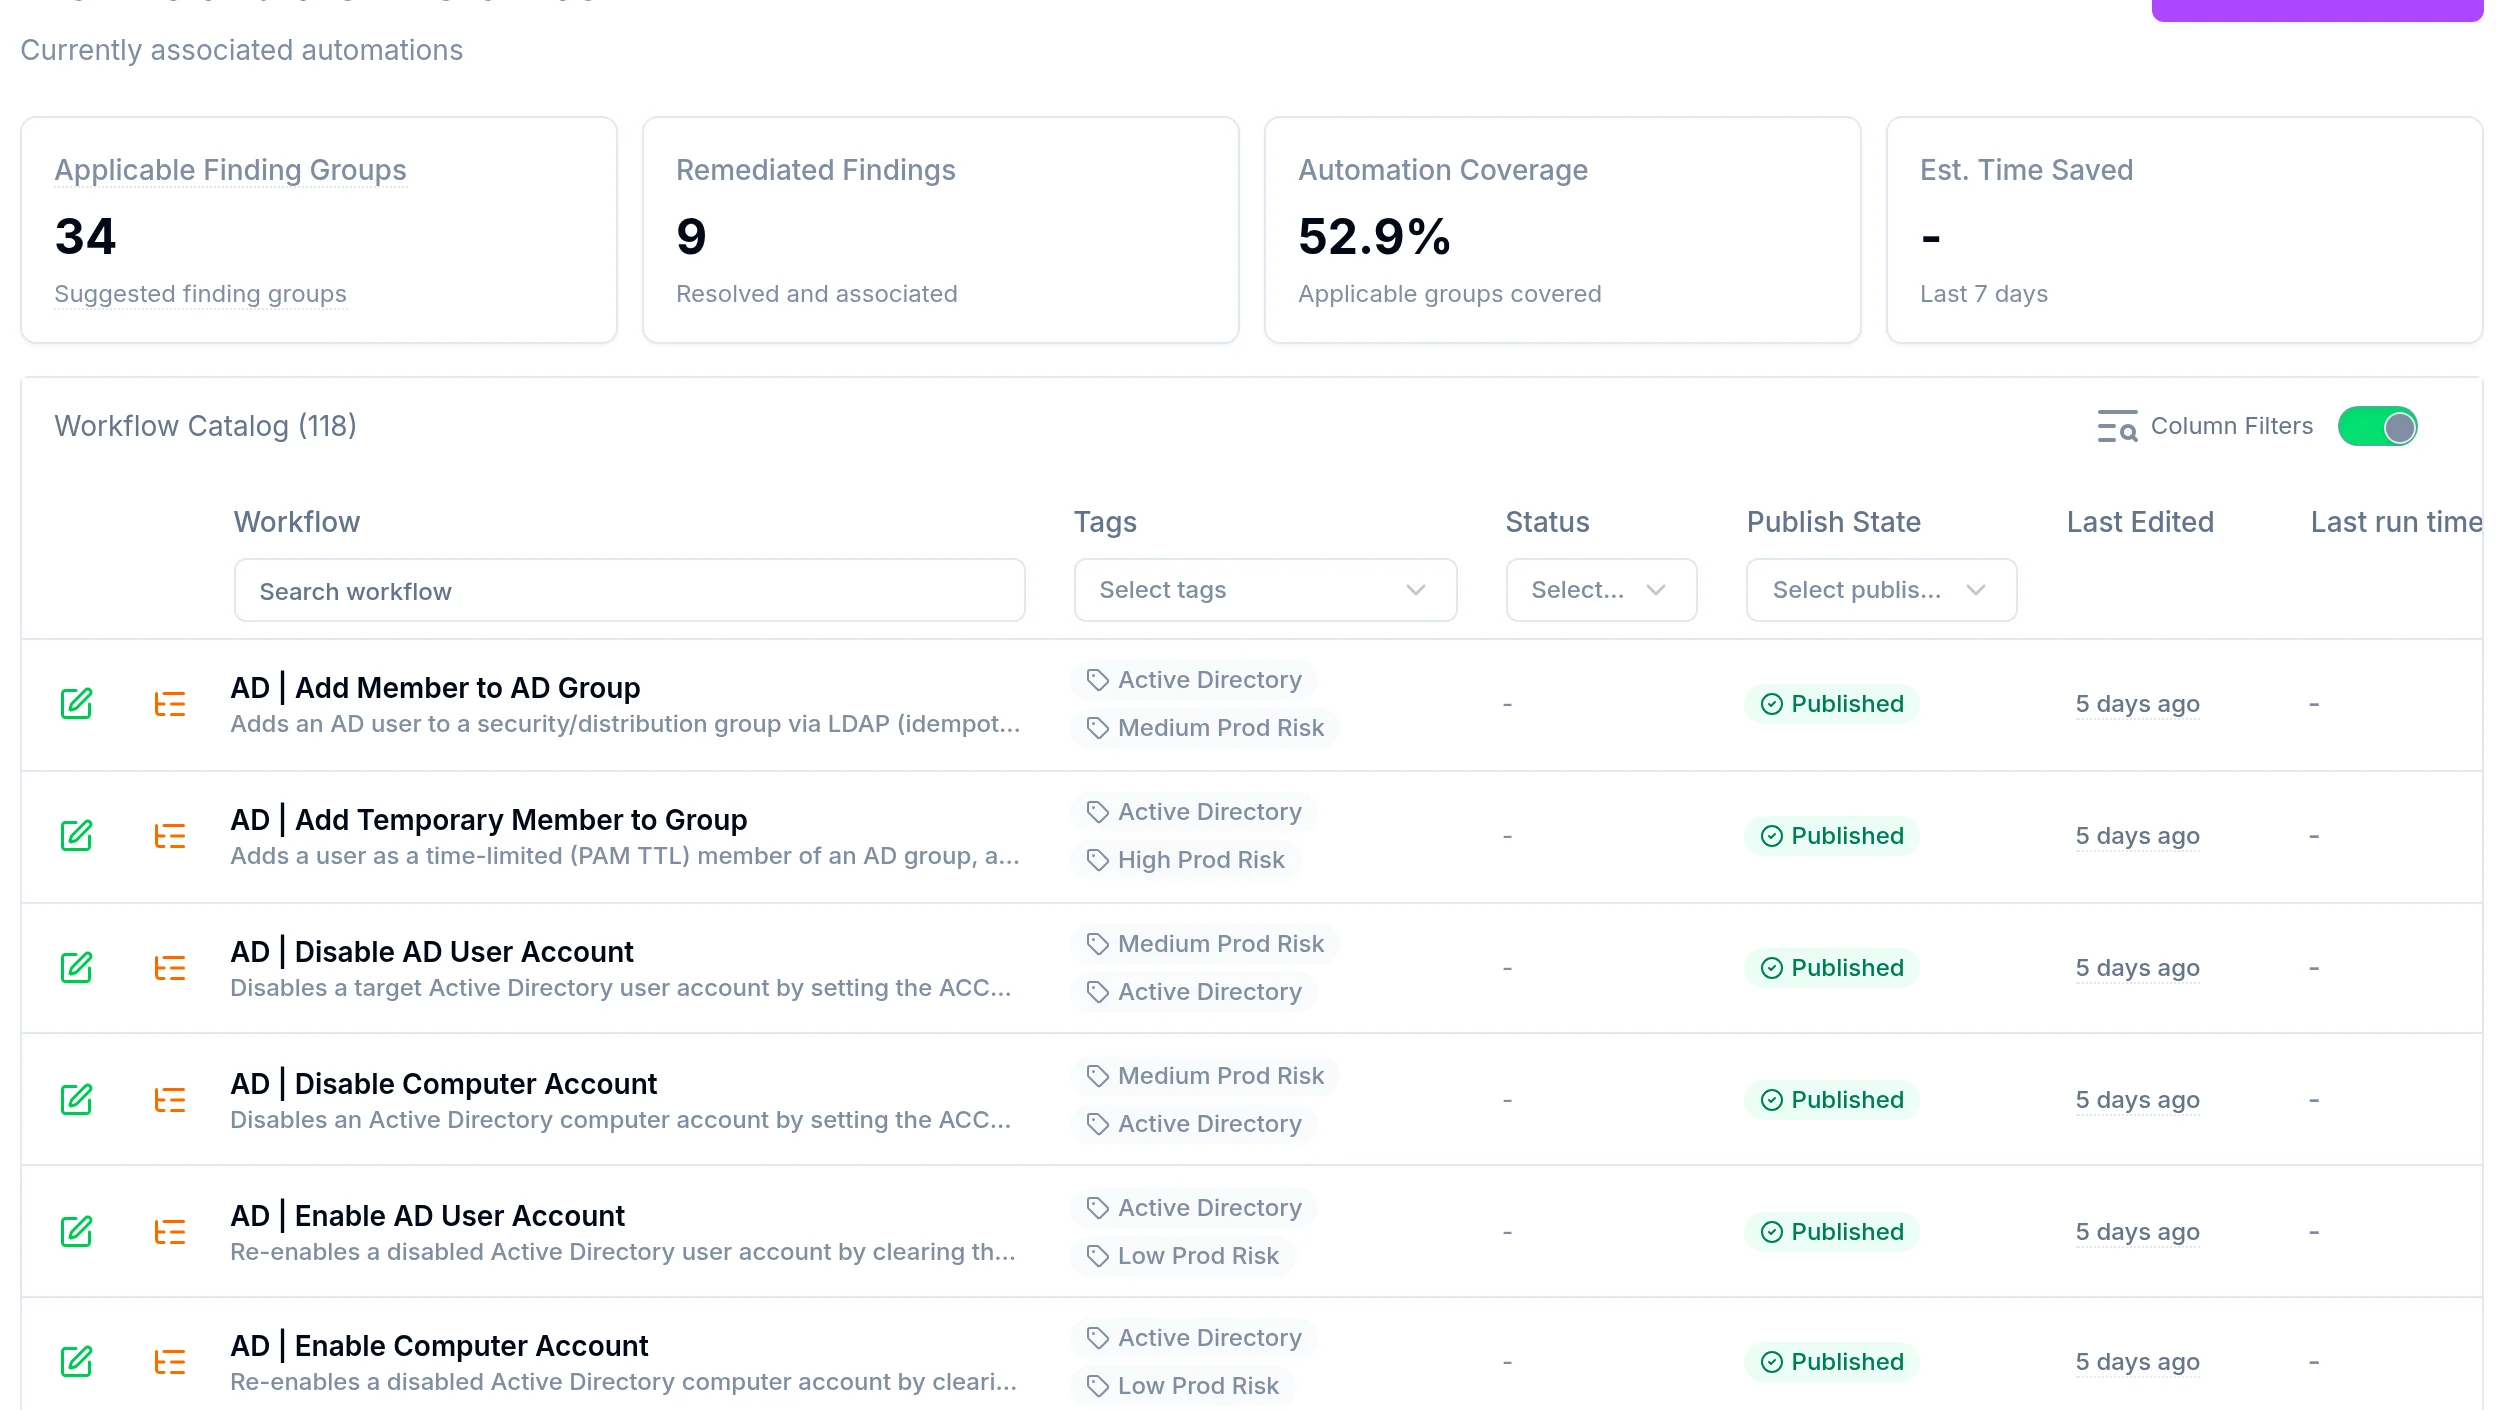
Turn remediation guidance into automated workflows, with approval steps that match your operational requirements.

Explore solution

Change & Event Monitoring

Track how attack opportunities change as identities, permissions, and configurations evolve.

Explore solution

A different operating model

From finding more problems to removing more risk

With Saporo

01

Attack opportunities connected in one identity graph

Without Saporo

Fragmented findings reviewed in isolation

With Saporo

02

Prioritize by reachability, blast radius, and impact

Without Saporo

Severity ratings with limited exposure context

With Saporo

03

Targeted chokepoint fixes reduce many attack paths

Without Saporo

Individual fixes with unclear impact on attacker reach

With Saporo

04

Guided remediation and governed automation

Without Saporo

Manual remediation across disconnected tools

With Saporo

05

Continuous exposure reduction as environments change

Without Saporo

Periodic assessments and growing backlogs

With Saporo

06

Resistance, control posture, and time savings tracked

Without Saporo

Progress measured by findings and tasks closed

Measure what changed

Turn exposure reduction into evidence

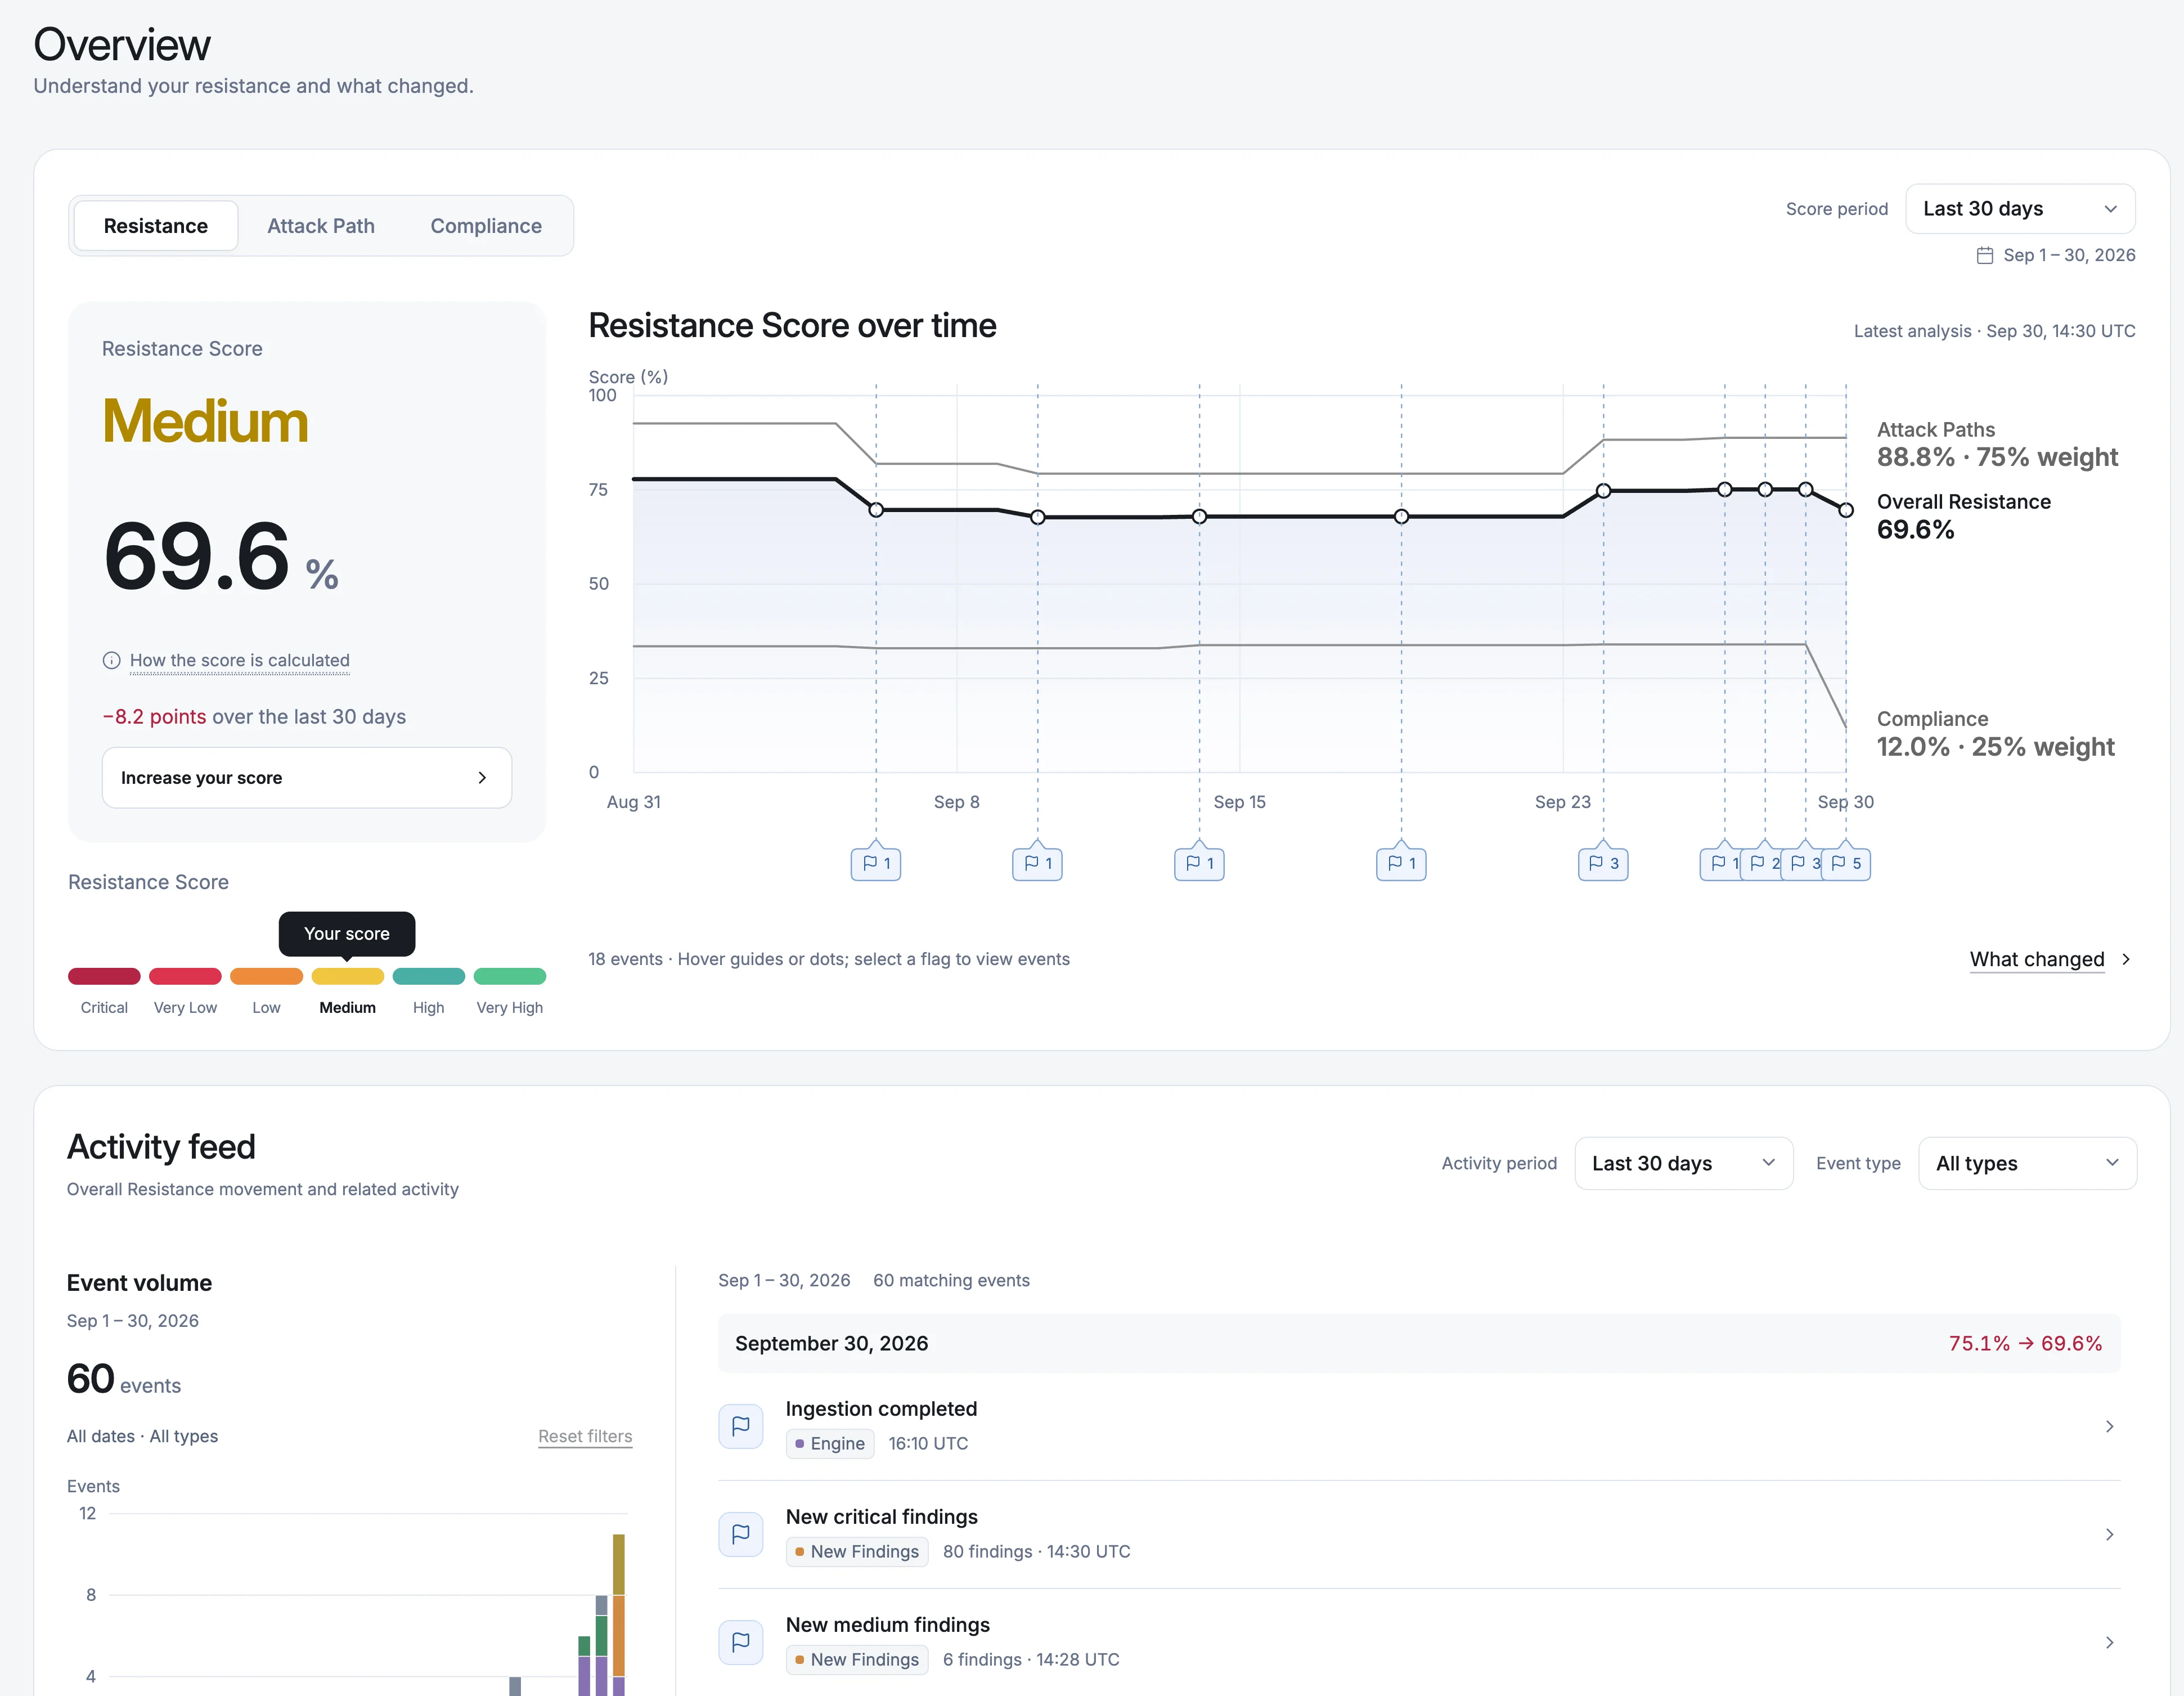
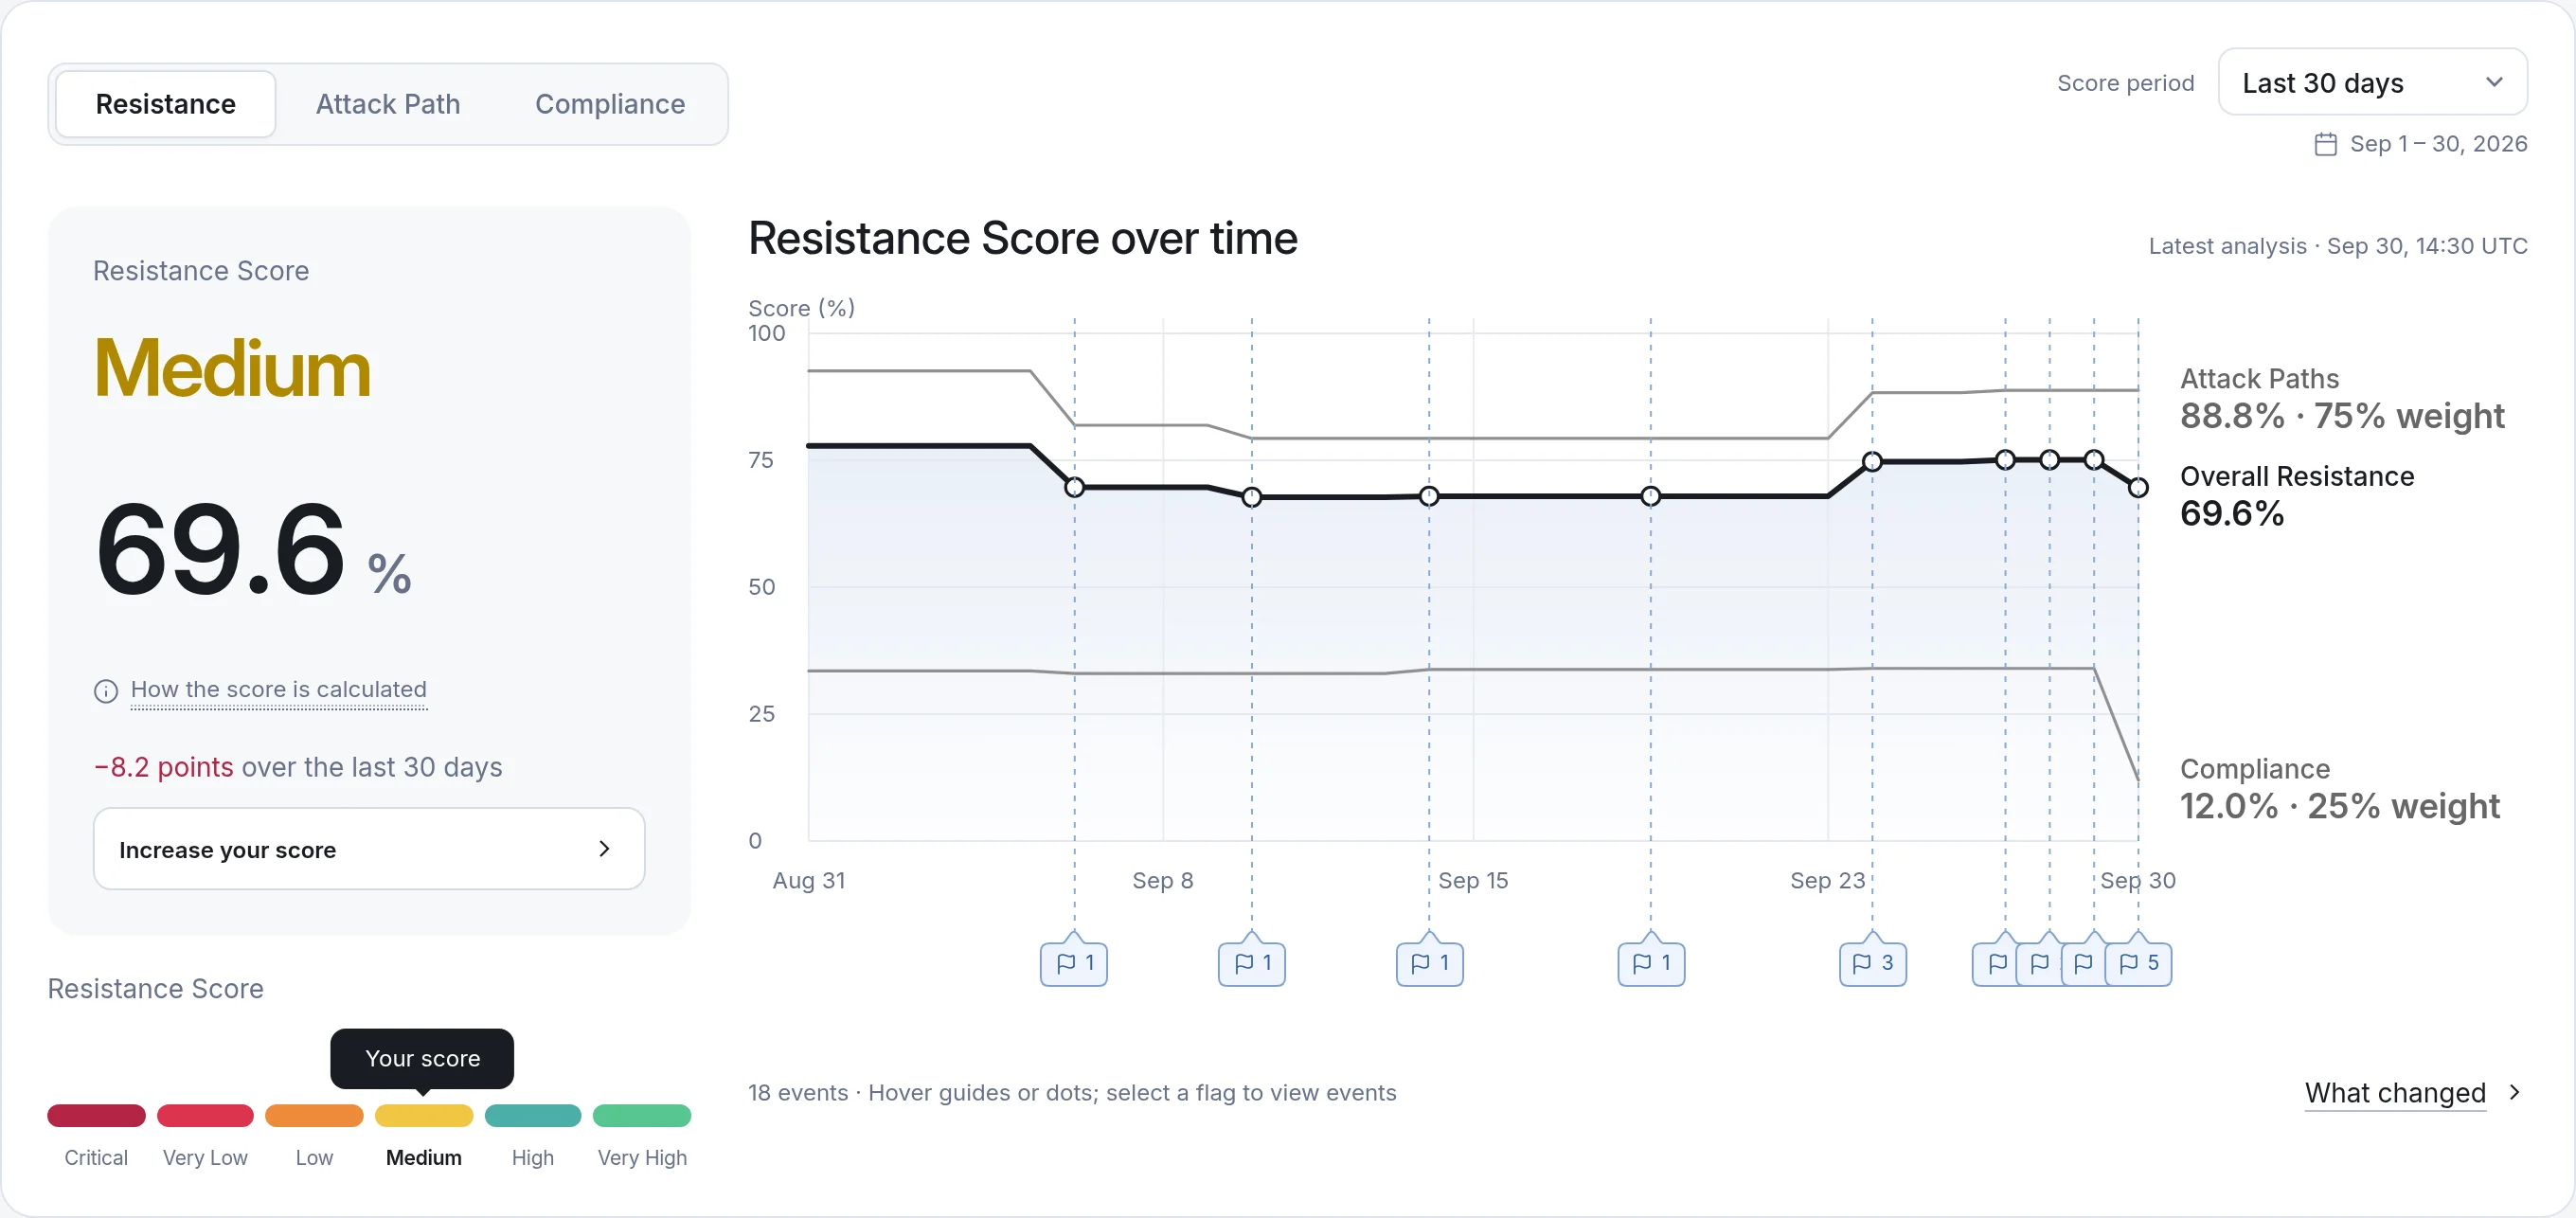
Show how your actions change identity exposure over time. Use Resistance Score, compliance and tiering results, and remediation trends to track improvement and identify regressions. Give security teams and leadership a shared view of what improved, what remains exposed, and where to focus next.

Attack paths removed
Critical assets protected
Posture improvement
Remediation progress

Reduce identity exposure before it becomes an attack

Book a demo