GOOGLE WORKSPACE & GCP EXPOSURE

Reduce identity exposure across Google Workspace & GCP

Uncover excessive permissions, misconfigurations, and attack opportunities across Google Workspace and Google Cloud.

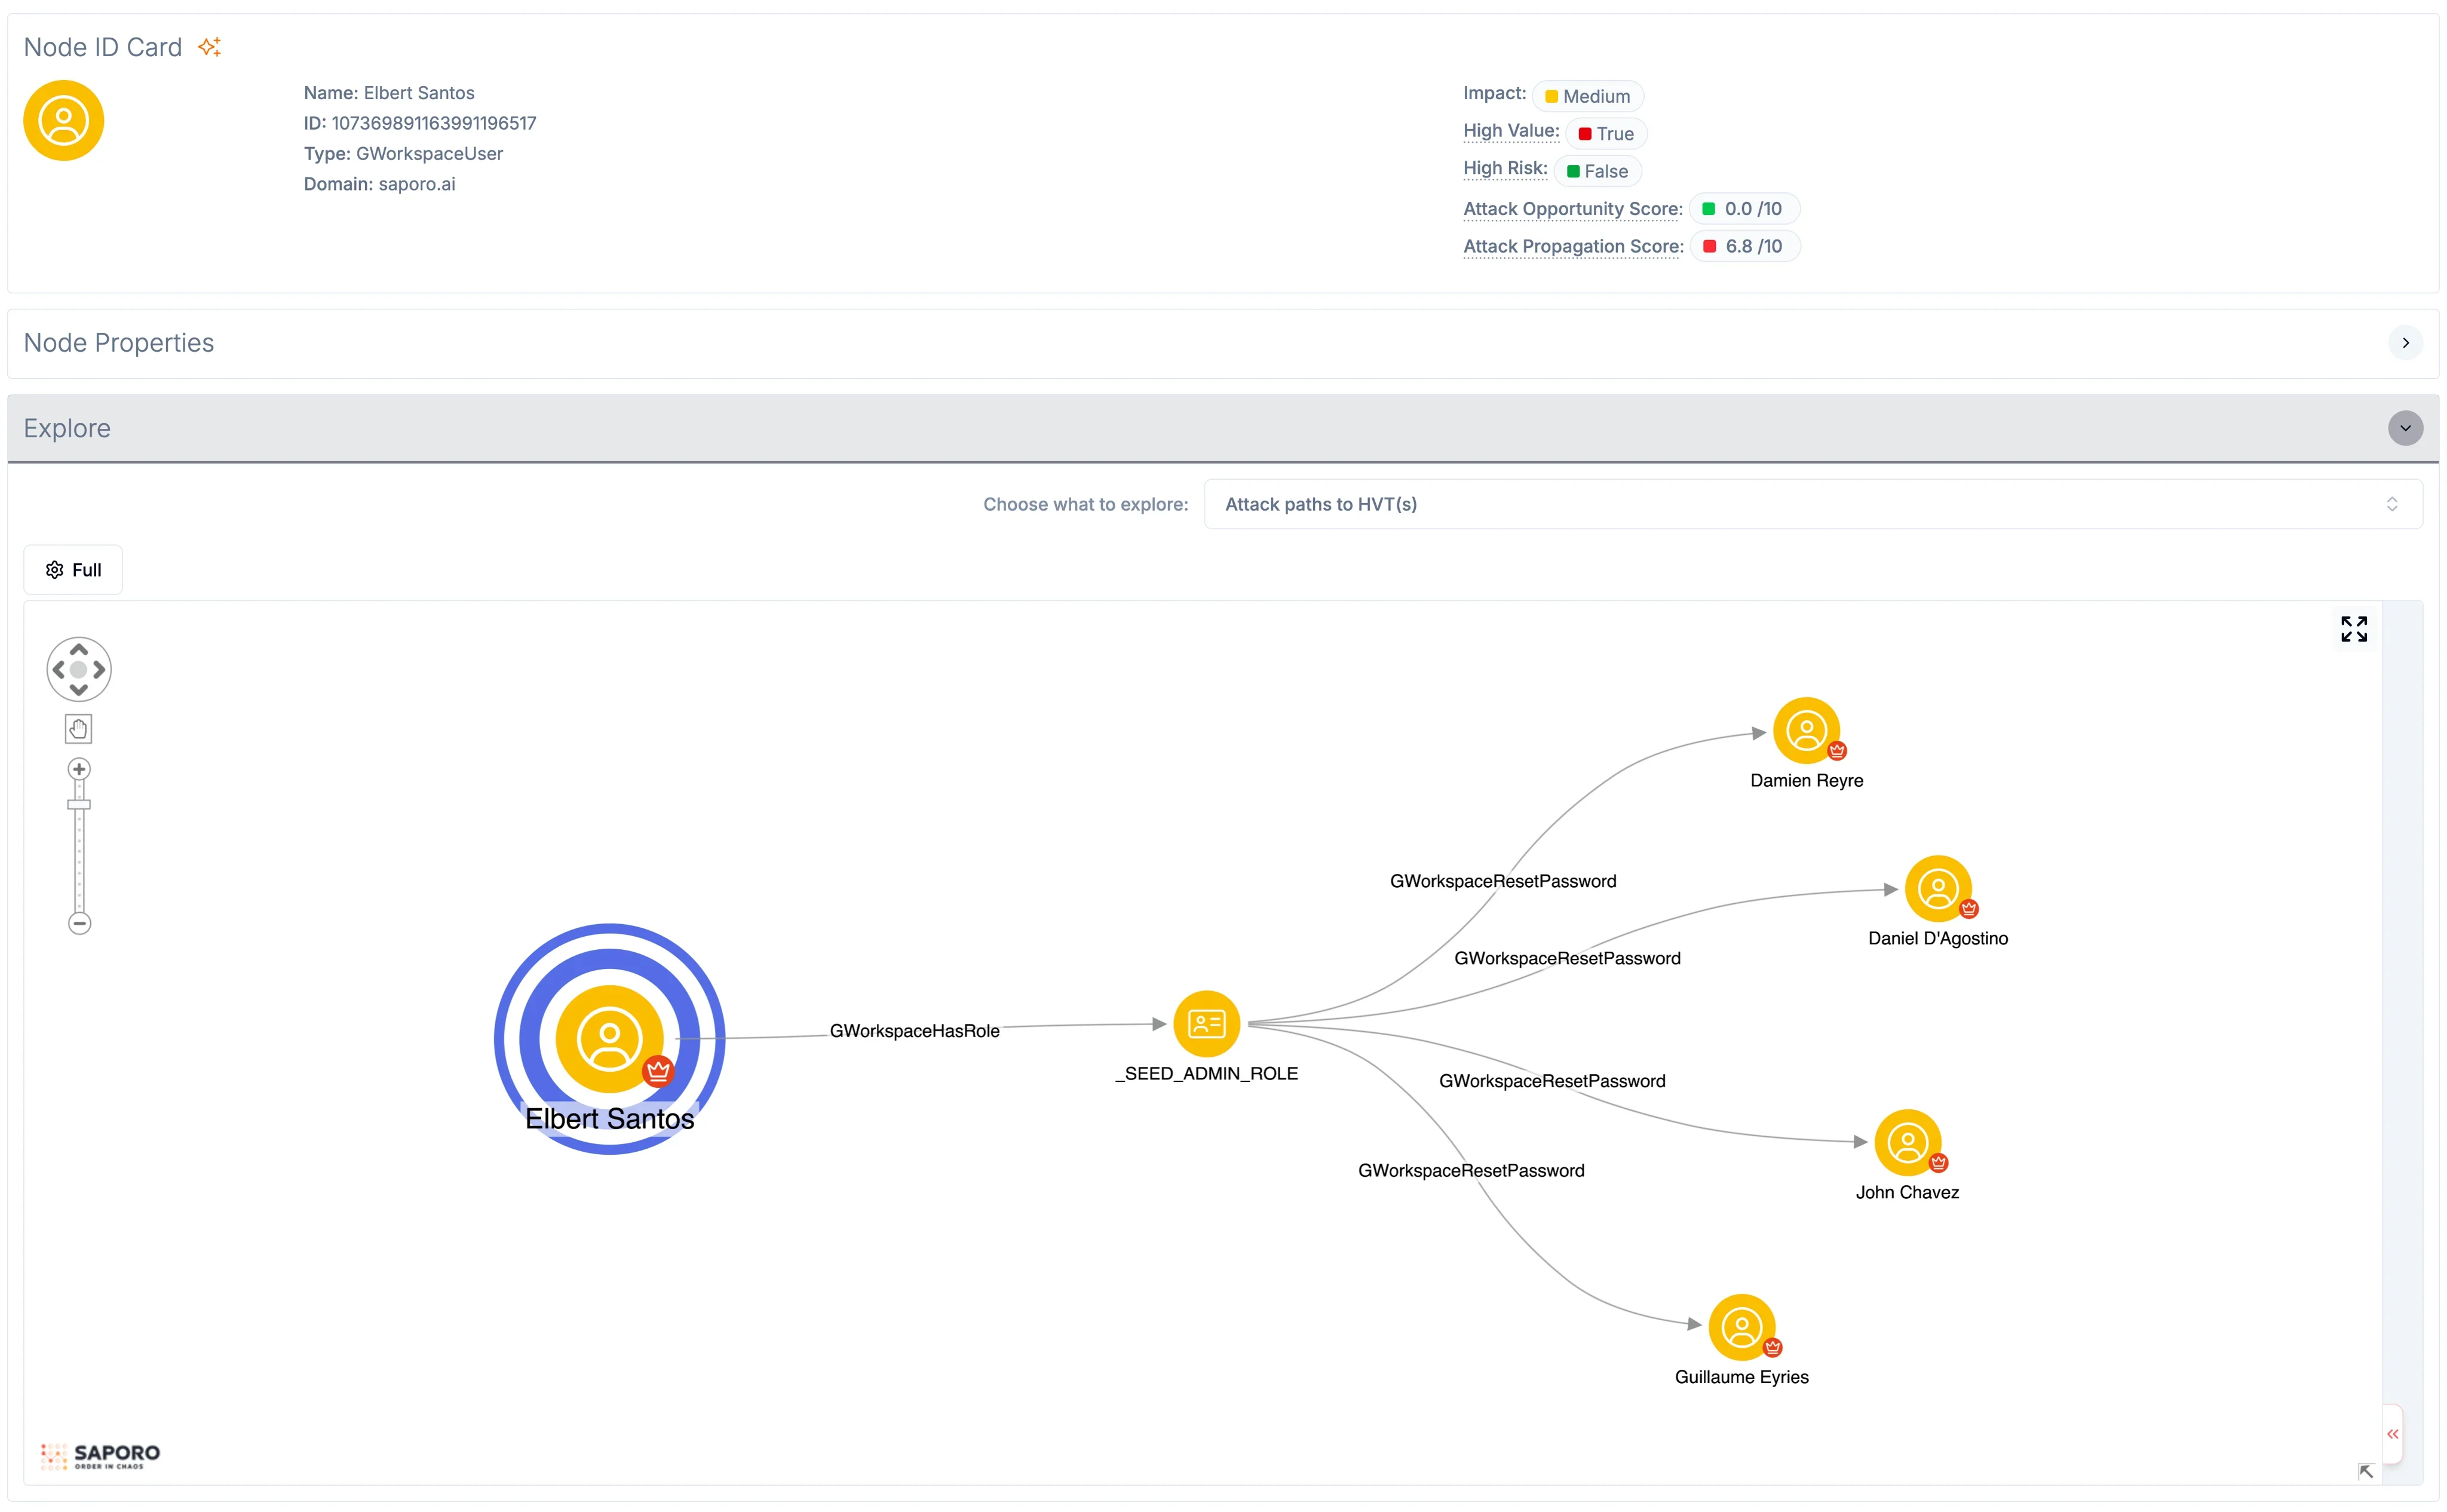
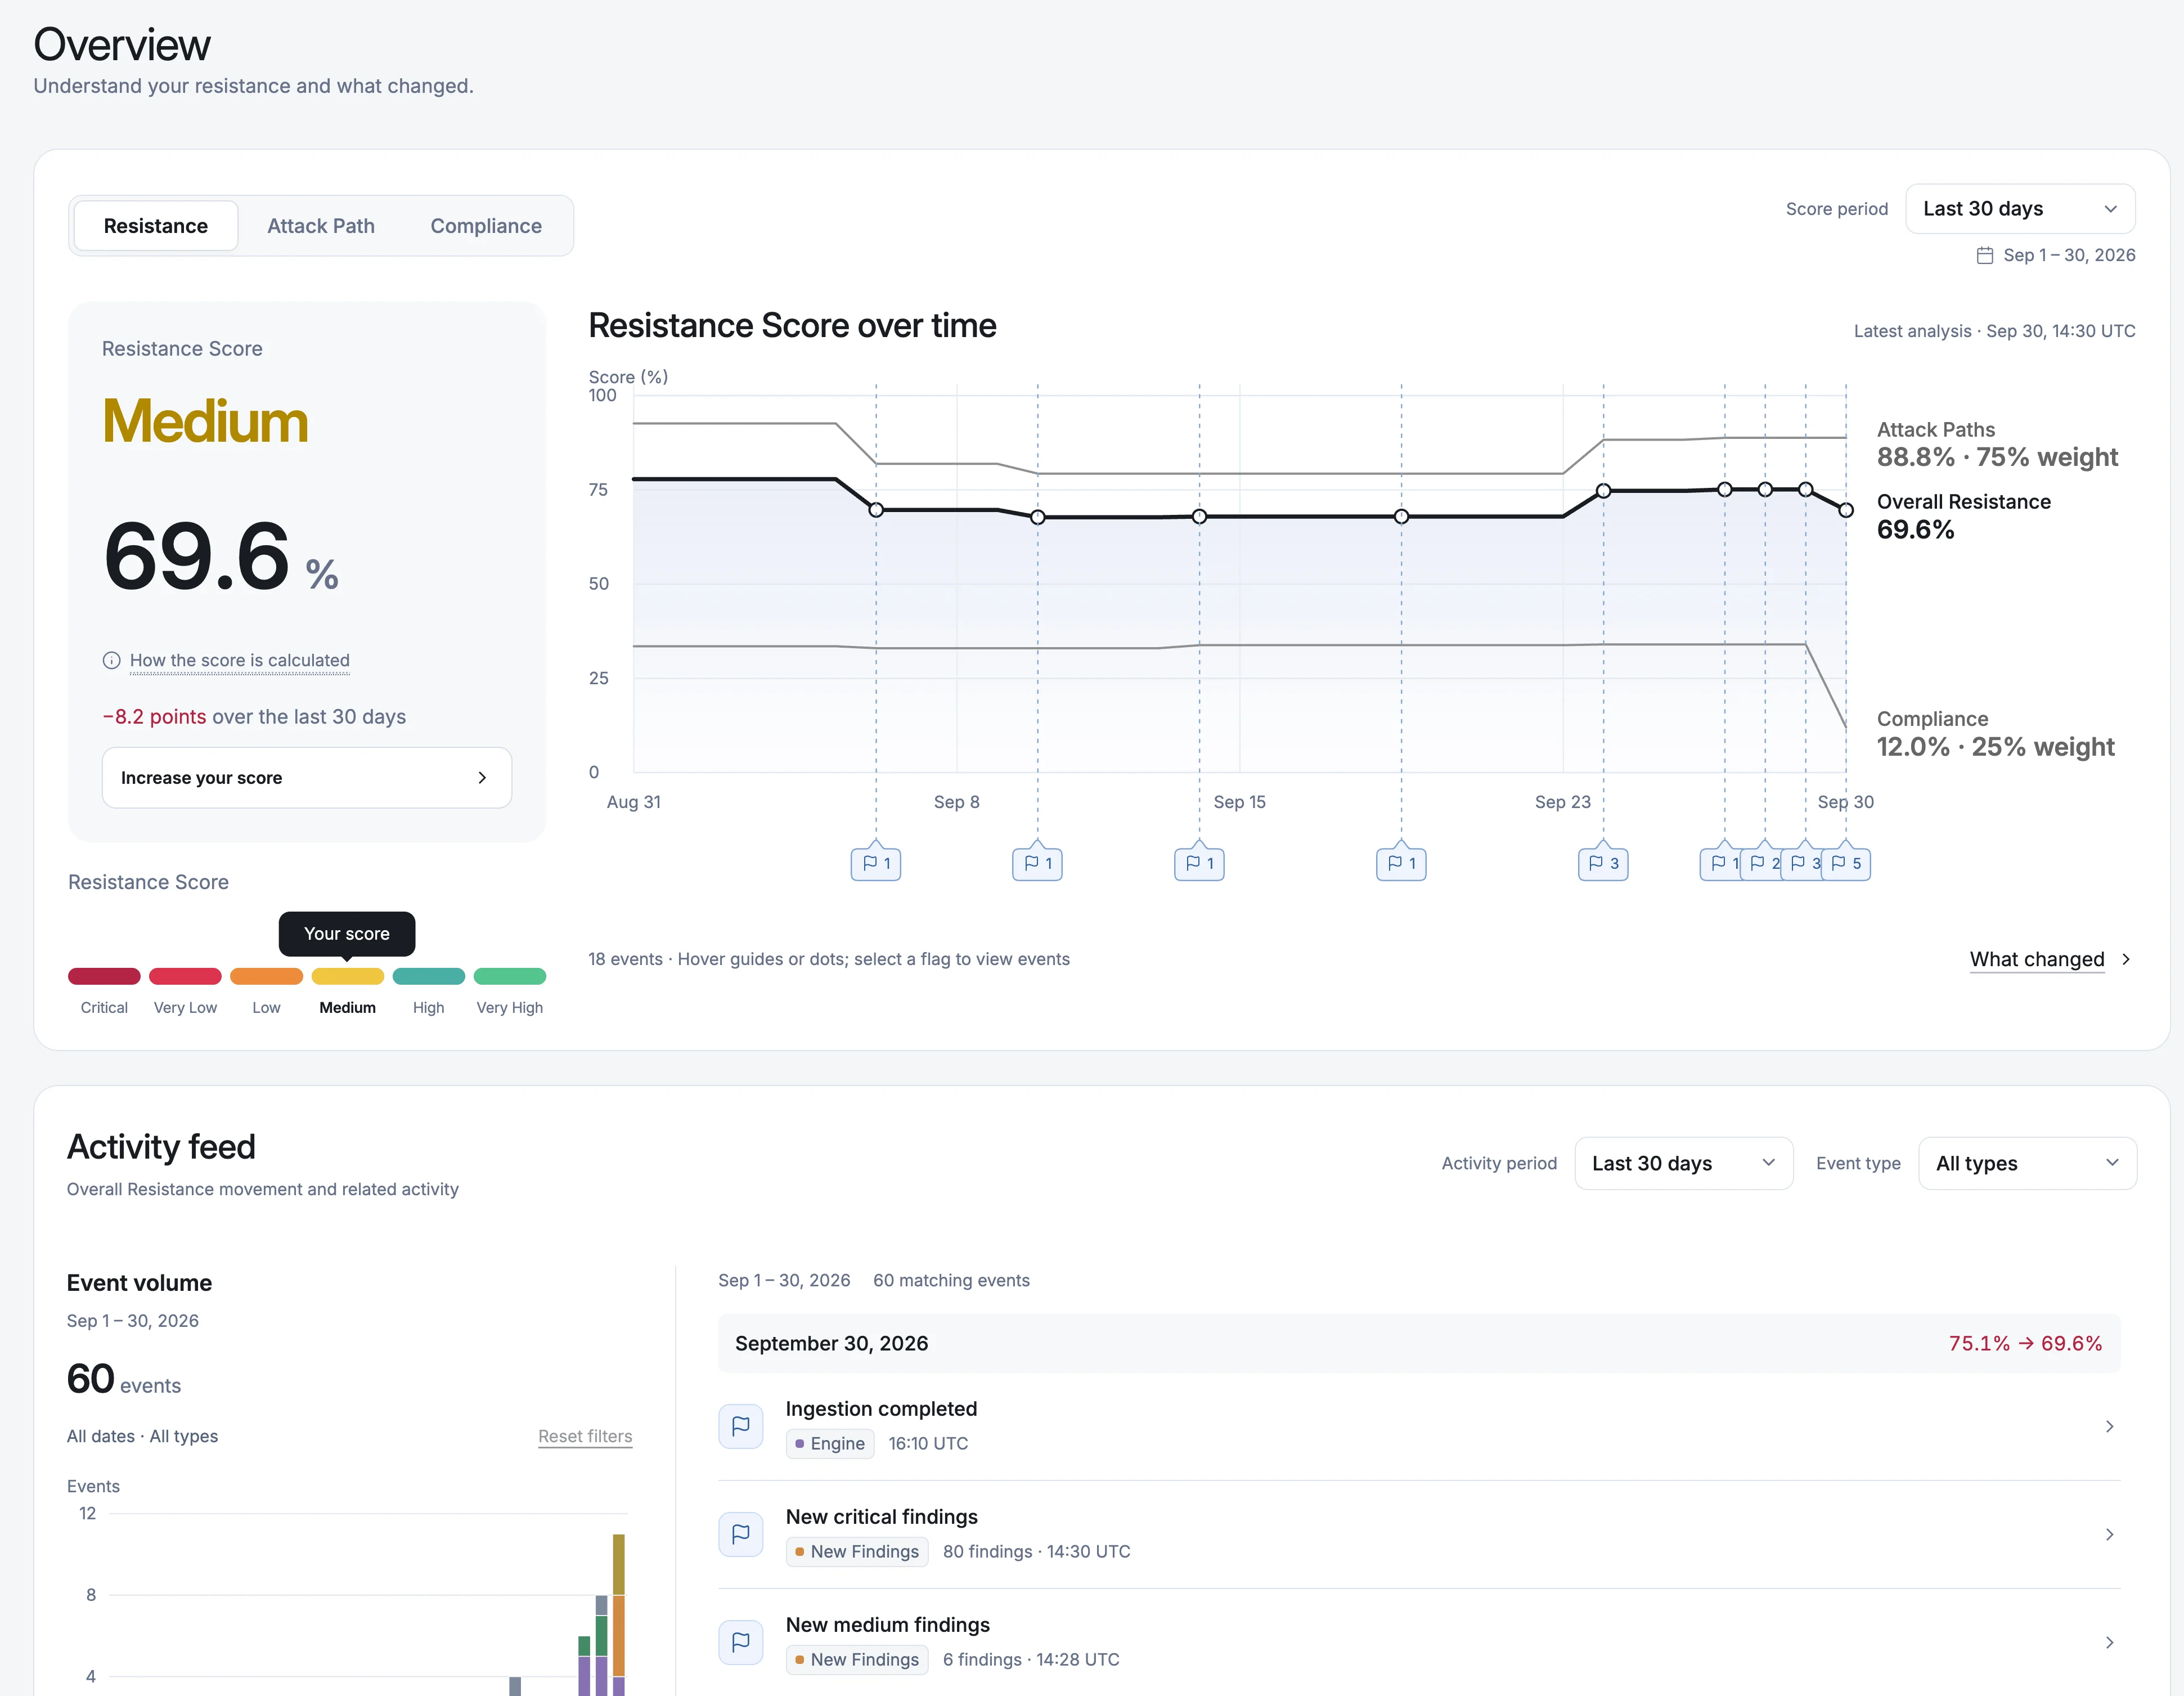
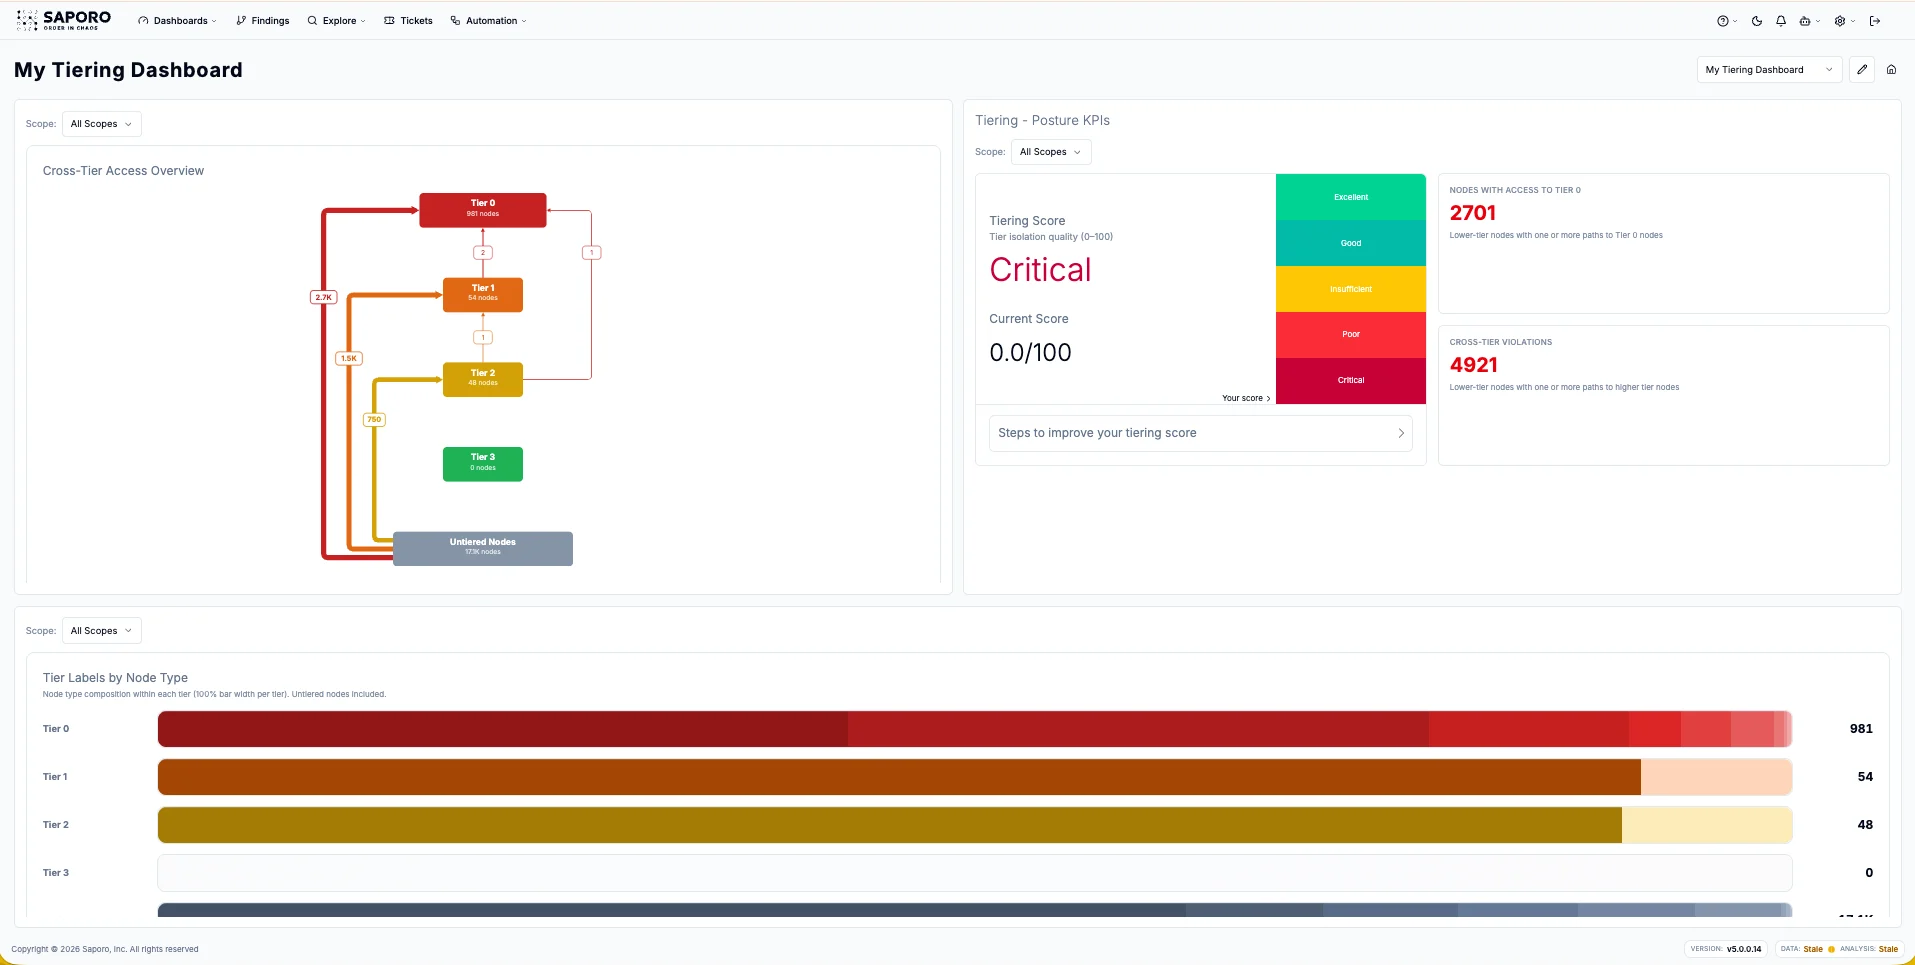
Saporo connects users, groups, admin roles, service accounts, and cloud resources in one graph to reveal how attackers could reach critical assets and which changes reduce the most exposure. Analyze either environment independently or connect both for a broader view.

Google WorkspaceGoogle Cloud
  • Users & groups
  • Projects
  • Admin roles
  • Service accounts
  • IAM roles
  • Resources

83% of investigated incidents in major cloud and SaaS environments involved threat actors exploiting identity issues for initial access.

Source: Google Cloud Threat Horizons Report, H1 2026

GOOGLE WORKSPACE & GCP Q&A

What security teams ask about Google identity exposure

Workspace identities and groups can shape access into Google Cloud. Connecting both environments helps reveal cross-service relationships and privilege paths that separate reviews may miss.

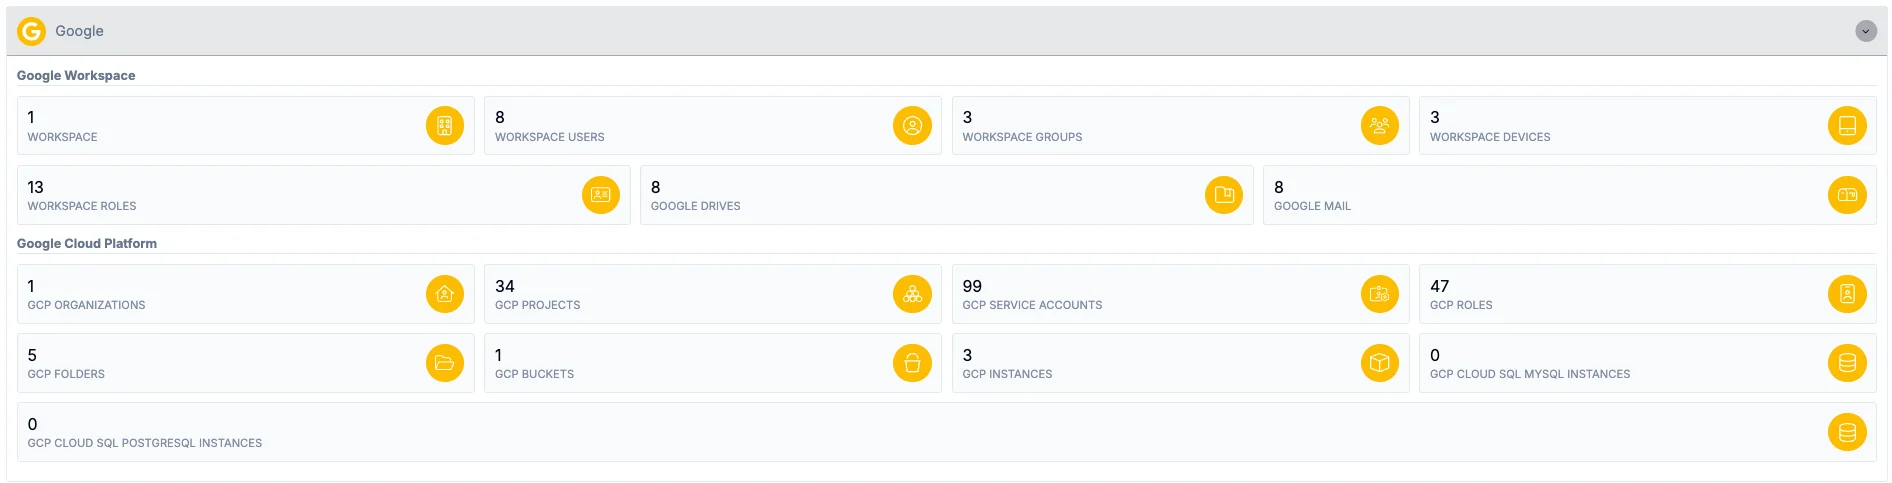
Saporo can connect Workspace users, groups, memberships, role assignments, managed devices, and Drive ownership context with the wider identity graph.

Saporo inventories organizations, folders, projects, service accounts, and supported resources, including Compute Engine instances, Cloud SQL instances, and Cloud Storage buckets. It connects these objects through supported IAM policy bindings and inherited access relationships.

Yes. Saporo identifies supported permissions that allow an identity to impersonate a Google Cloud service account and connects them to that account’s access. This reveals how a compromised identity could gain additional privileges and reach critical resources.

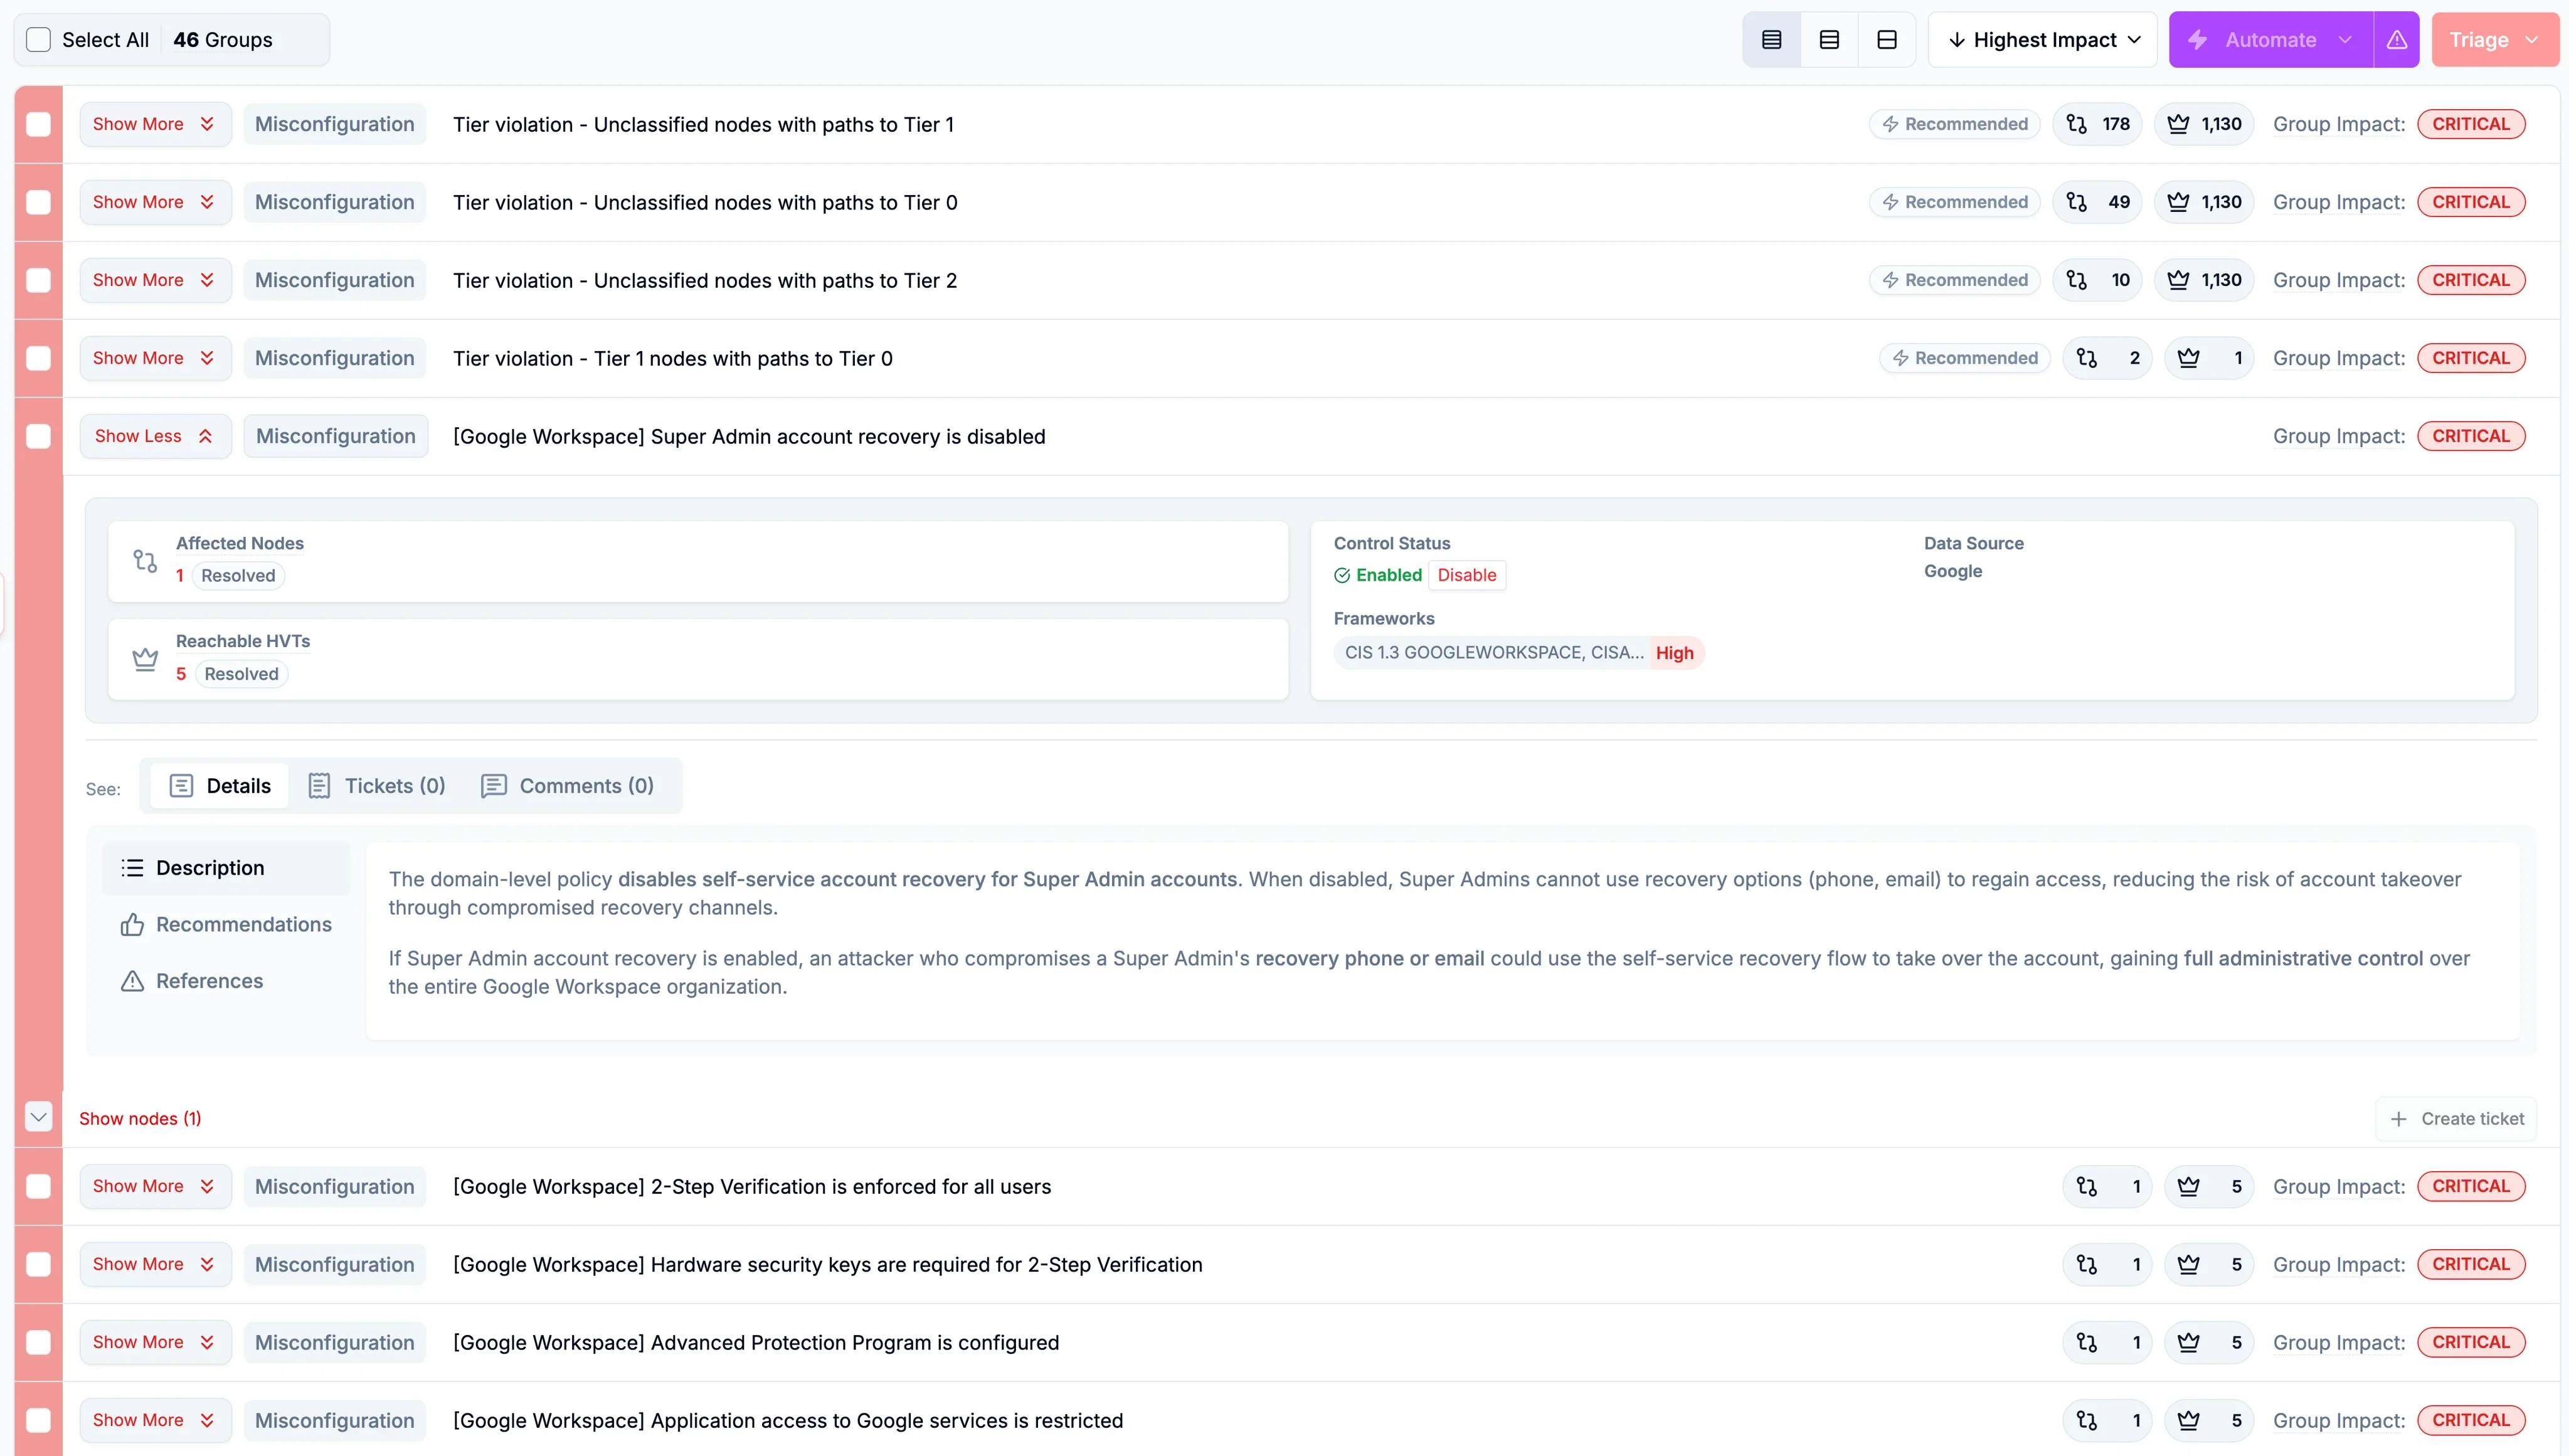
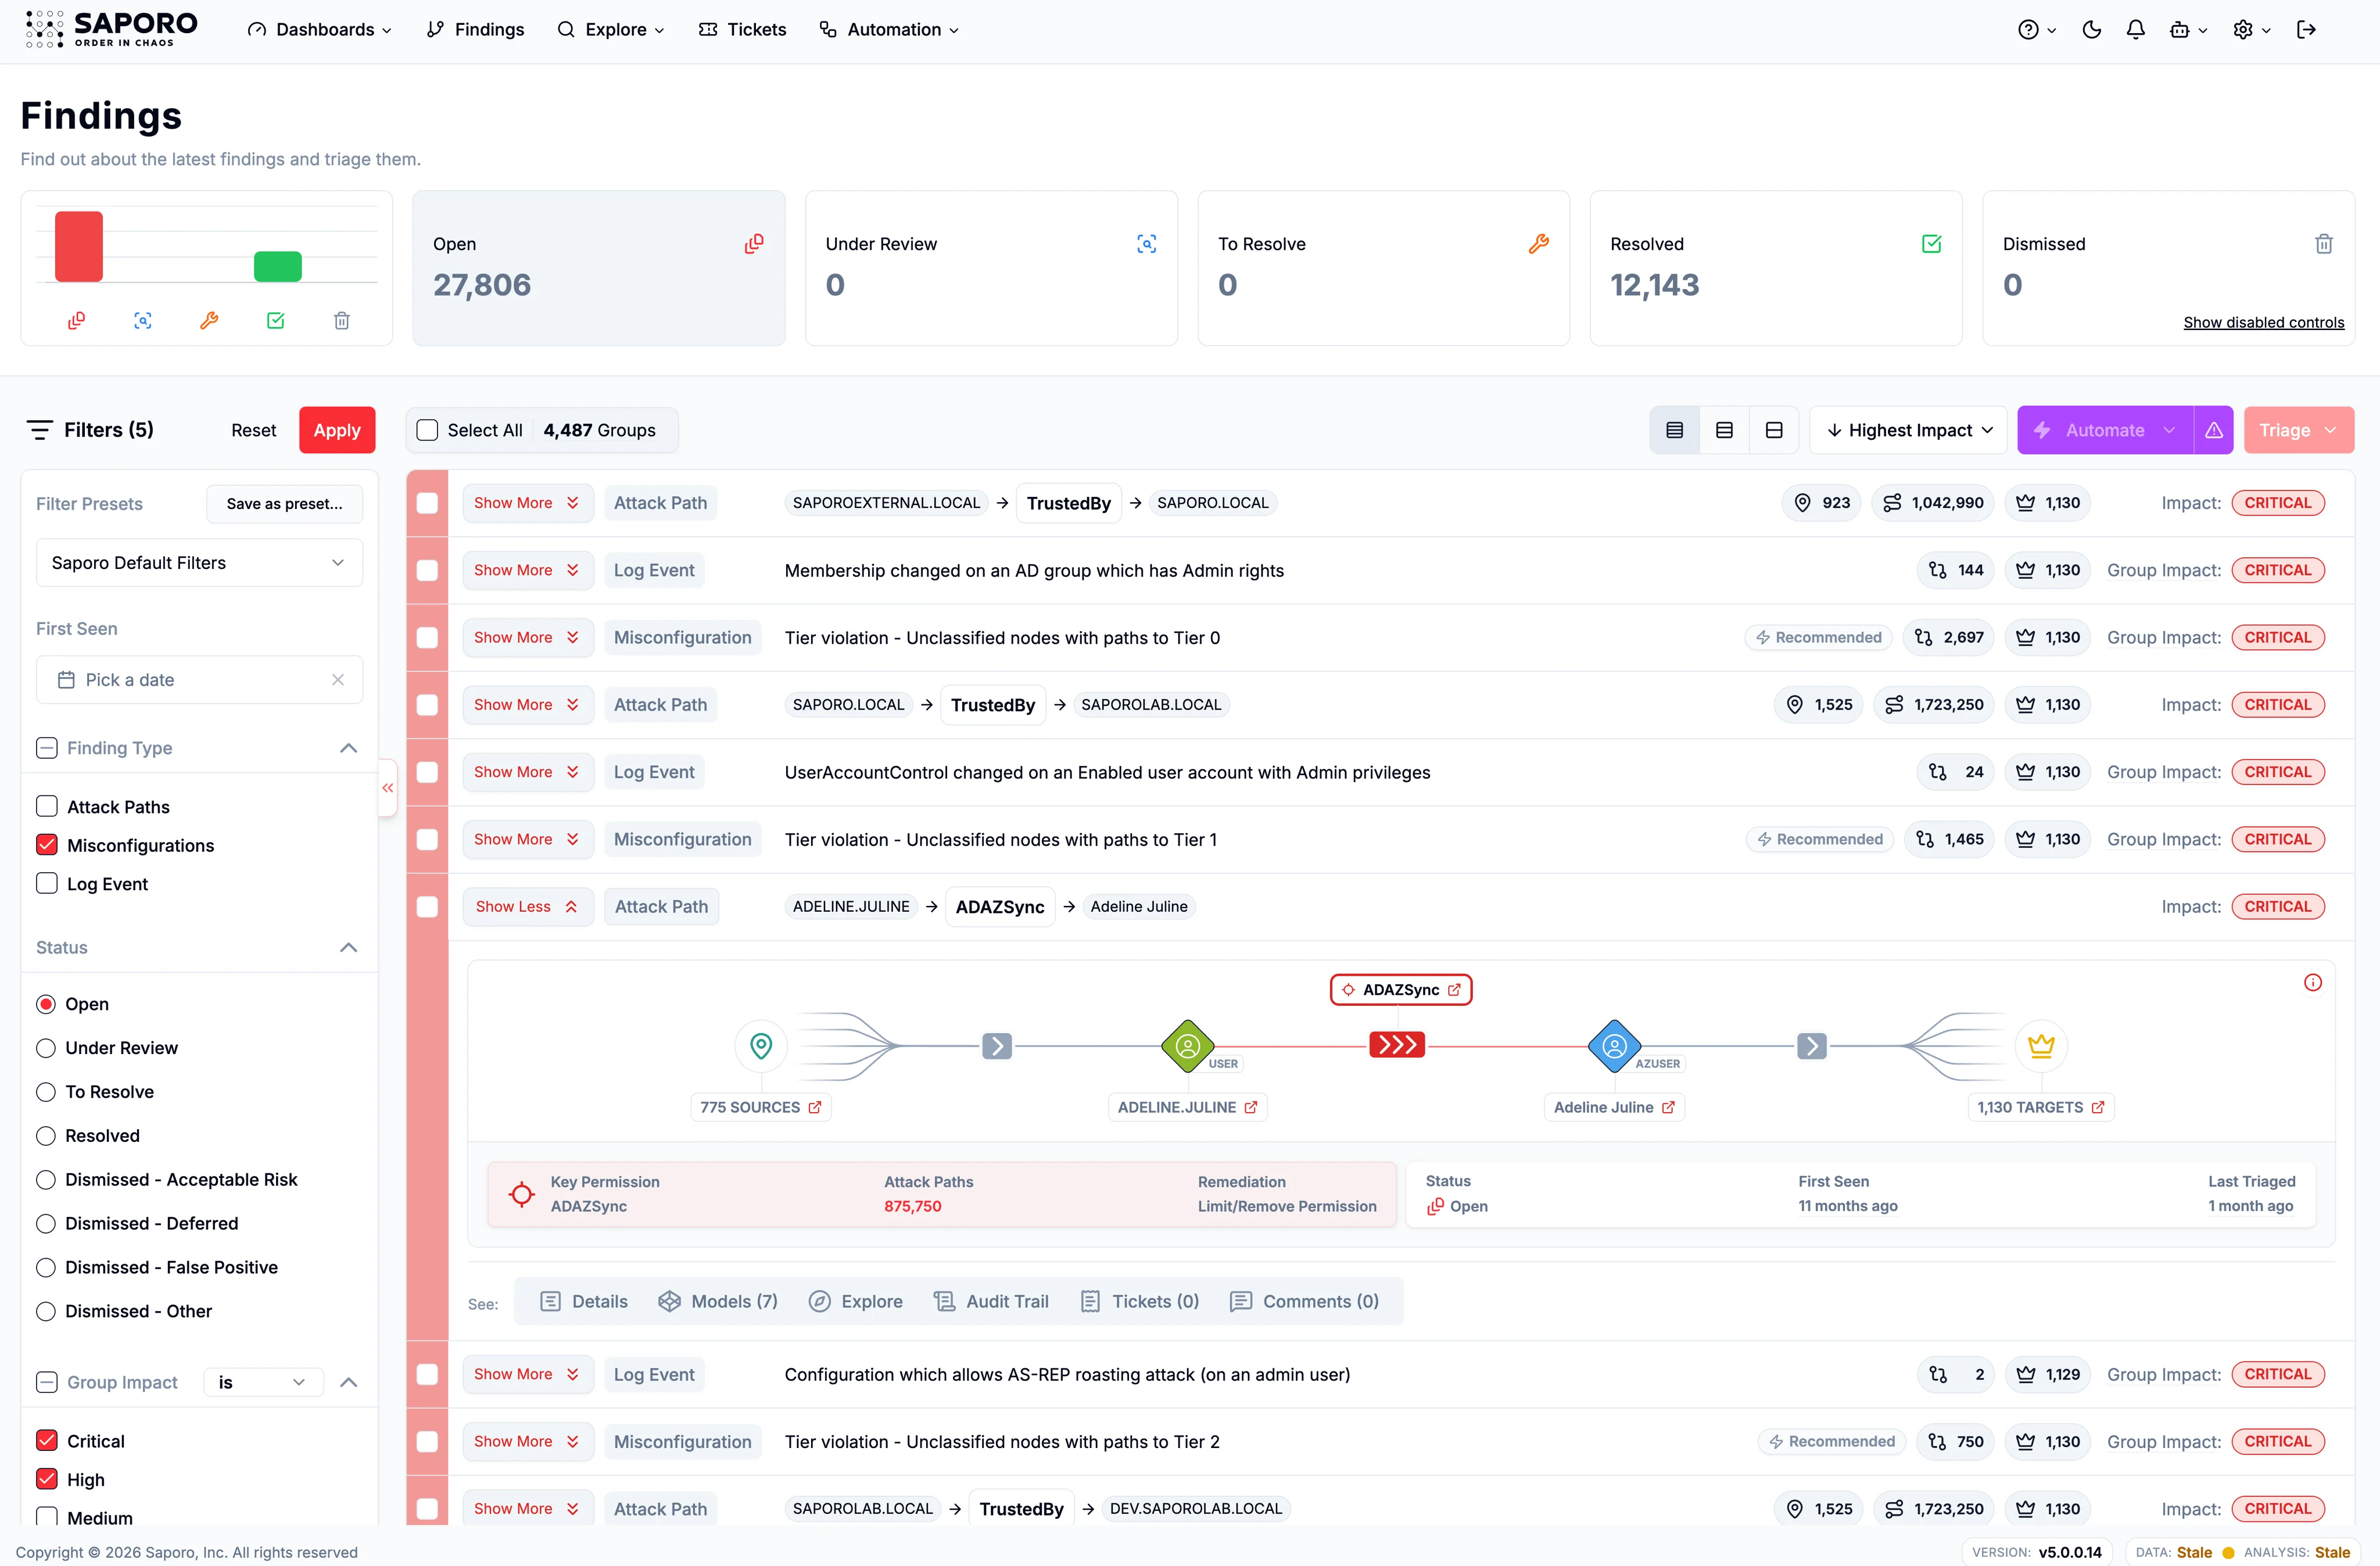
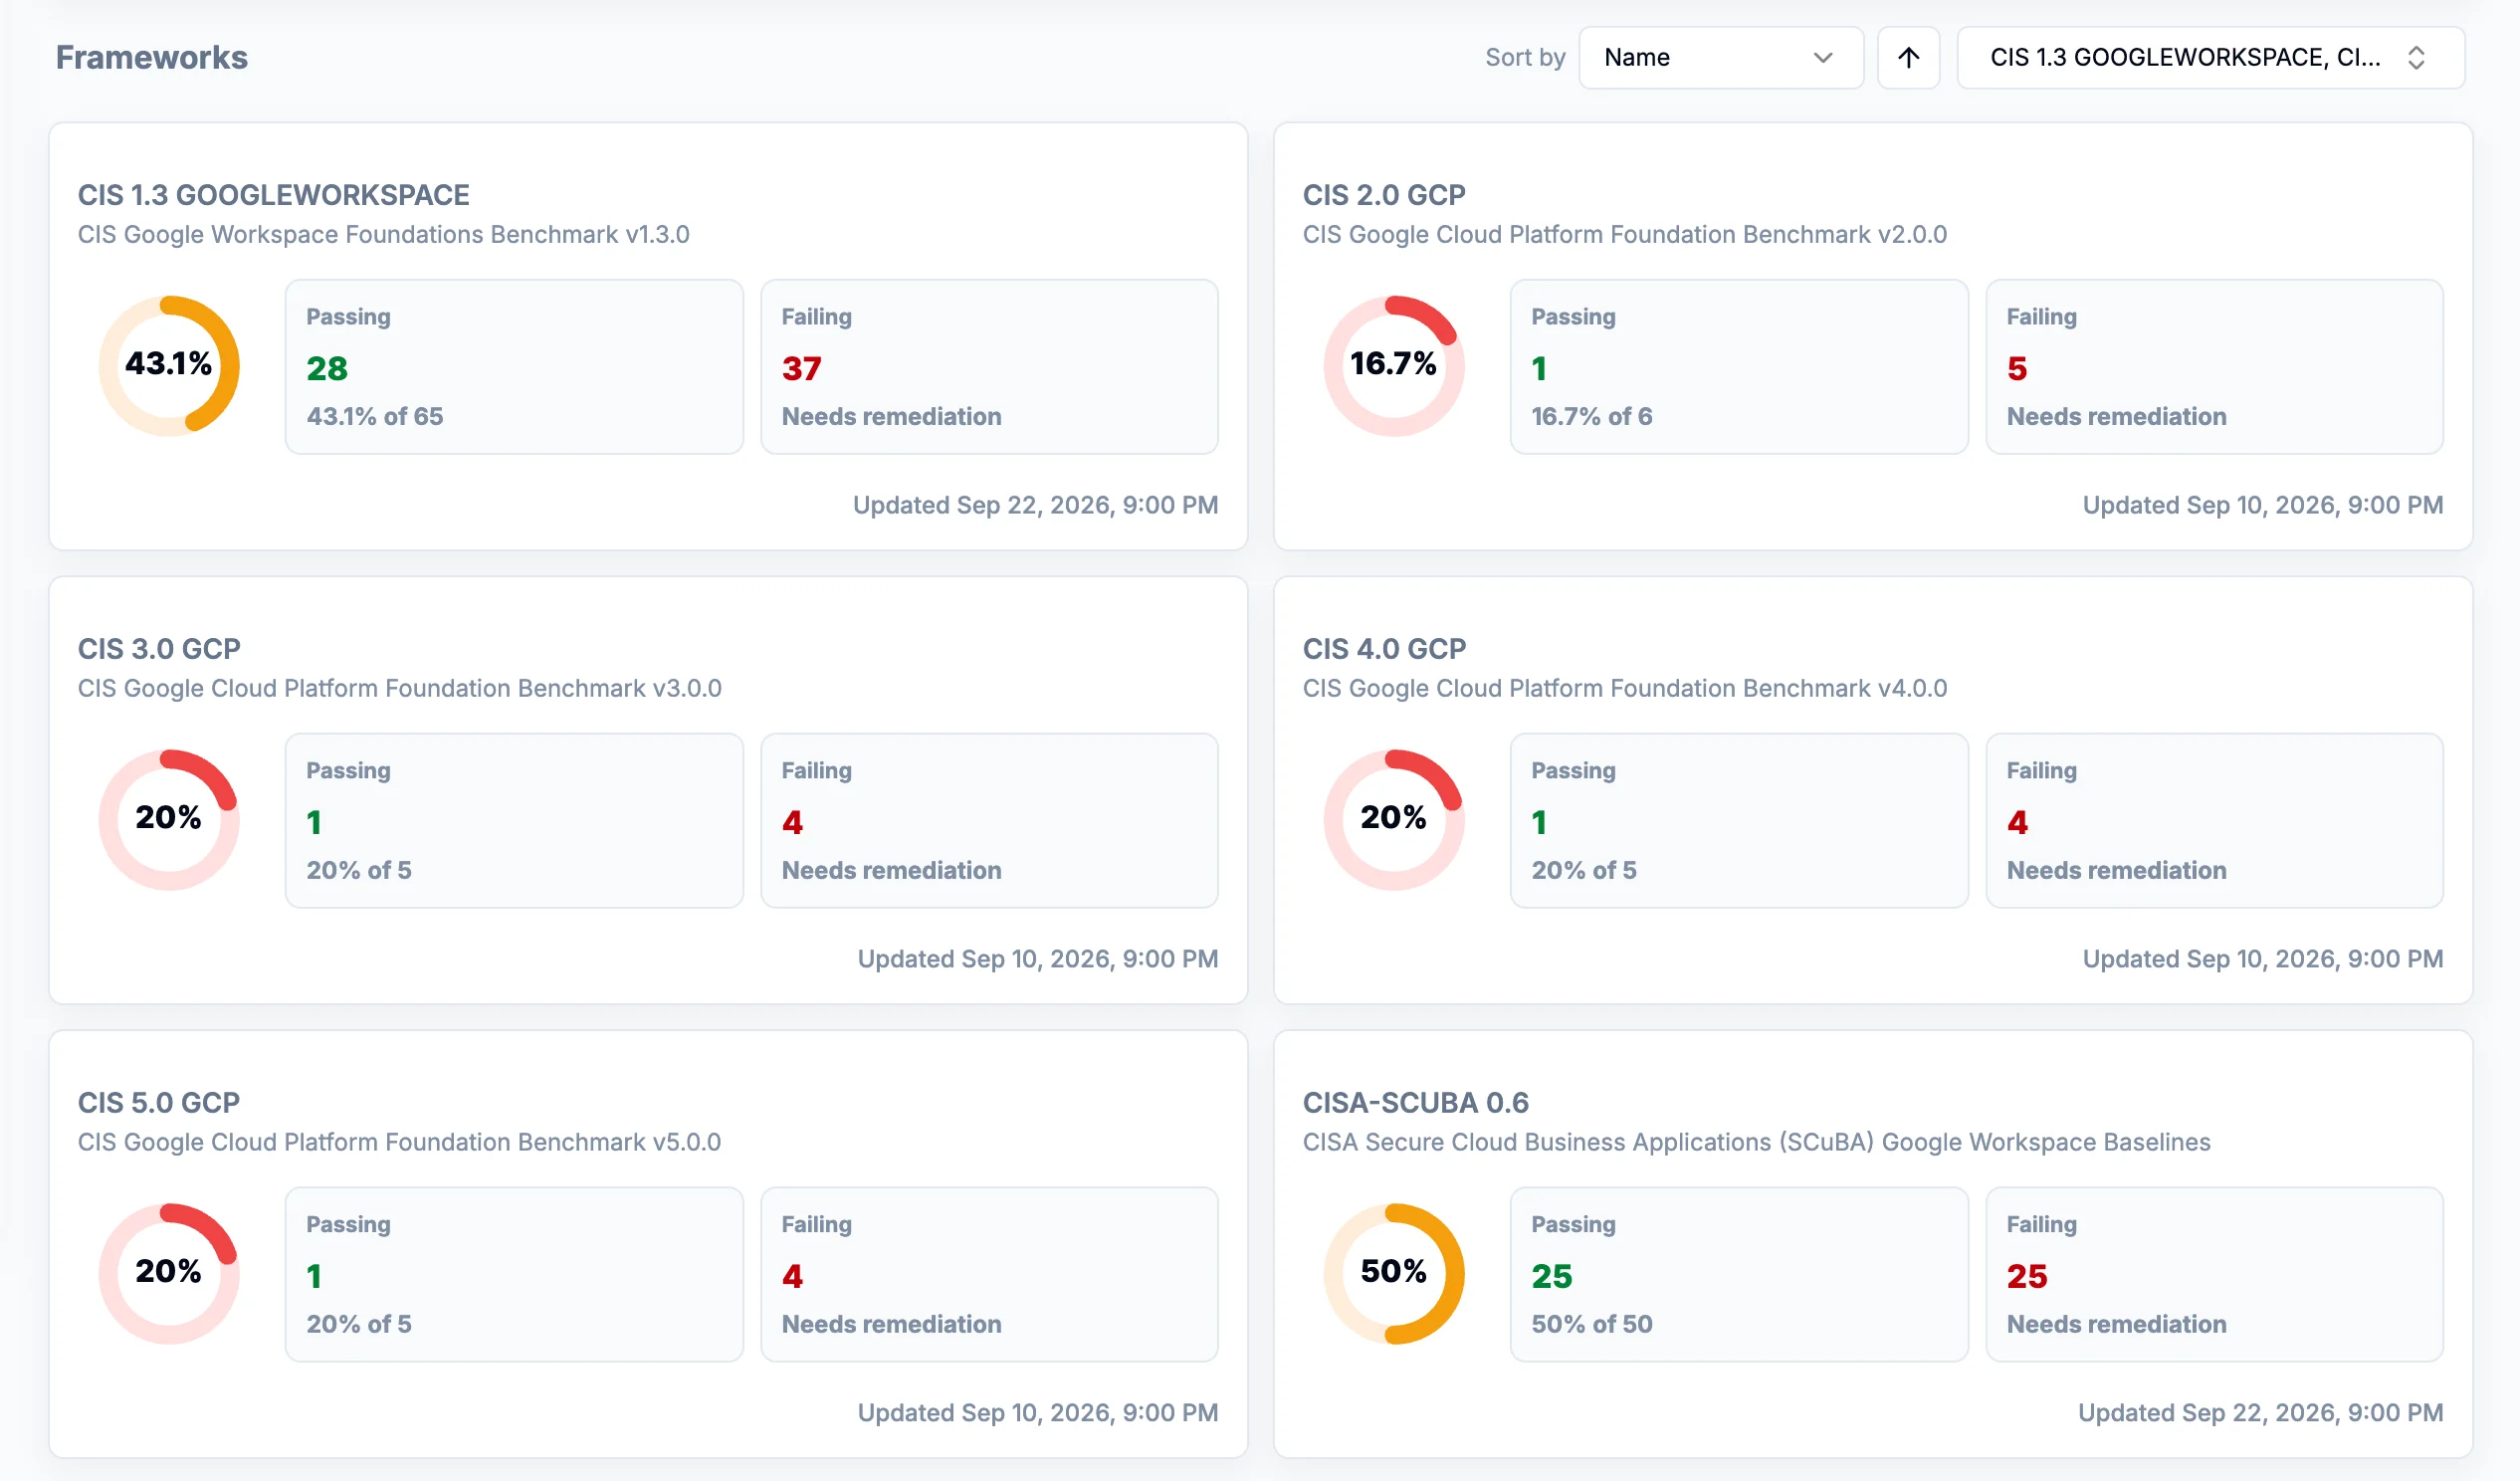
Saporo prioritizes exposure using reachability, privilege propagation, impact on critical assets, and the amount of attack surface a change can remove. This helps teams focus on the misconfigurations, excessive permissions, and risky relationships where remediation reduces the most exposure.

Yes. Google Workspace and Google Cloud collection can be enabled separately. Analyze either environment on its own, or connect both to reveal how Workspace users, groups, and administrative privileges relate to Google Cloud access.

Reduce identity exposure before it becomes an attack

Book a demo