
MICROSOFT ENTRA ID & AZURE EXPOSURE

Reduce identity exposure across Entra ID and Azure

Uncover excessive permissions and attack opportunities across Entra ID and Azure.

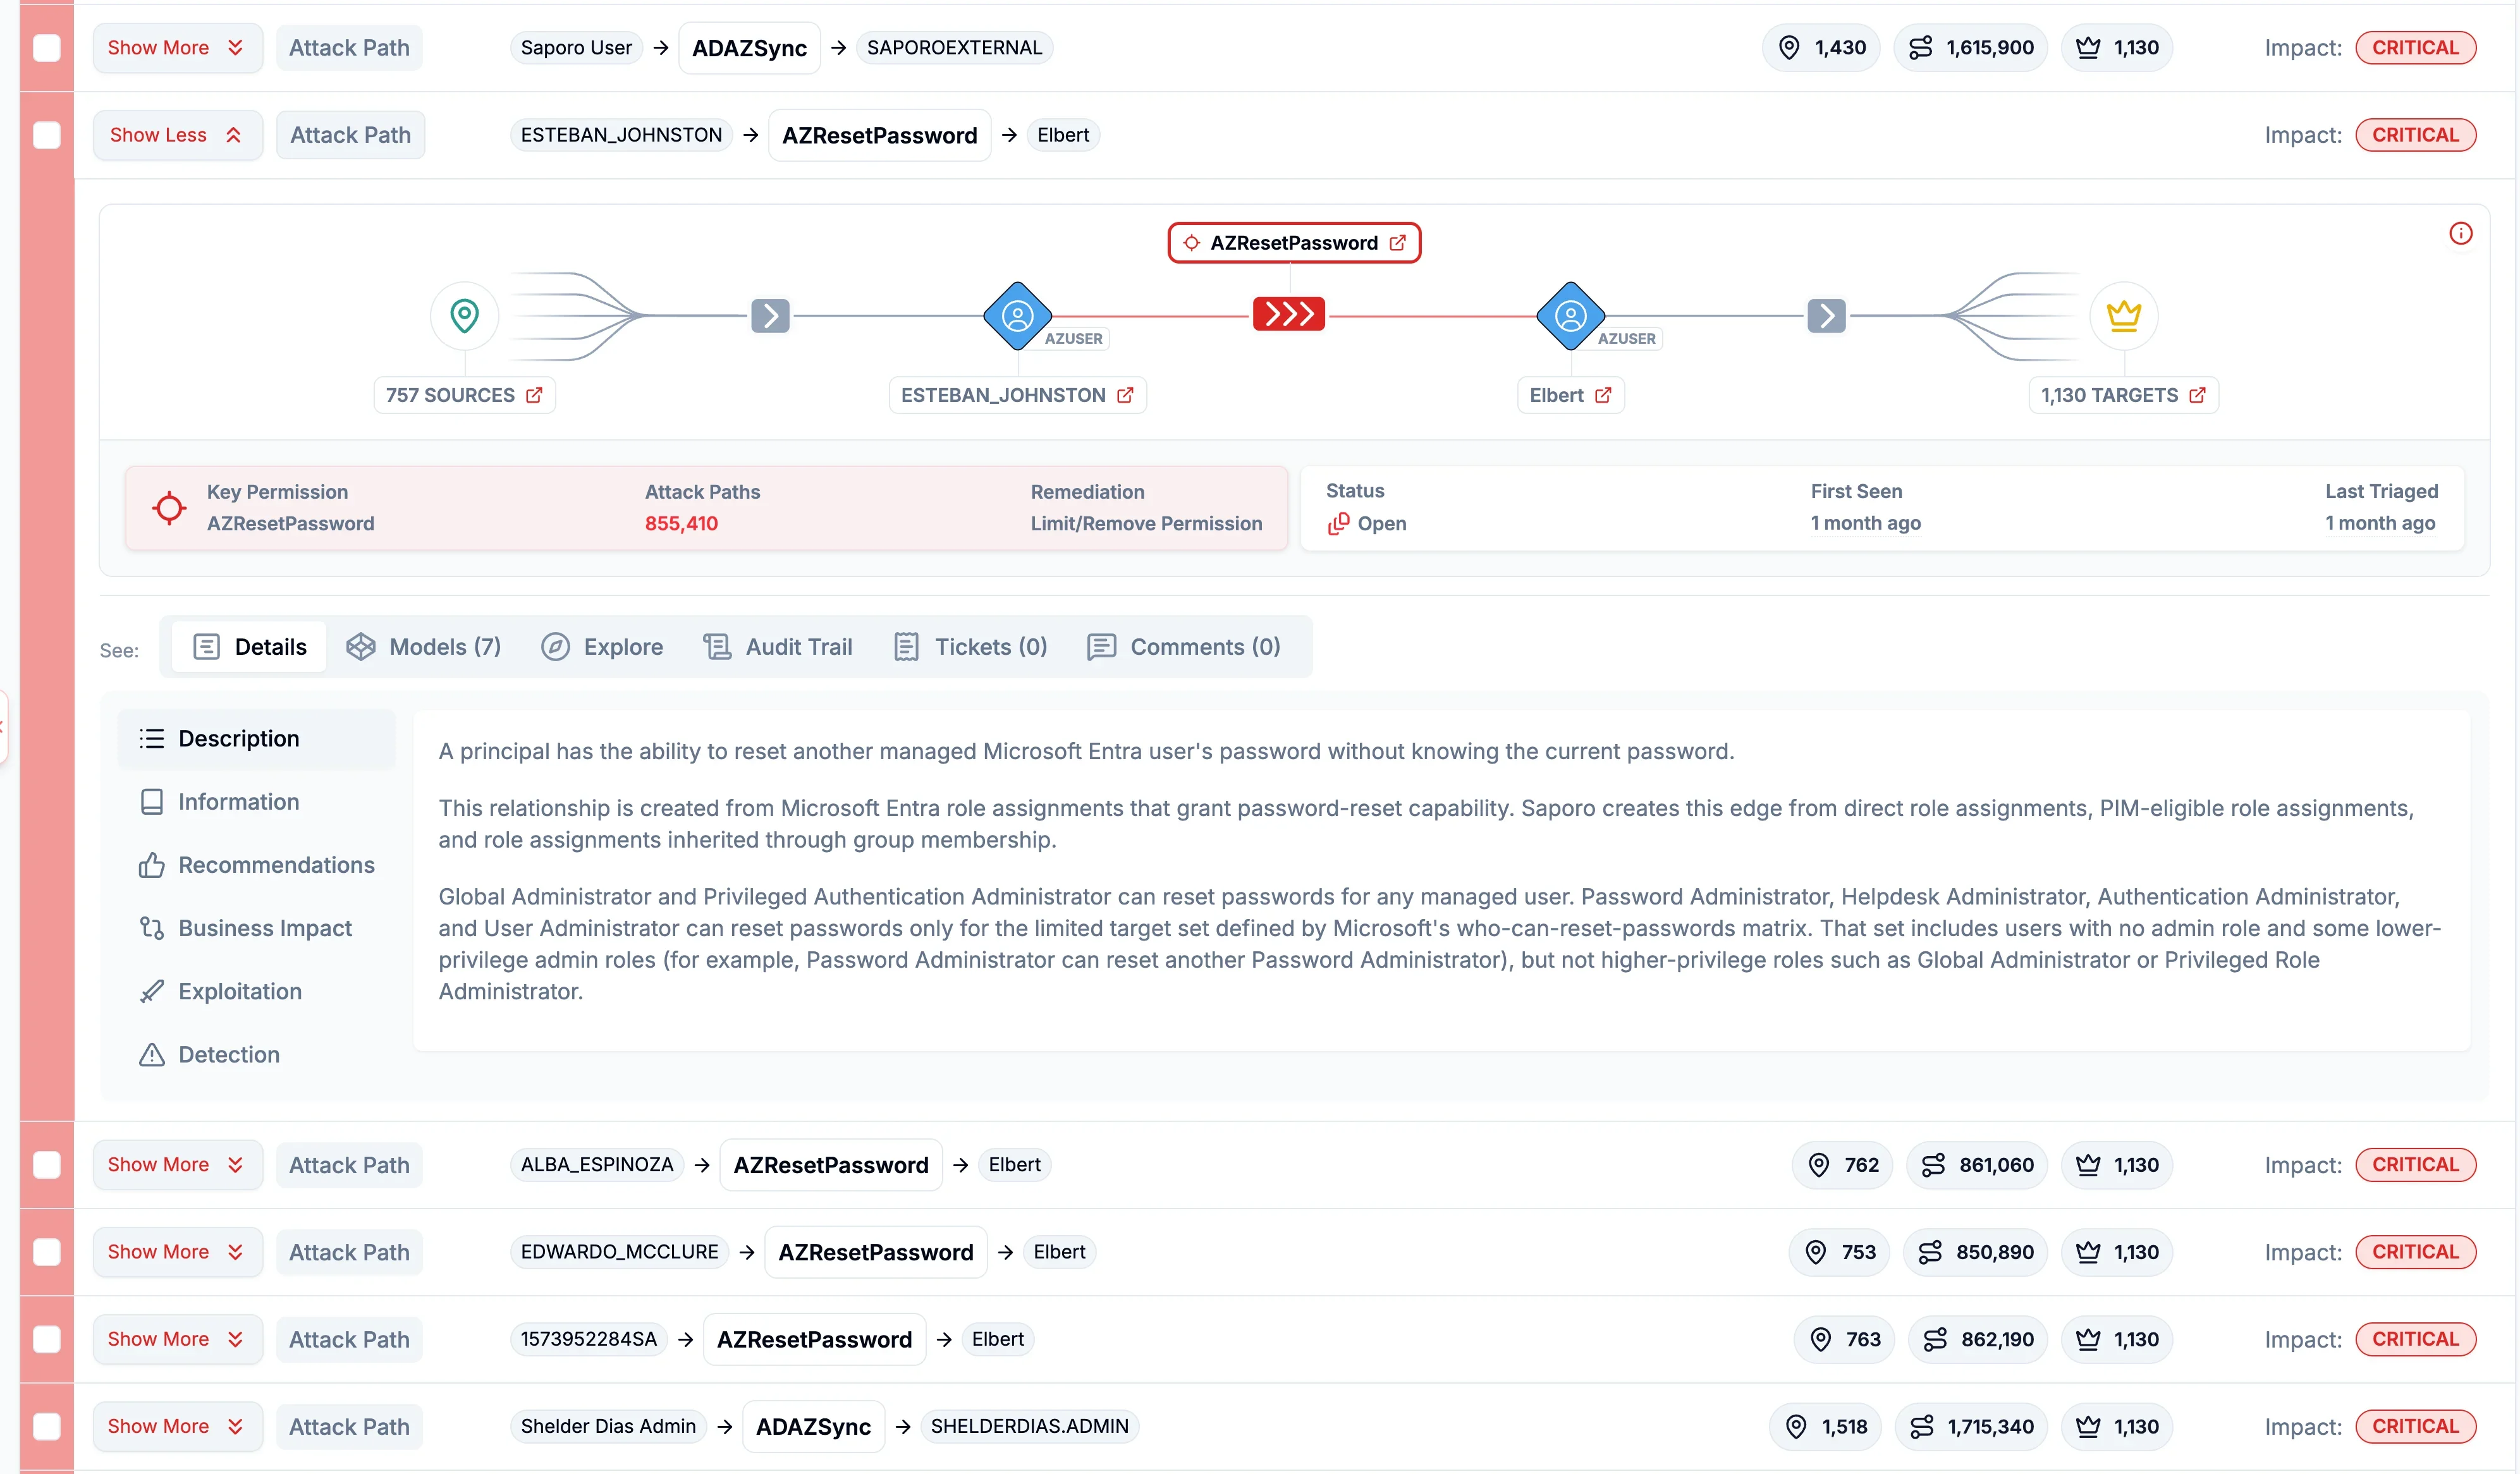
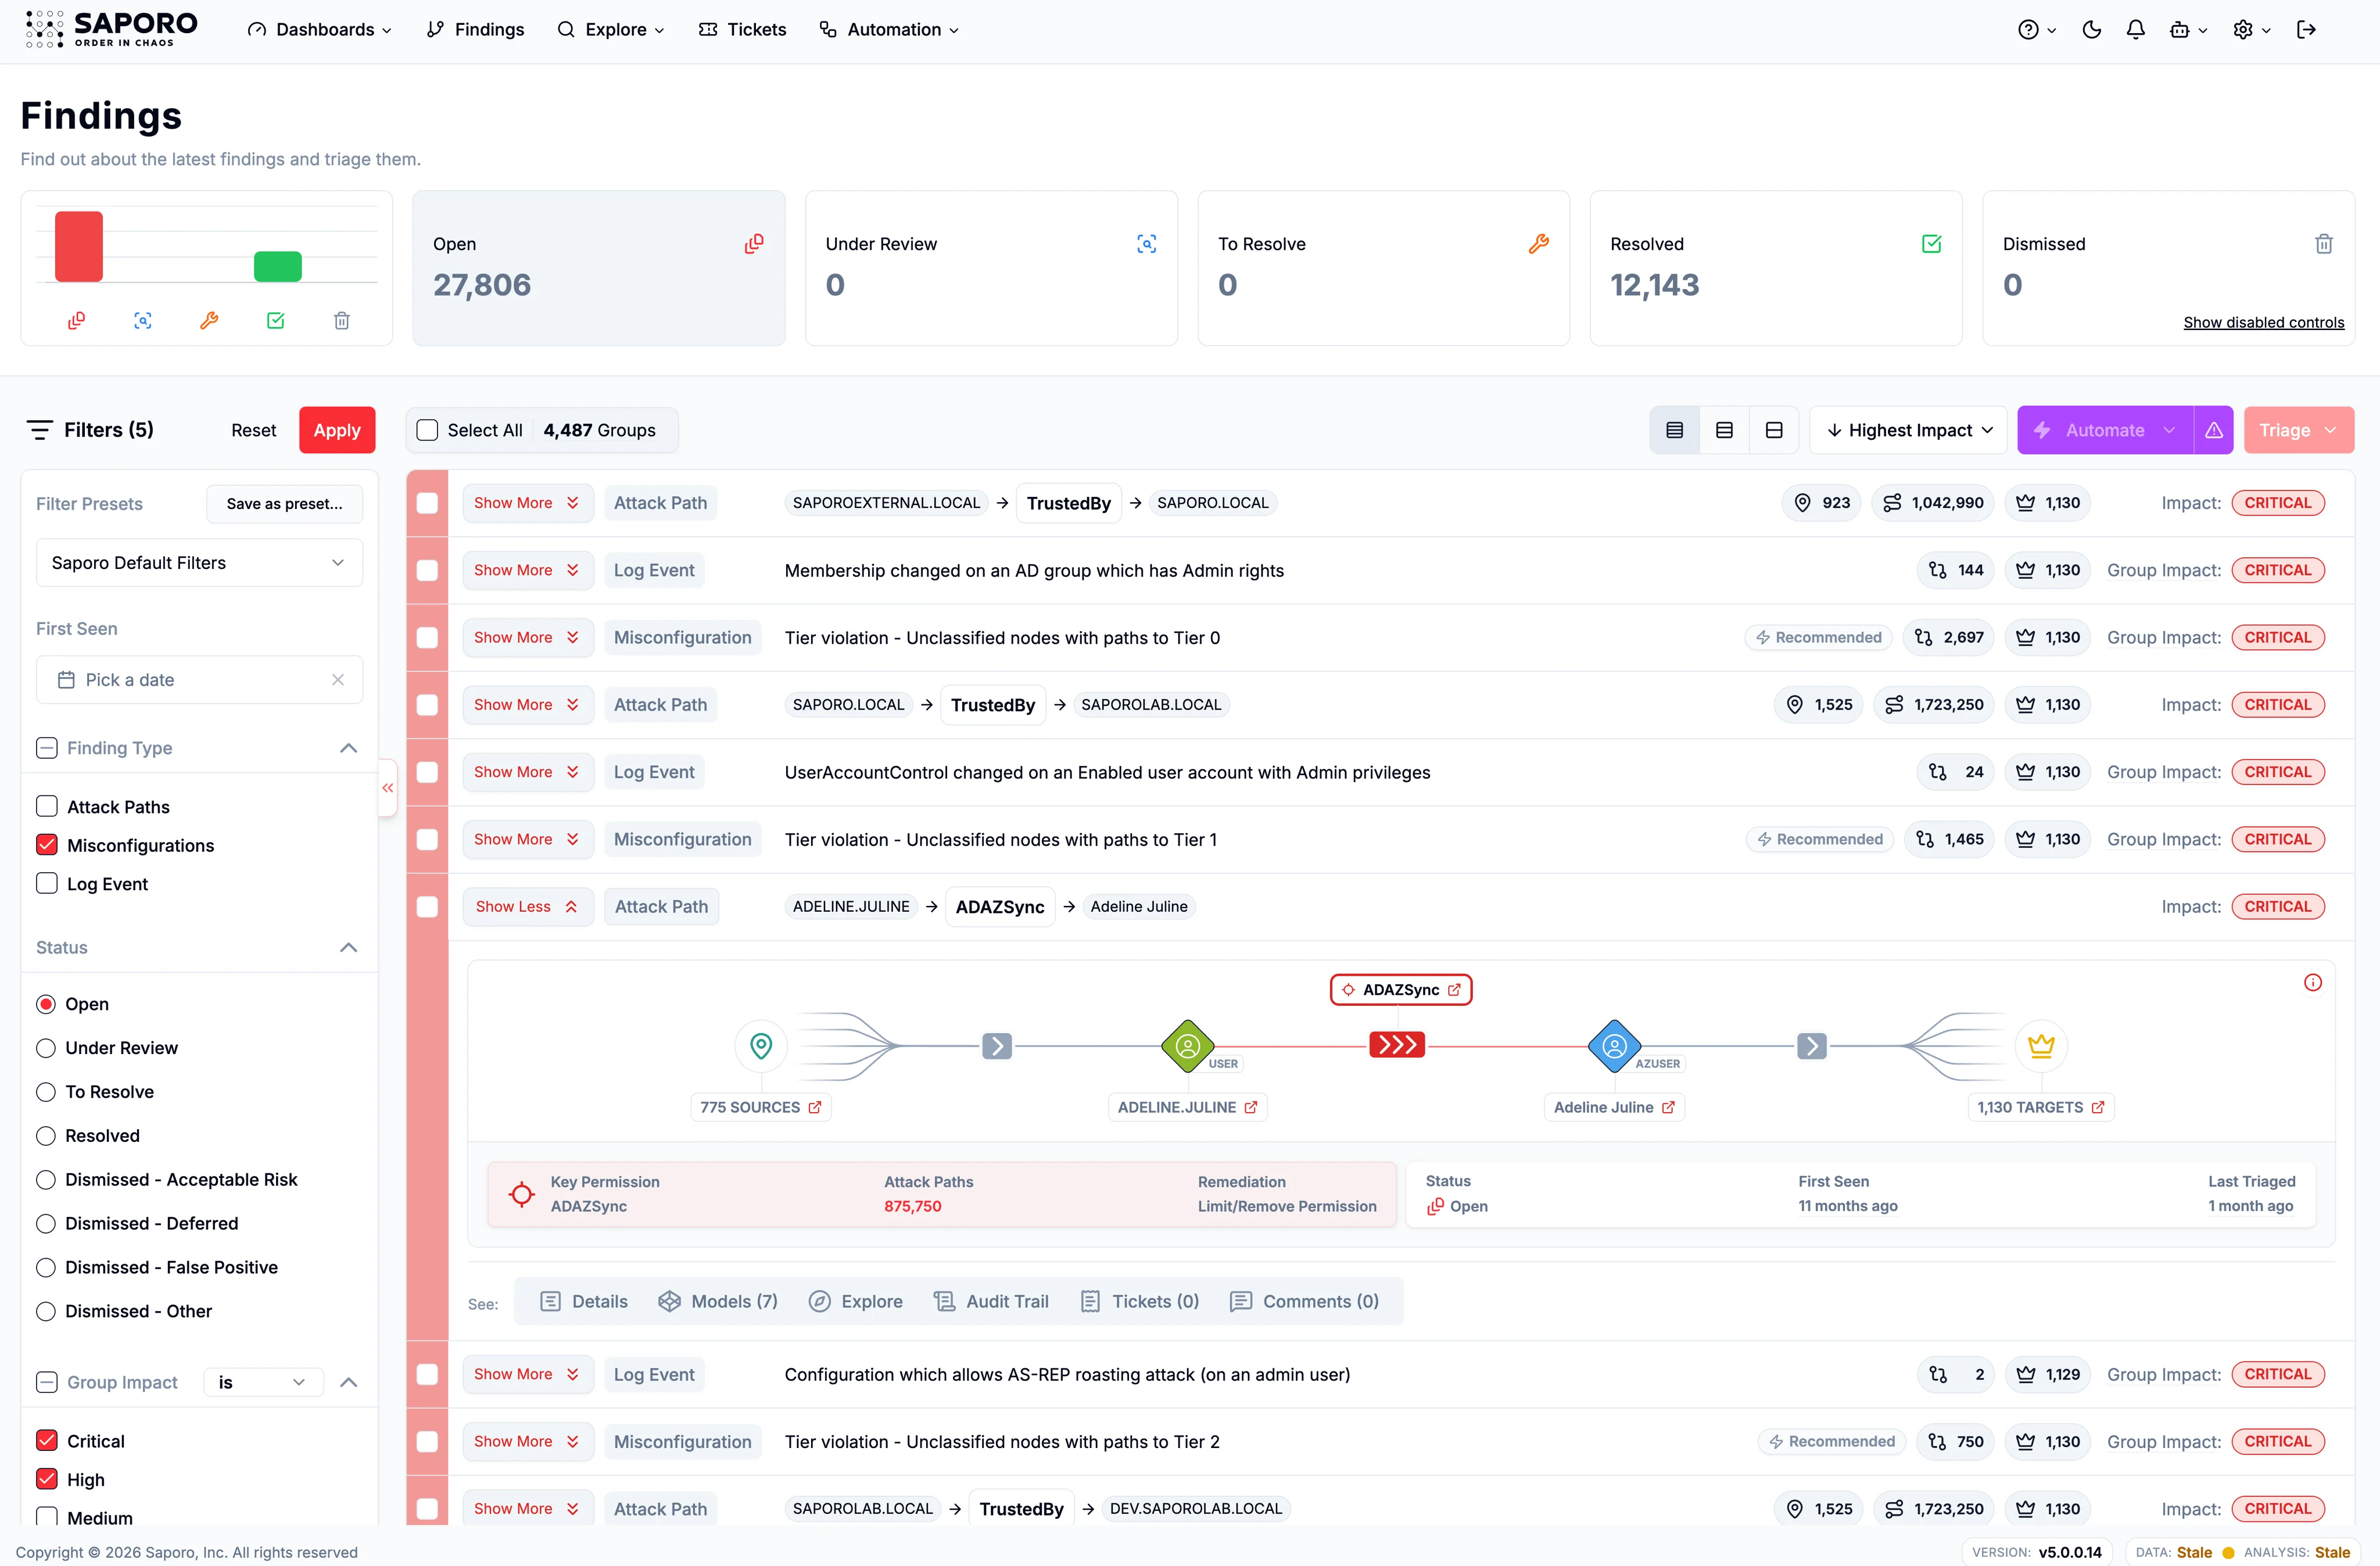
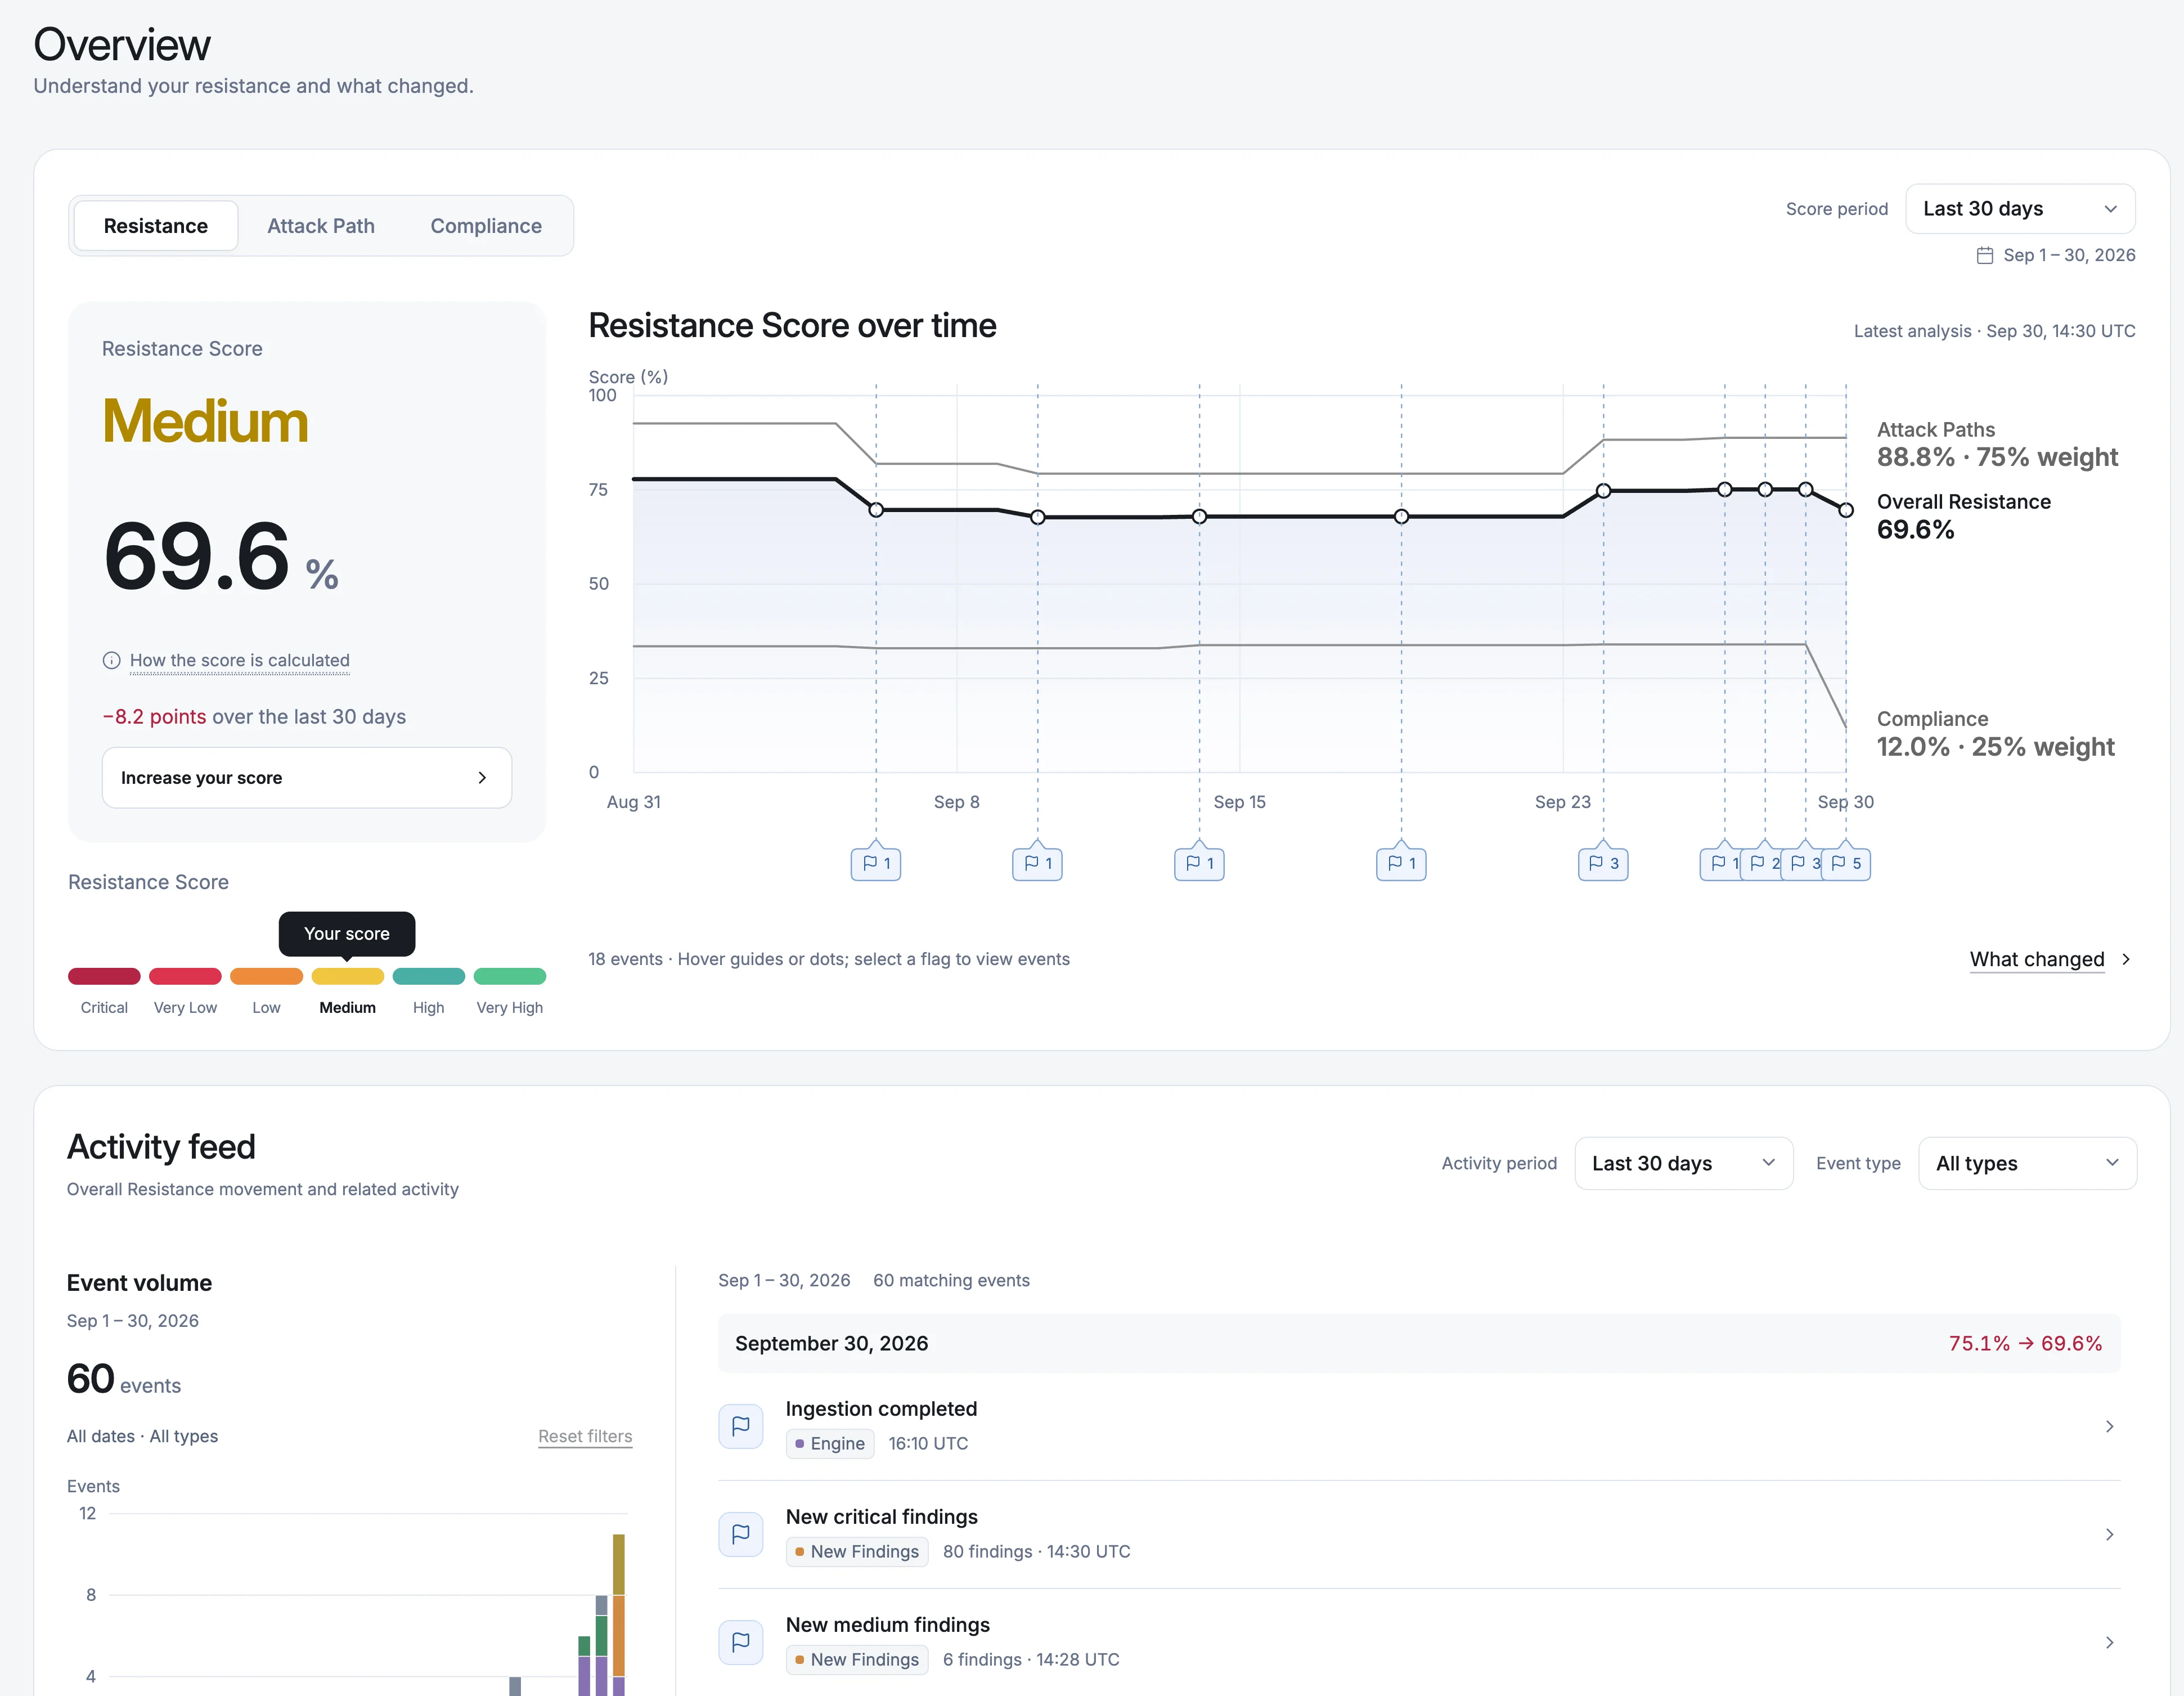
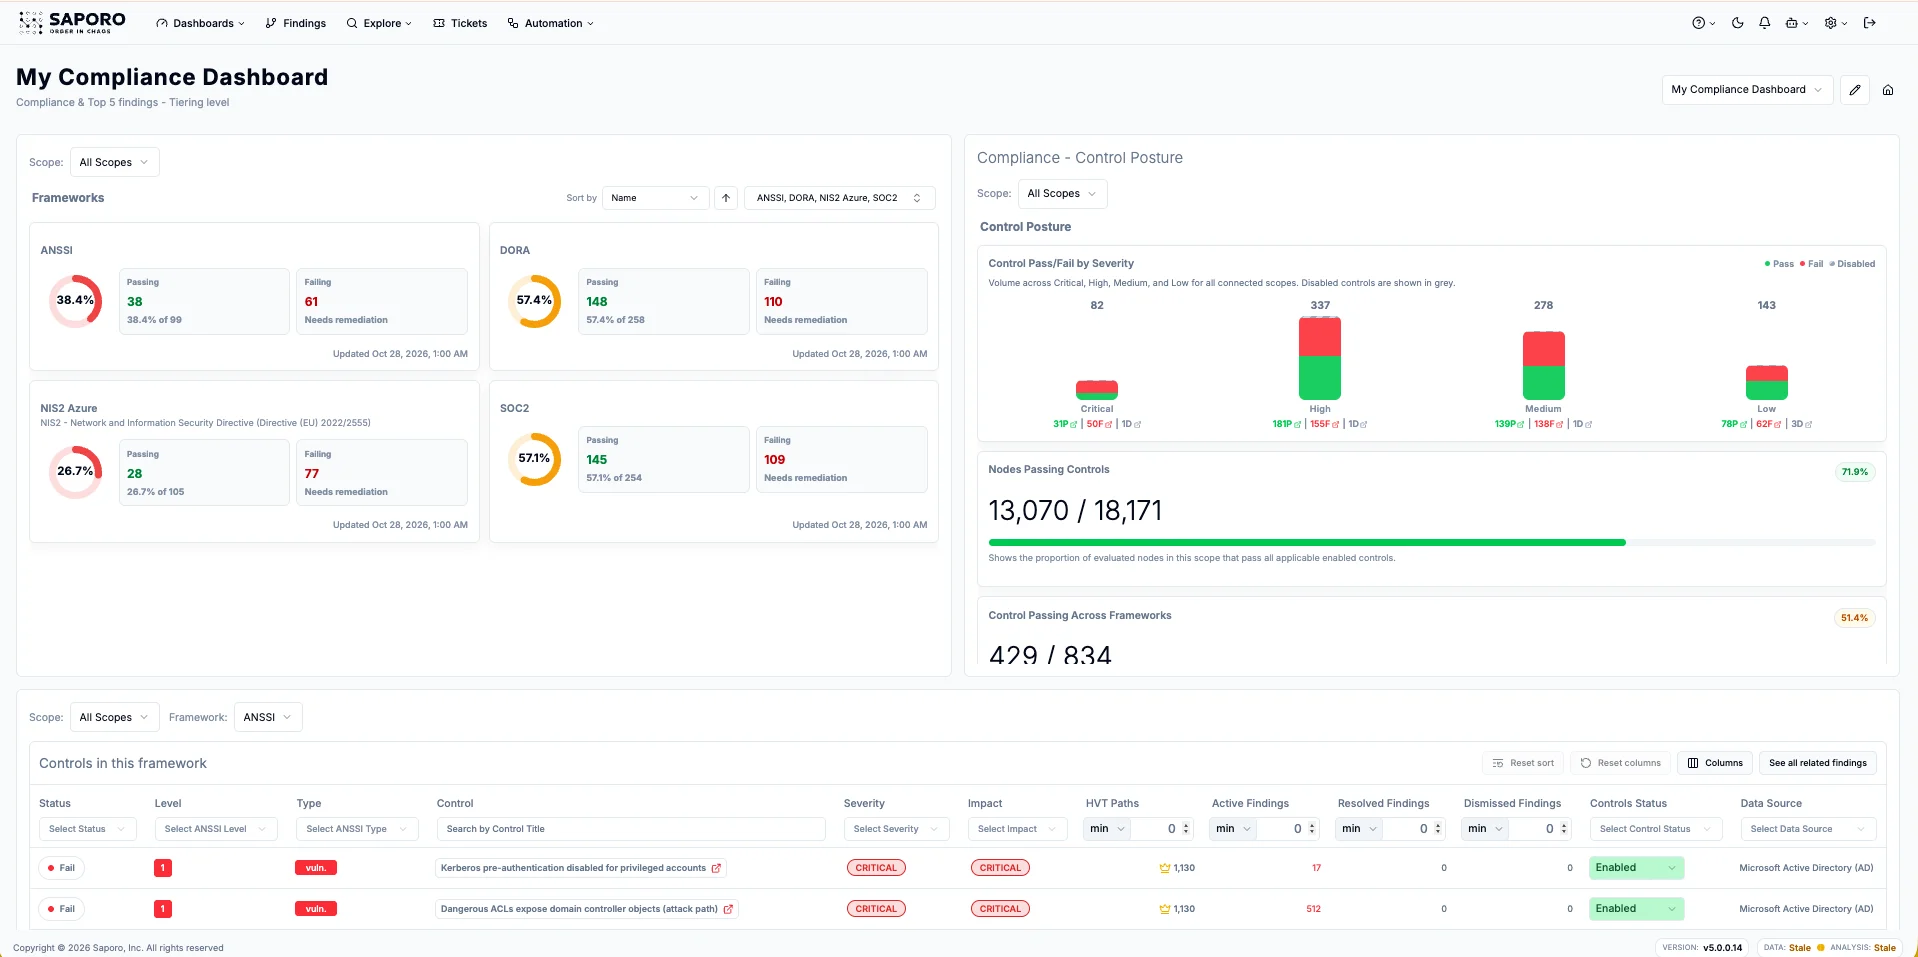
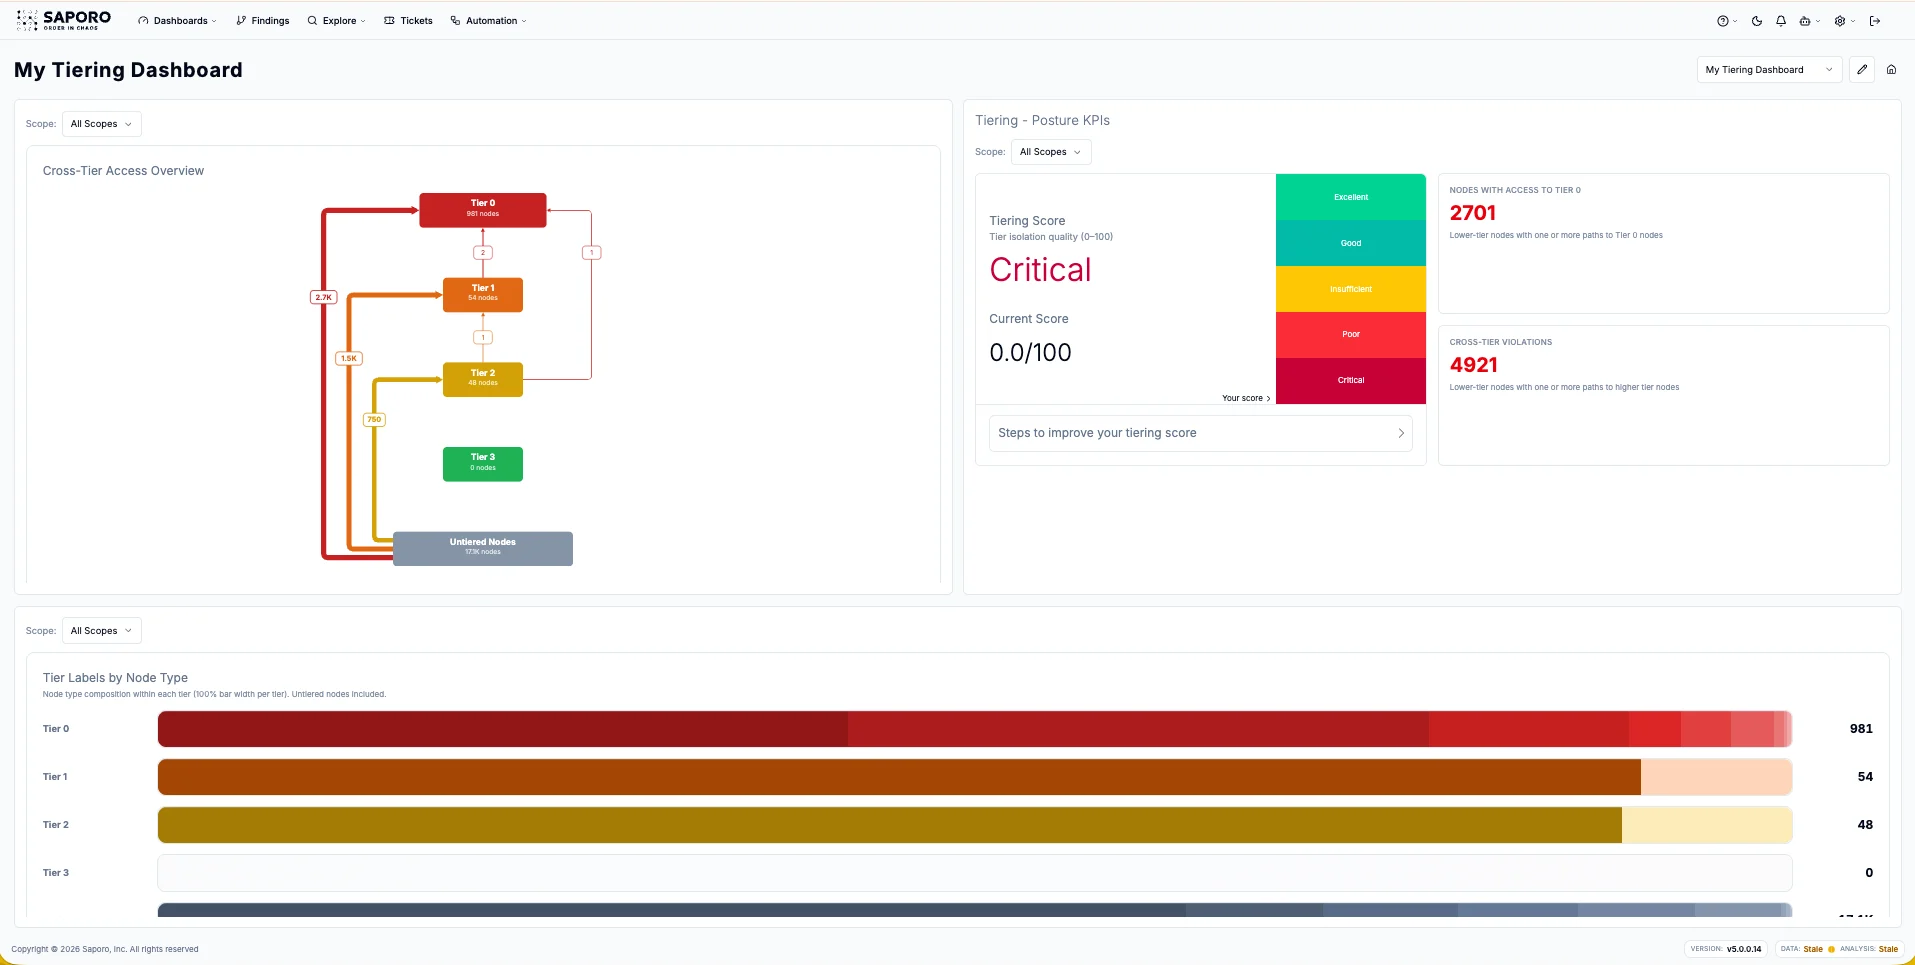
Saporo connects identities, applications, and resources in one graph to prioritize the changes that best protect critical assets. For hybrid environments, it also connects on-premises Active Directory to reveal how exposure extends across both.

Microsoft Entra IDMicrosoft Azure
  • Users & groups
  • Applications
  • Directory roles
  • Azure RBAC
  • Resources
  • Managed identities

78% of observed attack techniques against critical infrastructure used cloud identity abuse.

Source: Microsoft Digital Defense Report 2026

ENTRA ID & AZURE Q&A

What security teams ask about Microsoft cloud identity exposure

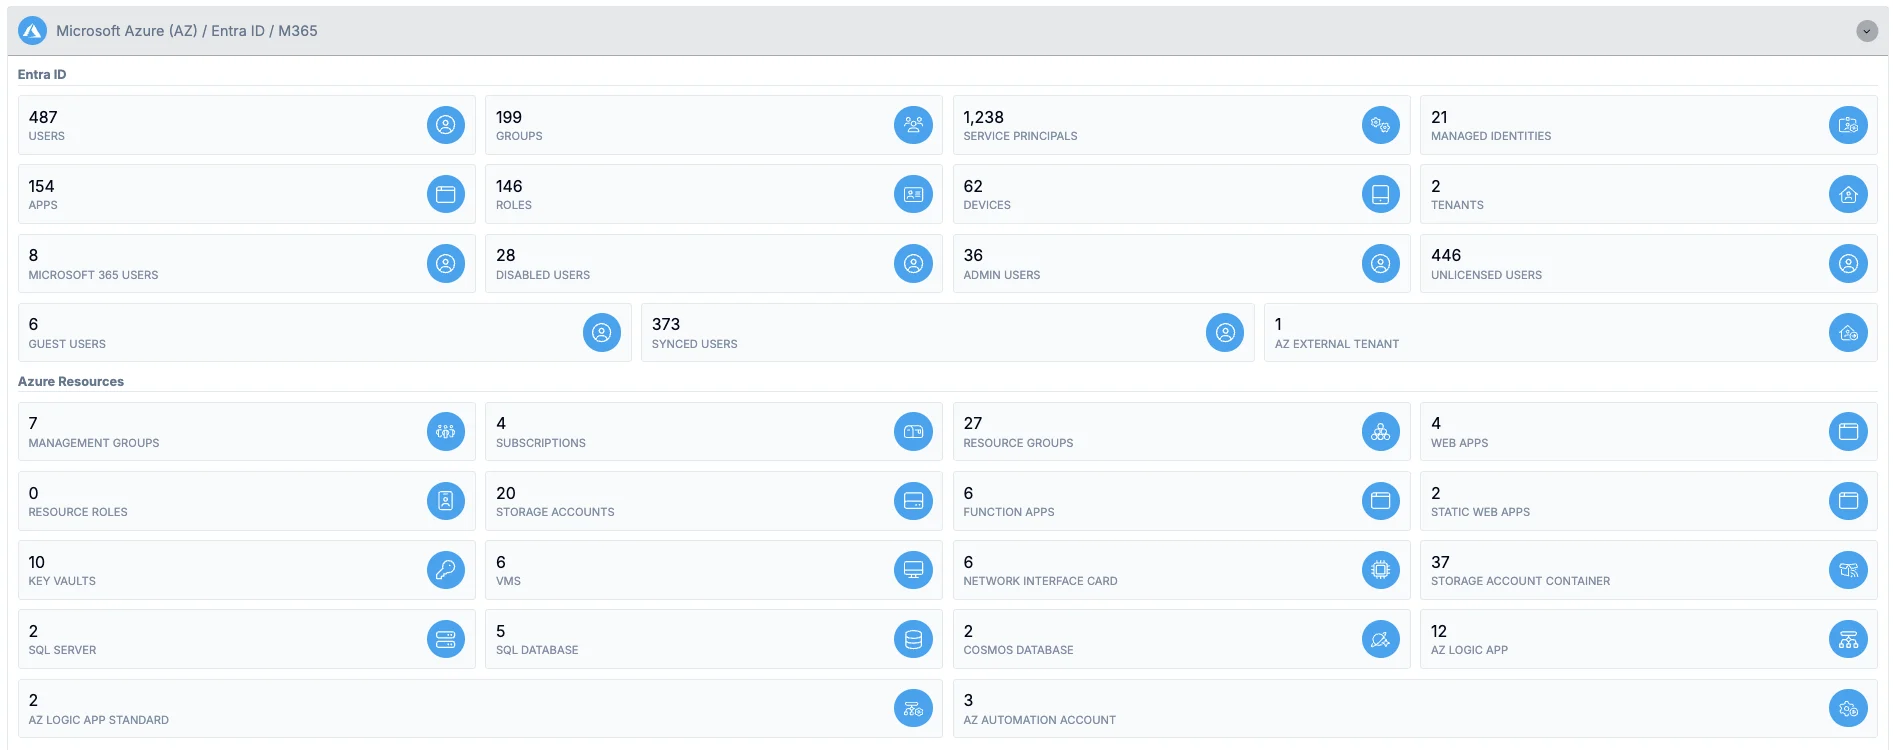
Saporo connects users, groups, directory roles, app registrations and their service principals (enterprise applications), managed identities, Azure RBAC, management groups, subscriptions, resource groups, and resources in one attack model.

Their permissions and administrative relationships are evaluated alongside human identities and cloud roles, making it easier to see where non-human access can expand reach or contribute to a path toward a critical resource.

Yes. Saporo connects directory roles, group memberships, application permissions, and Azure RBAC to the resources they affect. This helps reveal how control of an identity or application could lead to access to subscriptions, Key Vaults, virtual machines, storage accounts, databases, or other critical resources.

Yes. When both sources are connected, Saporo links synchronized identities and other collected hybrid relationships between Active Directory and Microsoft cloud. This helps reveal how exposure can propagate across cloud and on-premises environments.

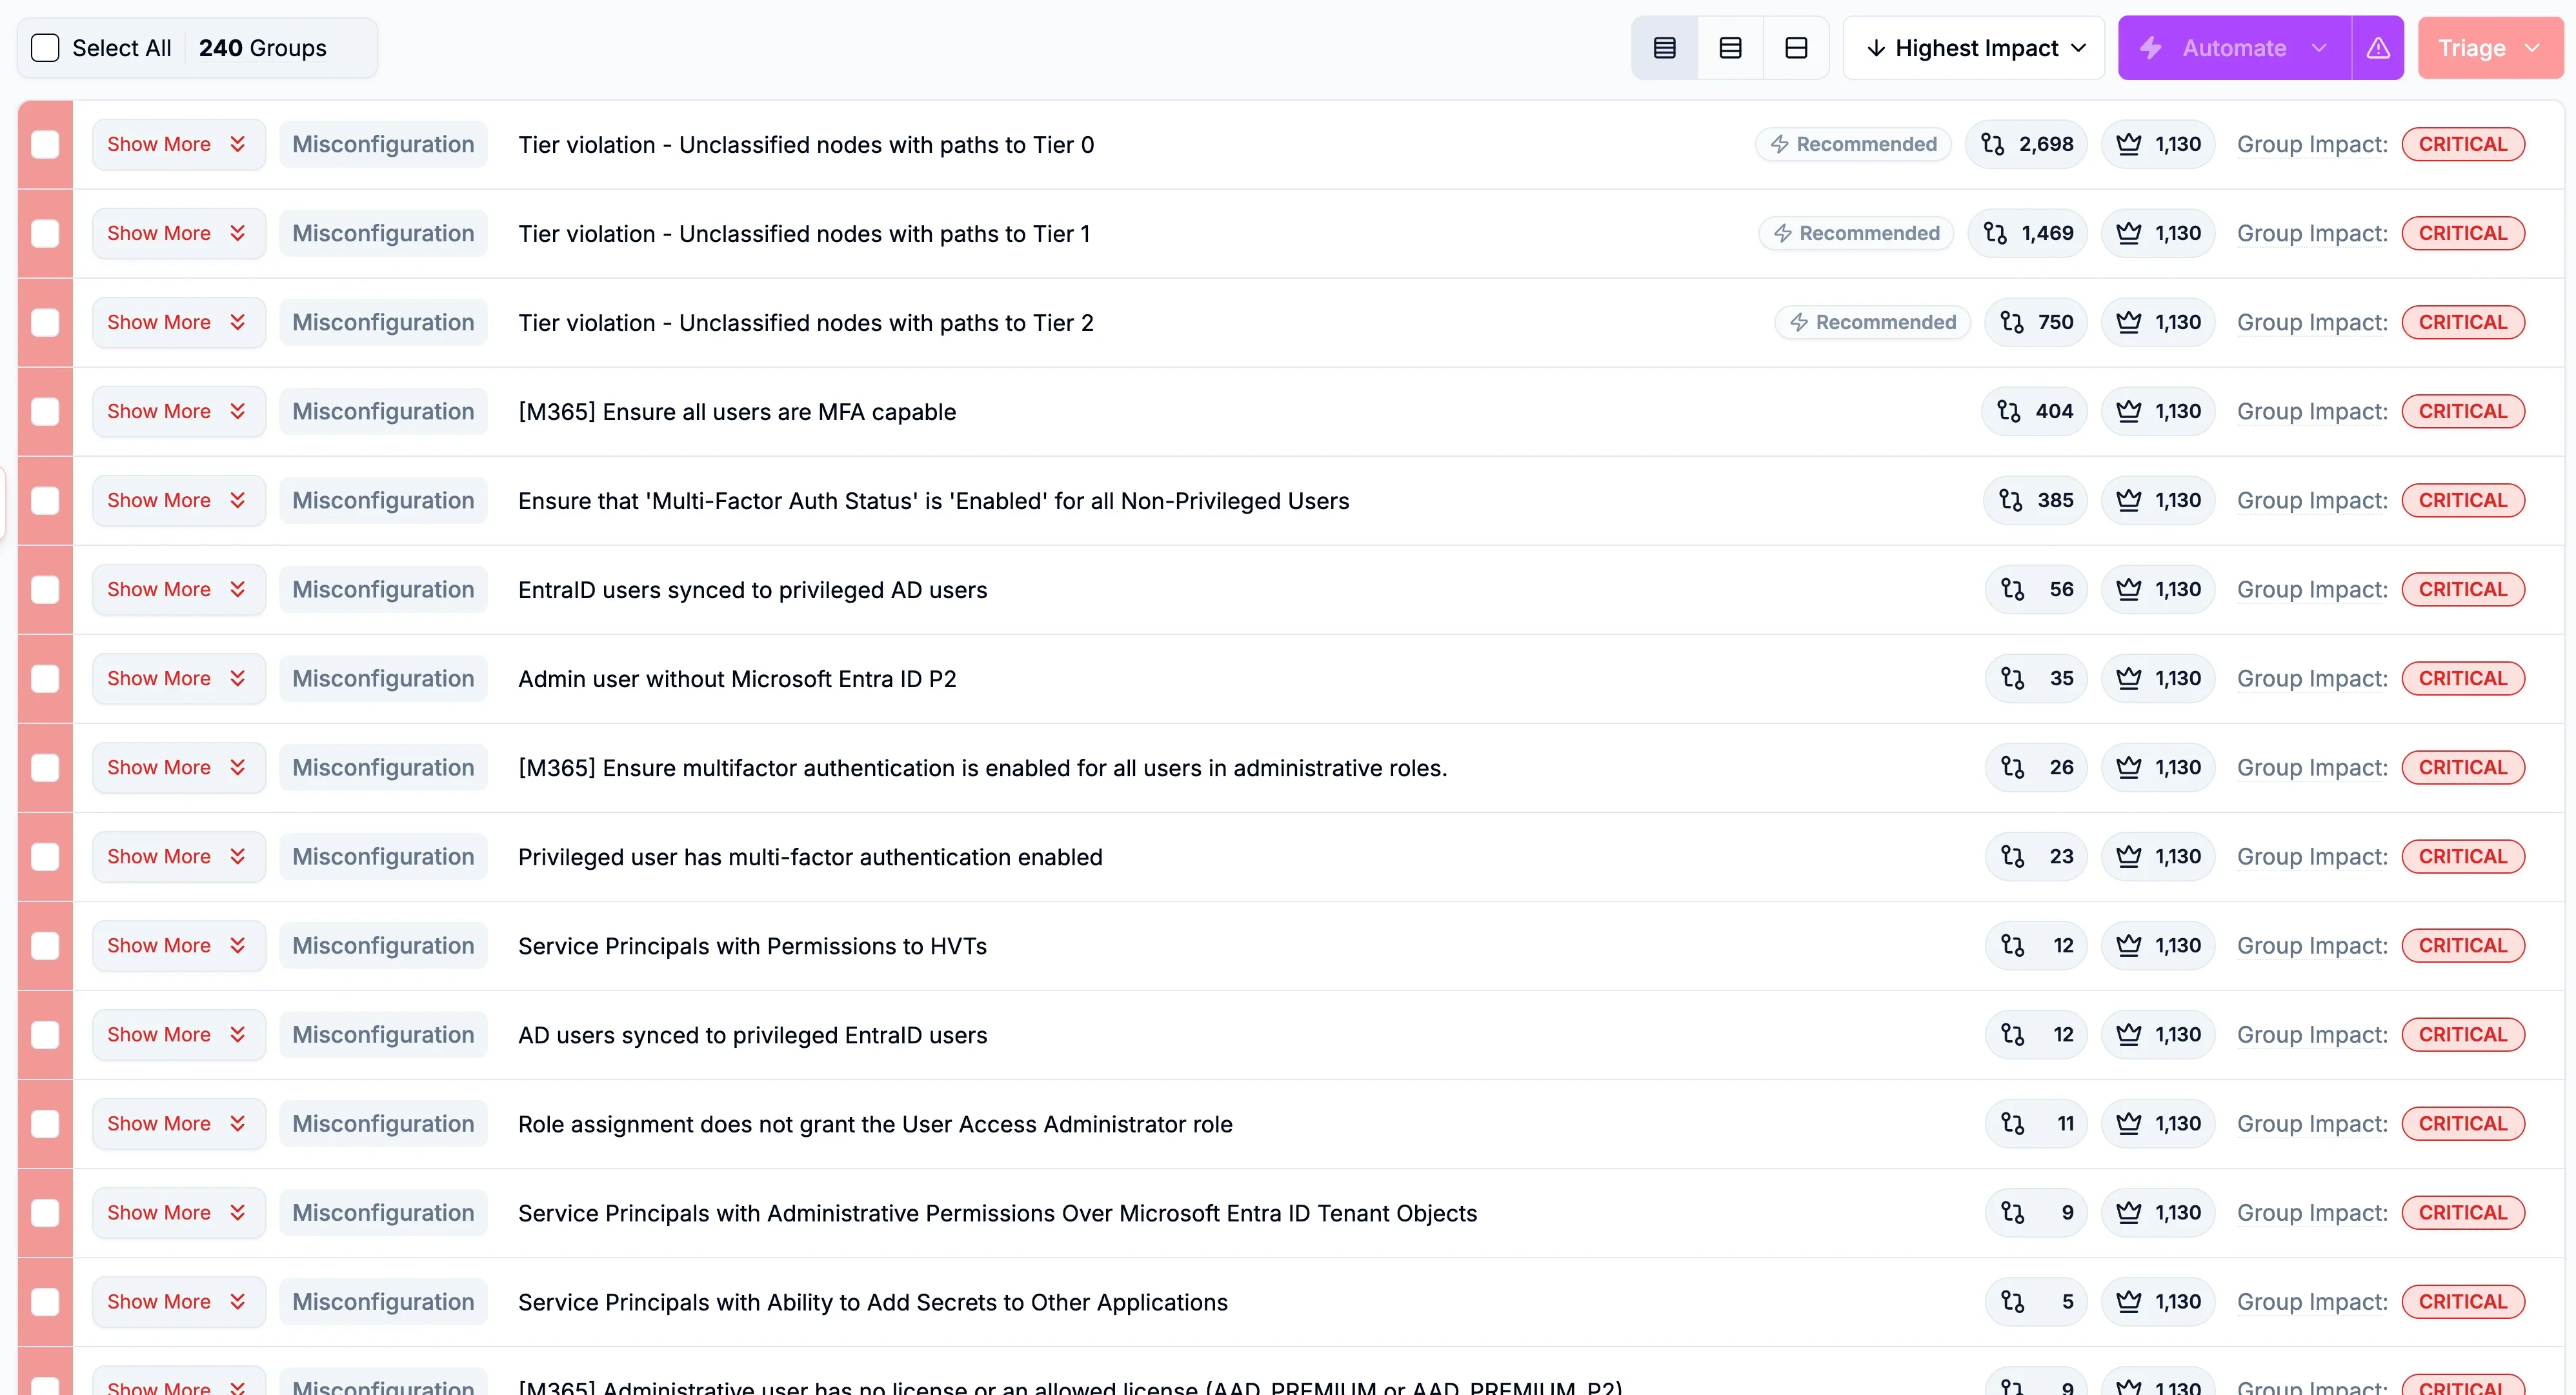
Saporo prioritizes exposure using reachability, privilege propagation, impact on critical assets, and the amount of attack surface a change can remove. This helps teams focus on the relationships that materially reduce risk.

Yes. Saporo can analyze Entra ID and Azure independently. Connecting Active Directory adds hybrid identity relationships, while cloud identities, permissions, misconfigurations, and attack opportunities can be analyzed on their own.

Saporo represents supported role relationships with PIM activation and approval context. Administrative Units add scope to delegated administration, helping teams review privilege beyond tenant-wide roles.

Reduce identity exposure before it becomes an attack

Book a demo