PREEMPTIVE IDENTITY SECURITY PLATFORM

See identity exposure as one connected attack surface

Saporo collects identity context across your hybrid environment, connects identities, permissions, relationships, misconfigurations, and critical assets in one attack graph, then shows your team which changes reduce the most risk.
Active Directory
Entra ID
Azure
Microsoft 365

AWS
Google Cloud
Google Workspace

Windows Local
SMB Shares
AD Certificate Services

FROM DATA TO ACTION

A complete loop for preemptive identity exposure management

  1. Collect and discover

    Agentless collectors gather human and non-human identities, permissions, configurations, relationships, activity, and critical assets across connected on-premises and cloud environments.
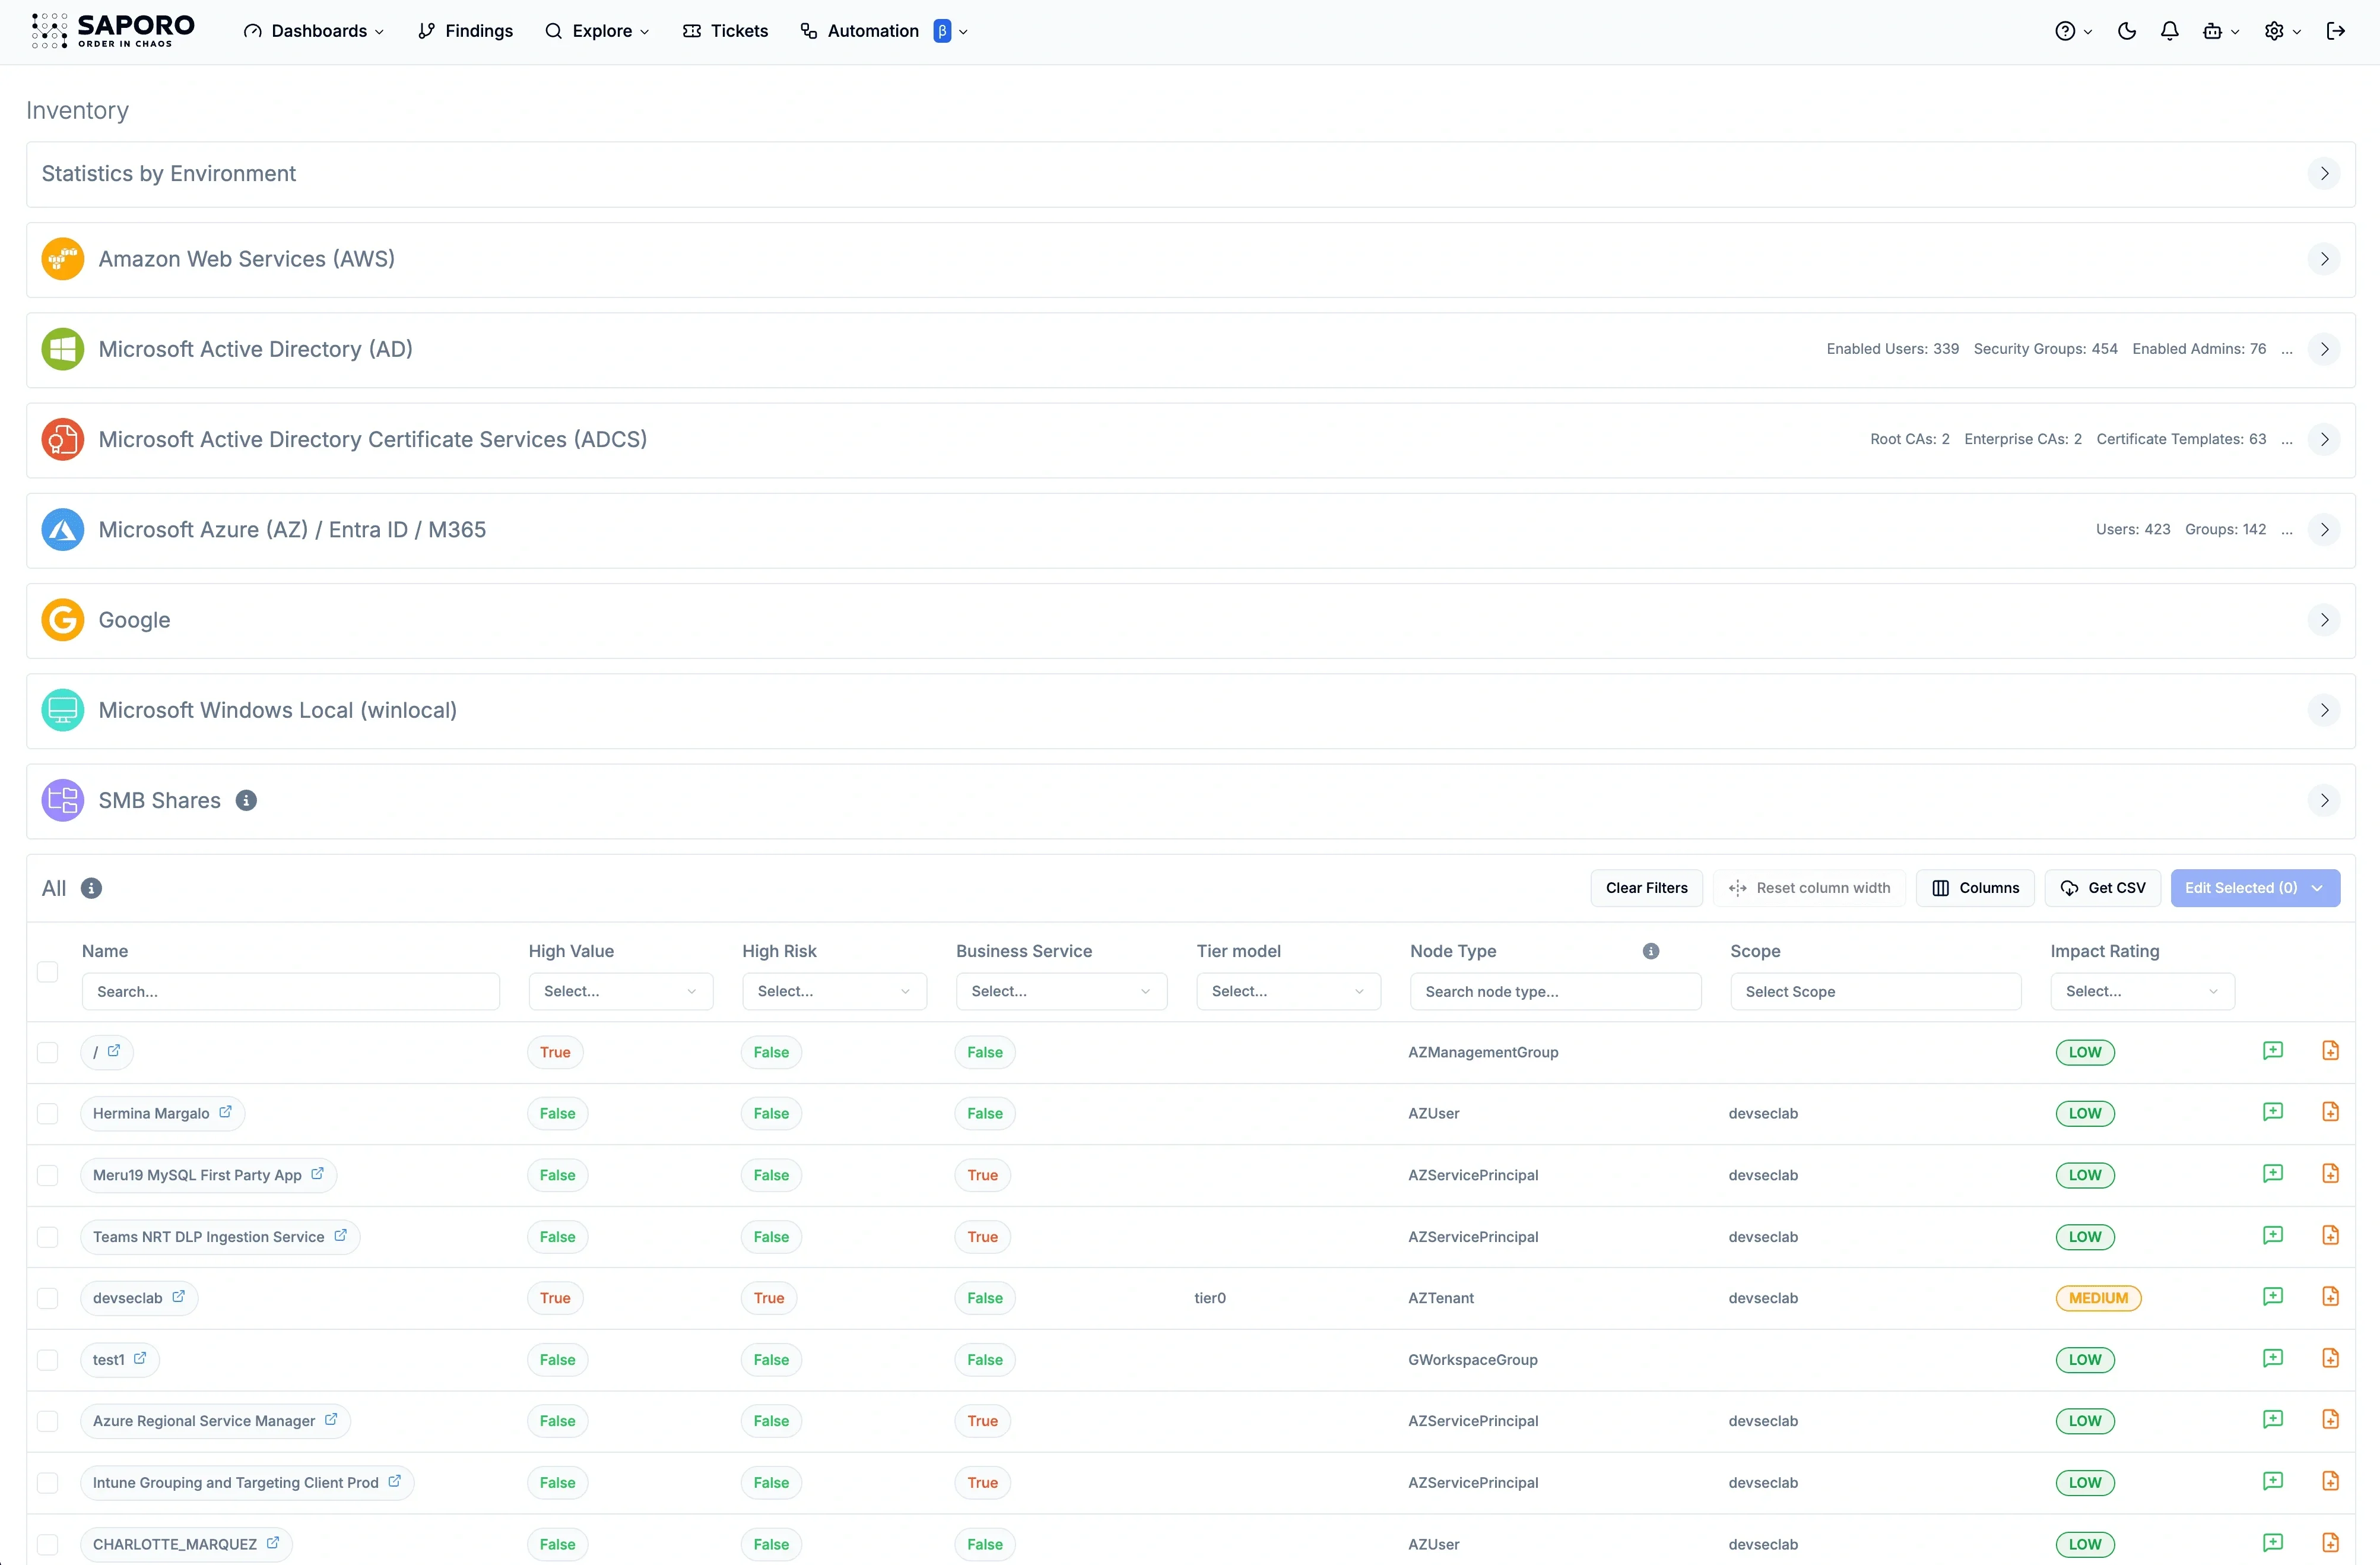
    Saporo Inventory view listing connected identity sources: AWS, Active Directory, ADCS, Azure, Entra ID and Microsoft 365, Google, Windows Local, and SMB Shares
    Inventory

    Example environment data

  2. Graph and reveal

    Saporo normalizes the data into an enterprise-scale attack graph that shows how attackers can combine identity relationships and weaknesses to reach High Value Targets.
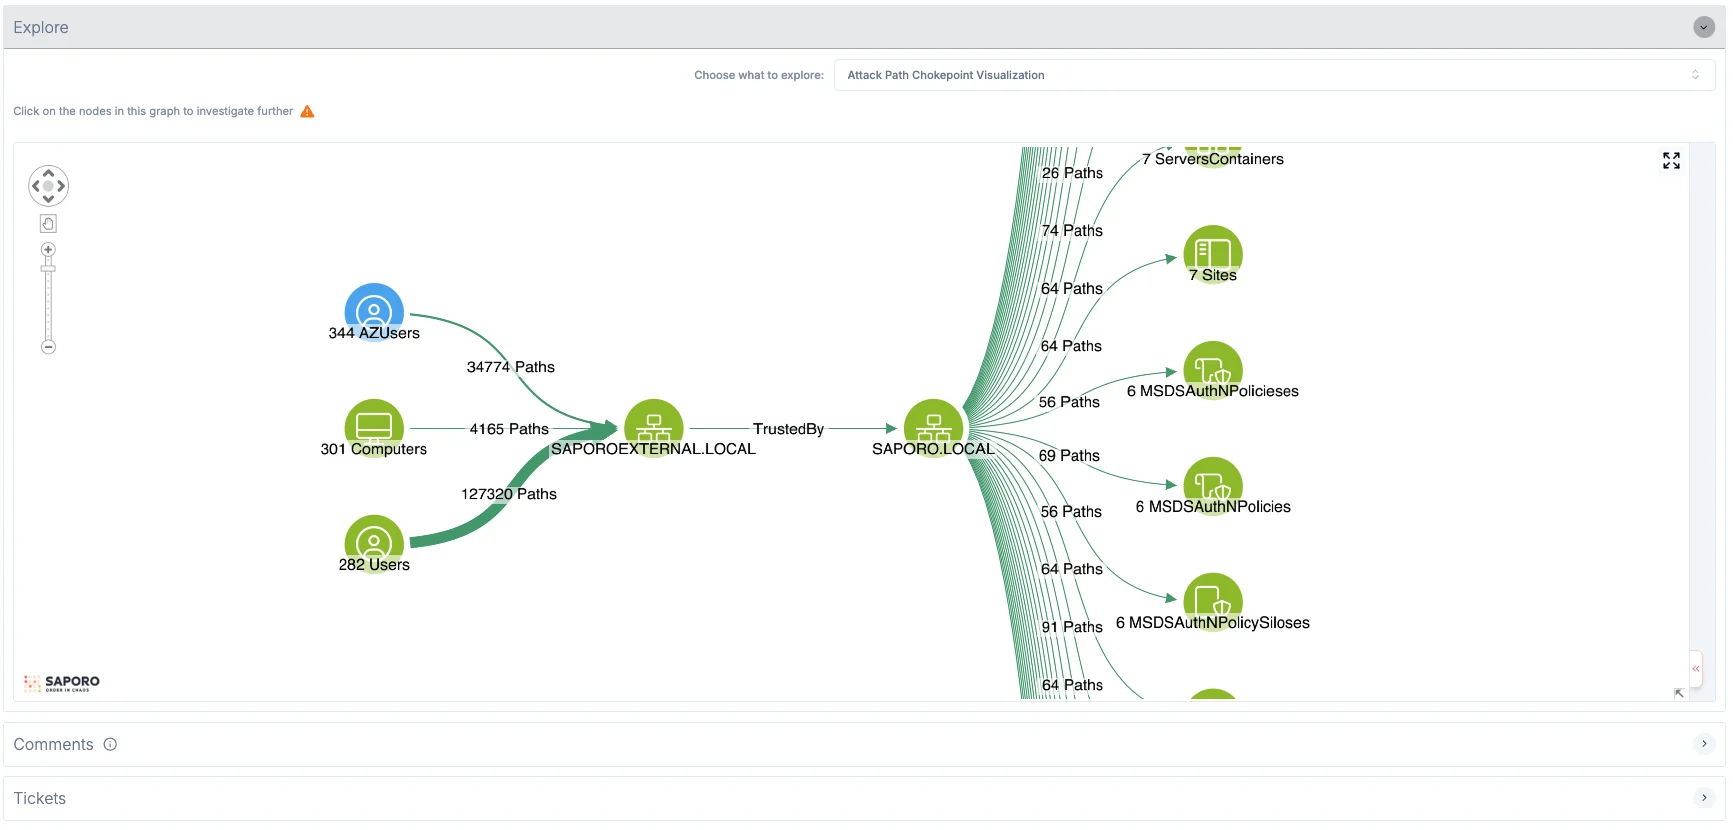
    Saporo Explore graph showing an attack path chokepoint where users, Azure users, and computers reach SAPOROEXTERNAL.LOCAL and SAPORO.LOCAL through thousands of paths
    Explore graph

    Example environment data

  3. Prioritize and validate

    Saporo ranks attack opportunities by reachability, propagation potential, and impact, using predictive attack path analysis to focus on attack and access paths to critical assets.
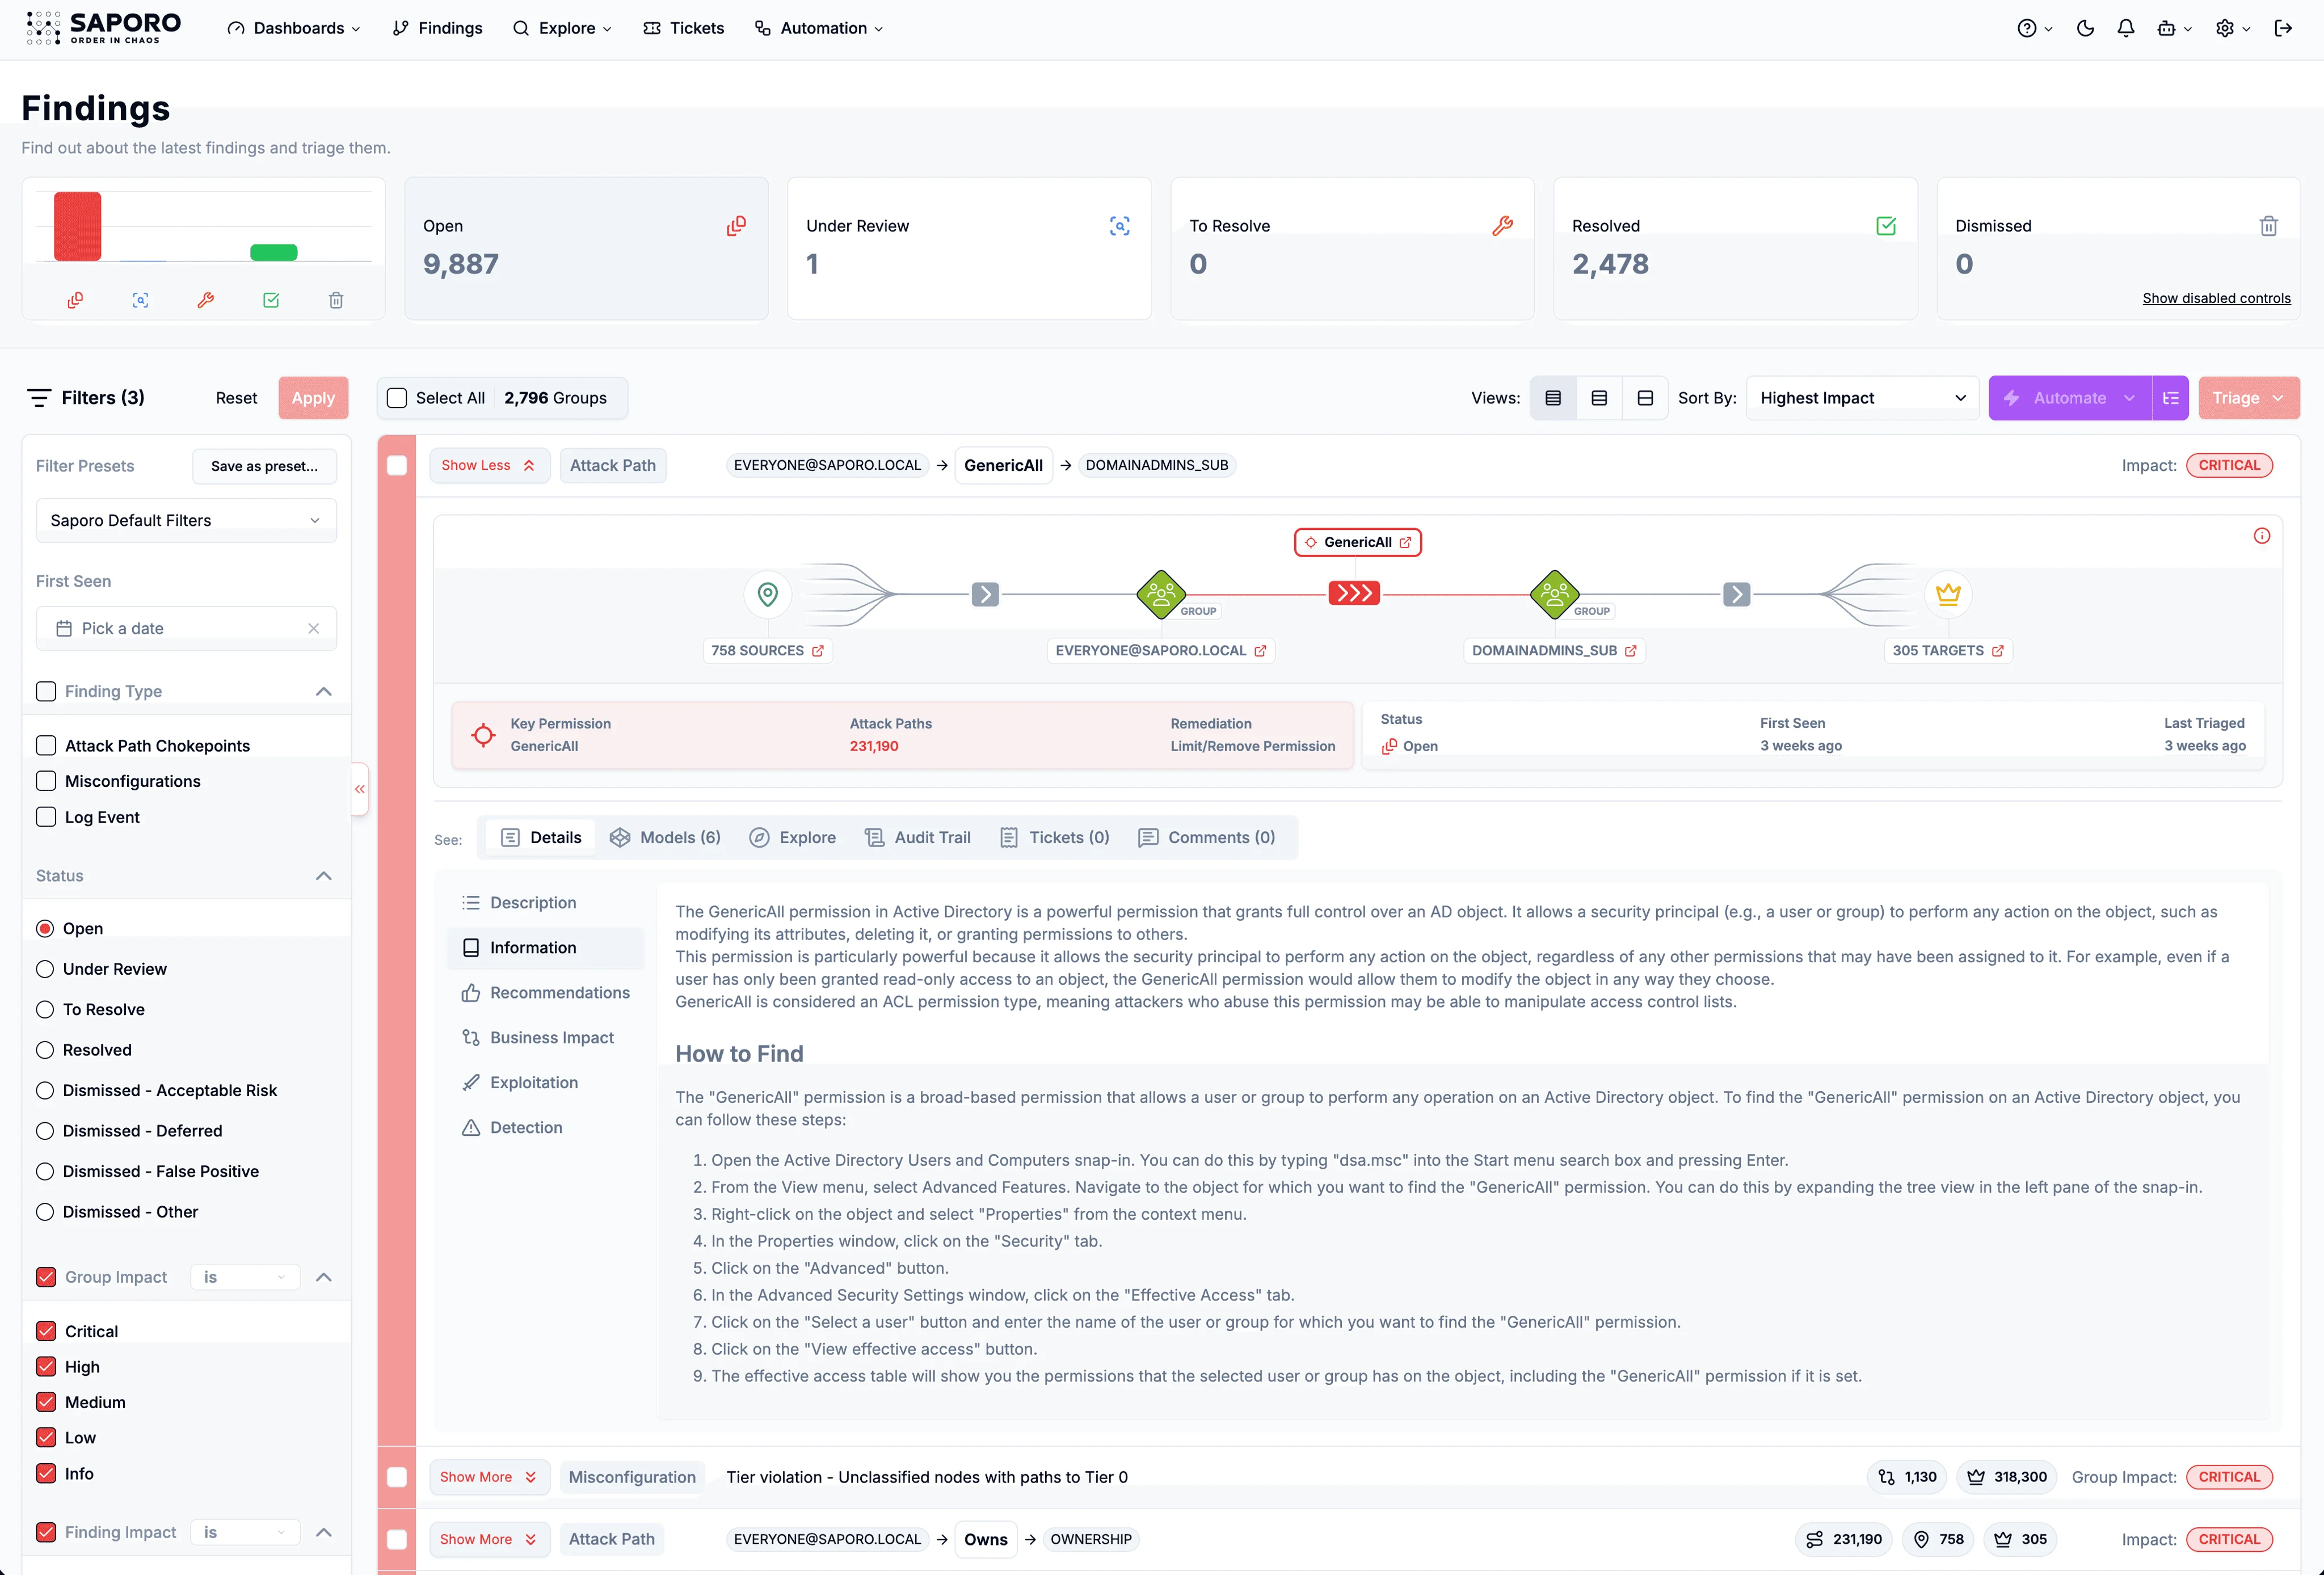
    Saporo Findings view showing a critical attack path from EVERYONE to DOMAINADMINS_SUB through a GenericAll permission, with 231,190 attack paths and the recommended remediation
    Findings

    Example environment data

  4. Mobilize and measure

    Guided and automated workflows reduce exposure at scale, with approvals where needed. Track progress through Resistance Score, compliance, tiering, and operational time savings.
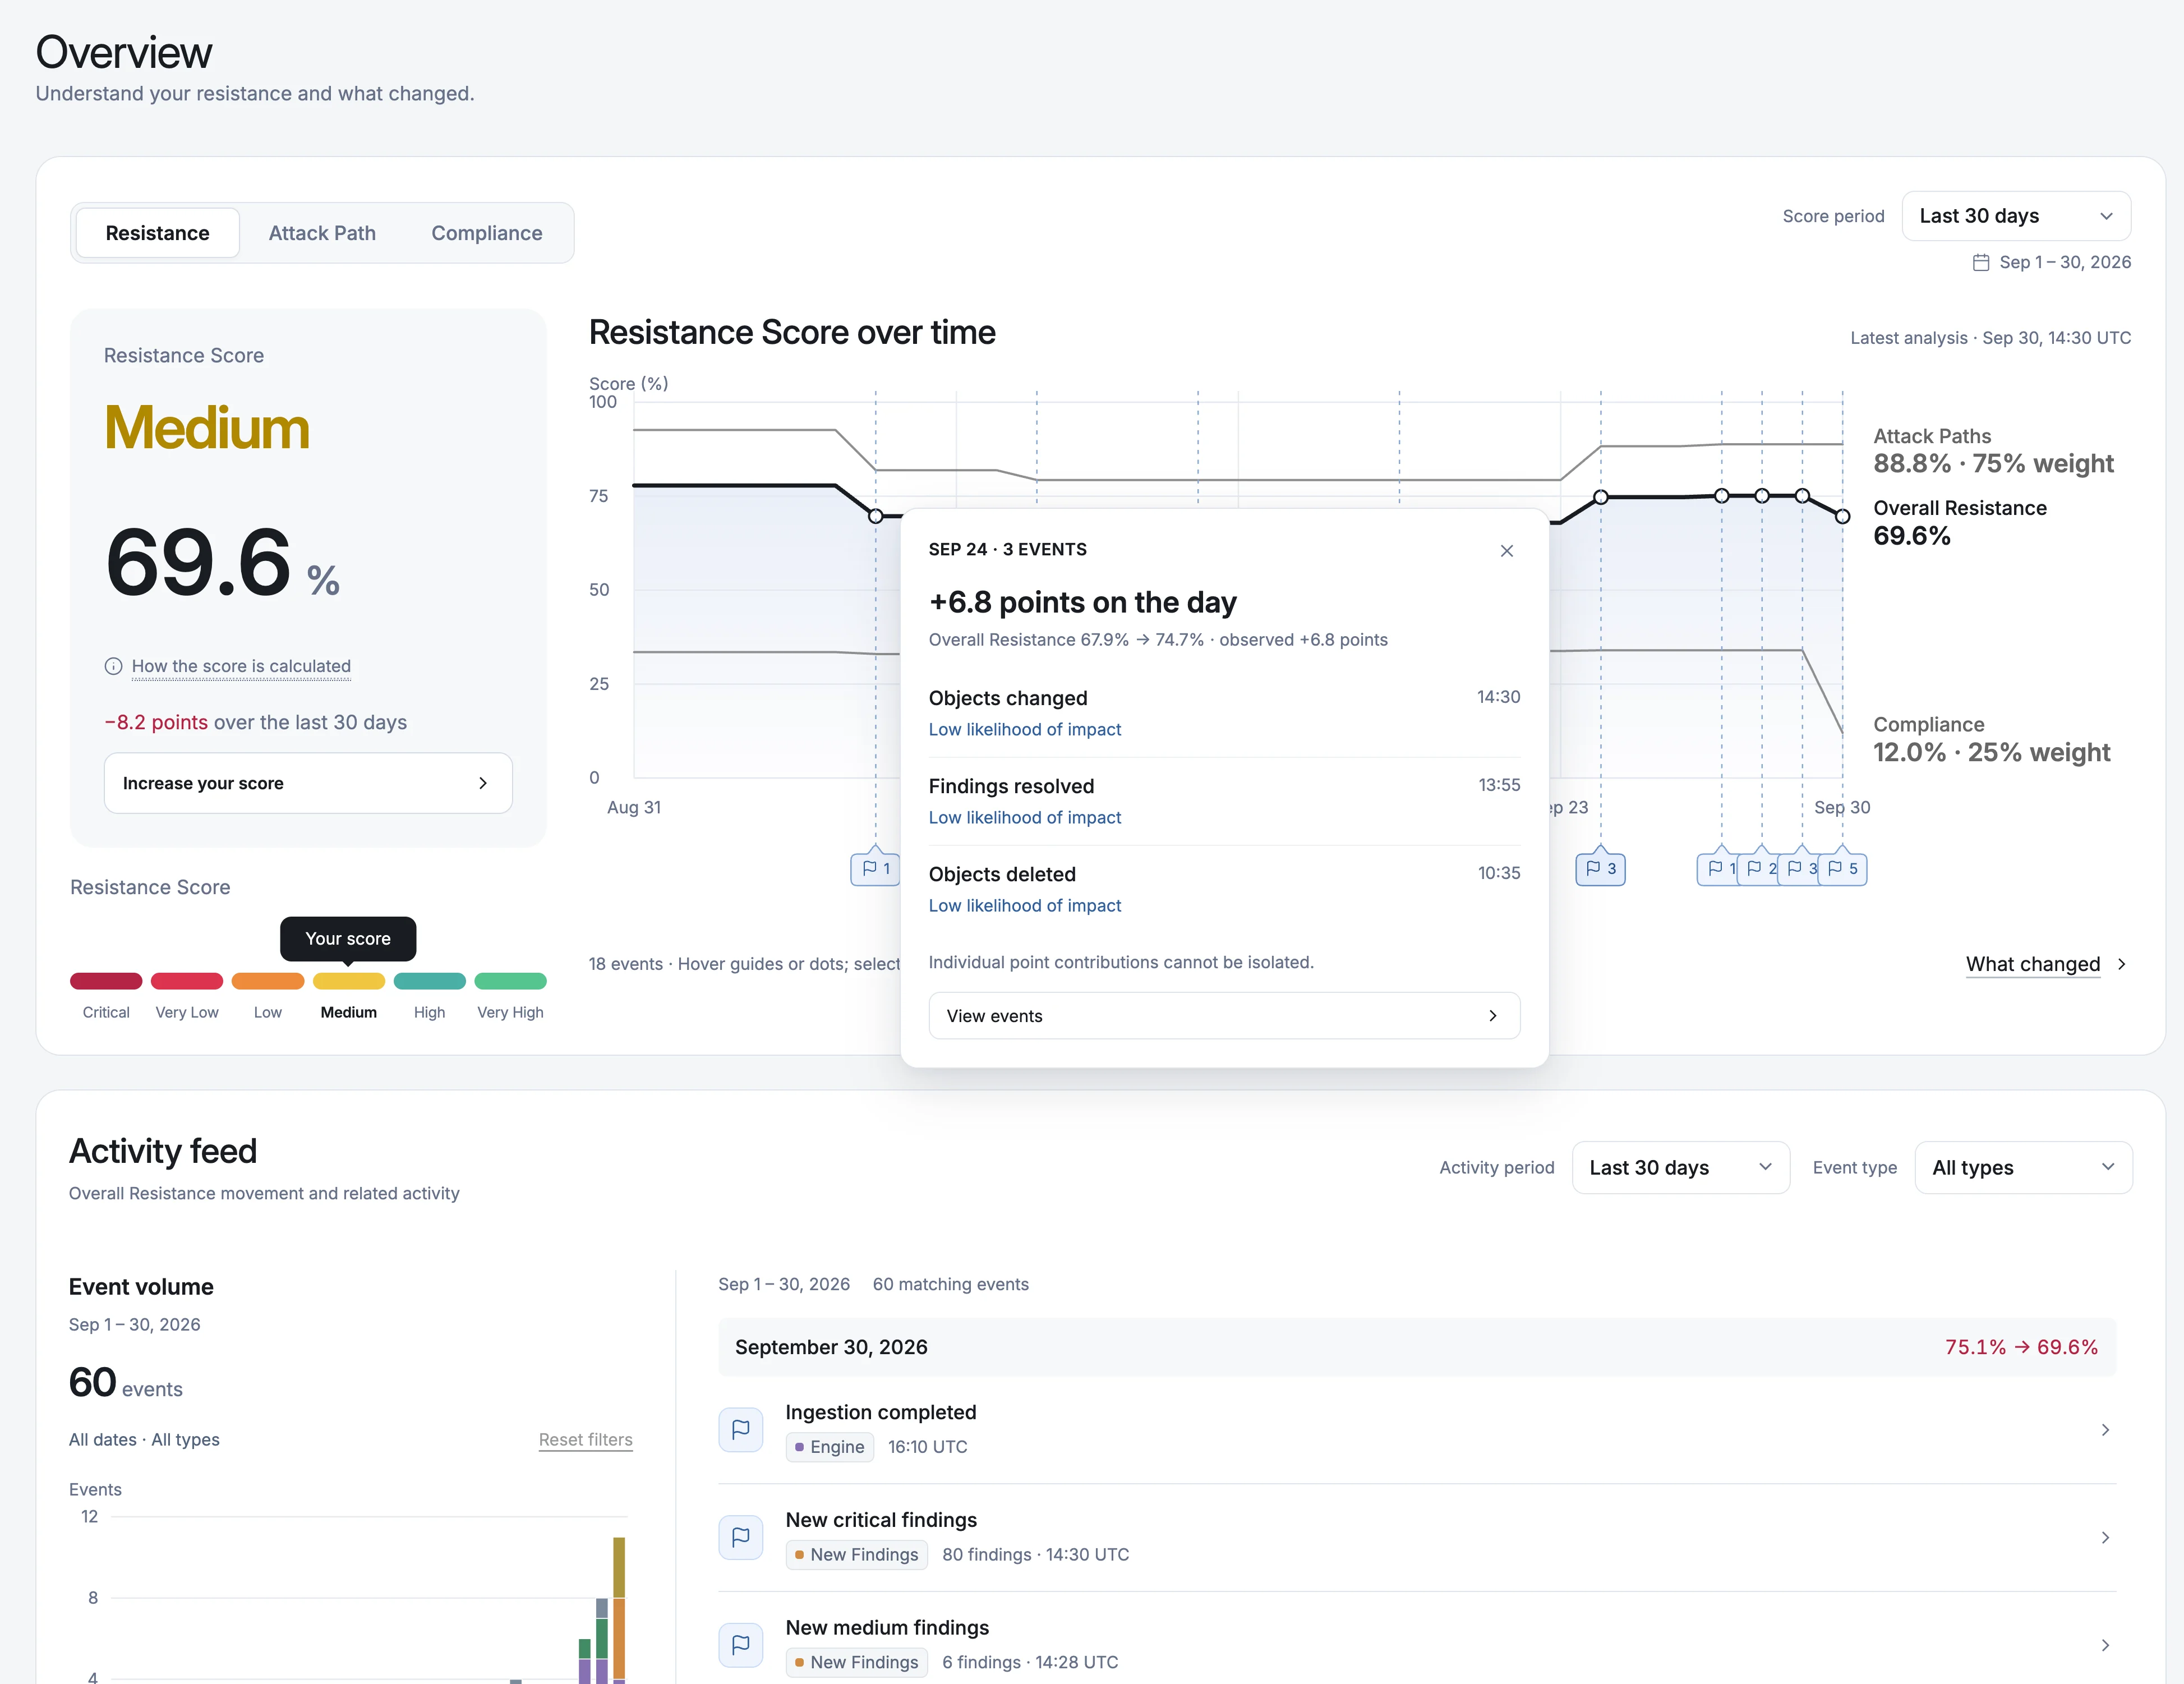
    Saporo Overview showing a Medium Resistance Score of 69.6%, the Resistance Score over time with the events behind one day's change, and the activity feed
    Overview

    Example environment data

How Saporo works

See which attack opportunities matter most

Saporo evaluates attack opportunities using reachability, propagation potential, and impact to show how attackers can gain access, how far compromise can spread, and which critical assets are exposed.

Reachability analysis

Reachability

Trace viable attack and access paths to an exposed identity.

PLATFORM CAPABILITIES

Explore the system behind exposure reduction

01 / 09

Graph Engine & Analysis

At the core of Saporo is an enterprise-scale graph engine that connects identities, permissions, relationships, activity, and misconfigurations into a unified model of attack opportunities.

  • Unify fragmented identity data in one continuously updated graph
  • Cover identities (human and NHI) across hybrid environments
  • Remediate the attack opportunities with the greatest impact
Expanding identity graphA single identity relationship expands from left to right into a wide graph of interconnected identities, permissions, controls, and resources.

Automation

Automate identity exposure reduction

Saporo

Automate remediation

  1. 01 · Trigger

    Choose a trigger

    Start on a prioritized finding, schedule, or webhook.

  2. 02 · Rules

    Apply your rules

    Add conditions and human approval where needed.

  3. 03 · Action

    Run the action

    Create a ticket, notify a team, enrich context, or remediate.

  4. 04 · Track

    Track execution

    Review run status, logs, and remediation progress.

Example workflows

01 / 06

Mark an account as sensitive
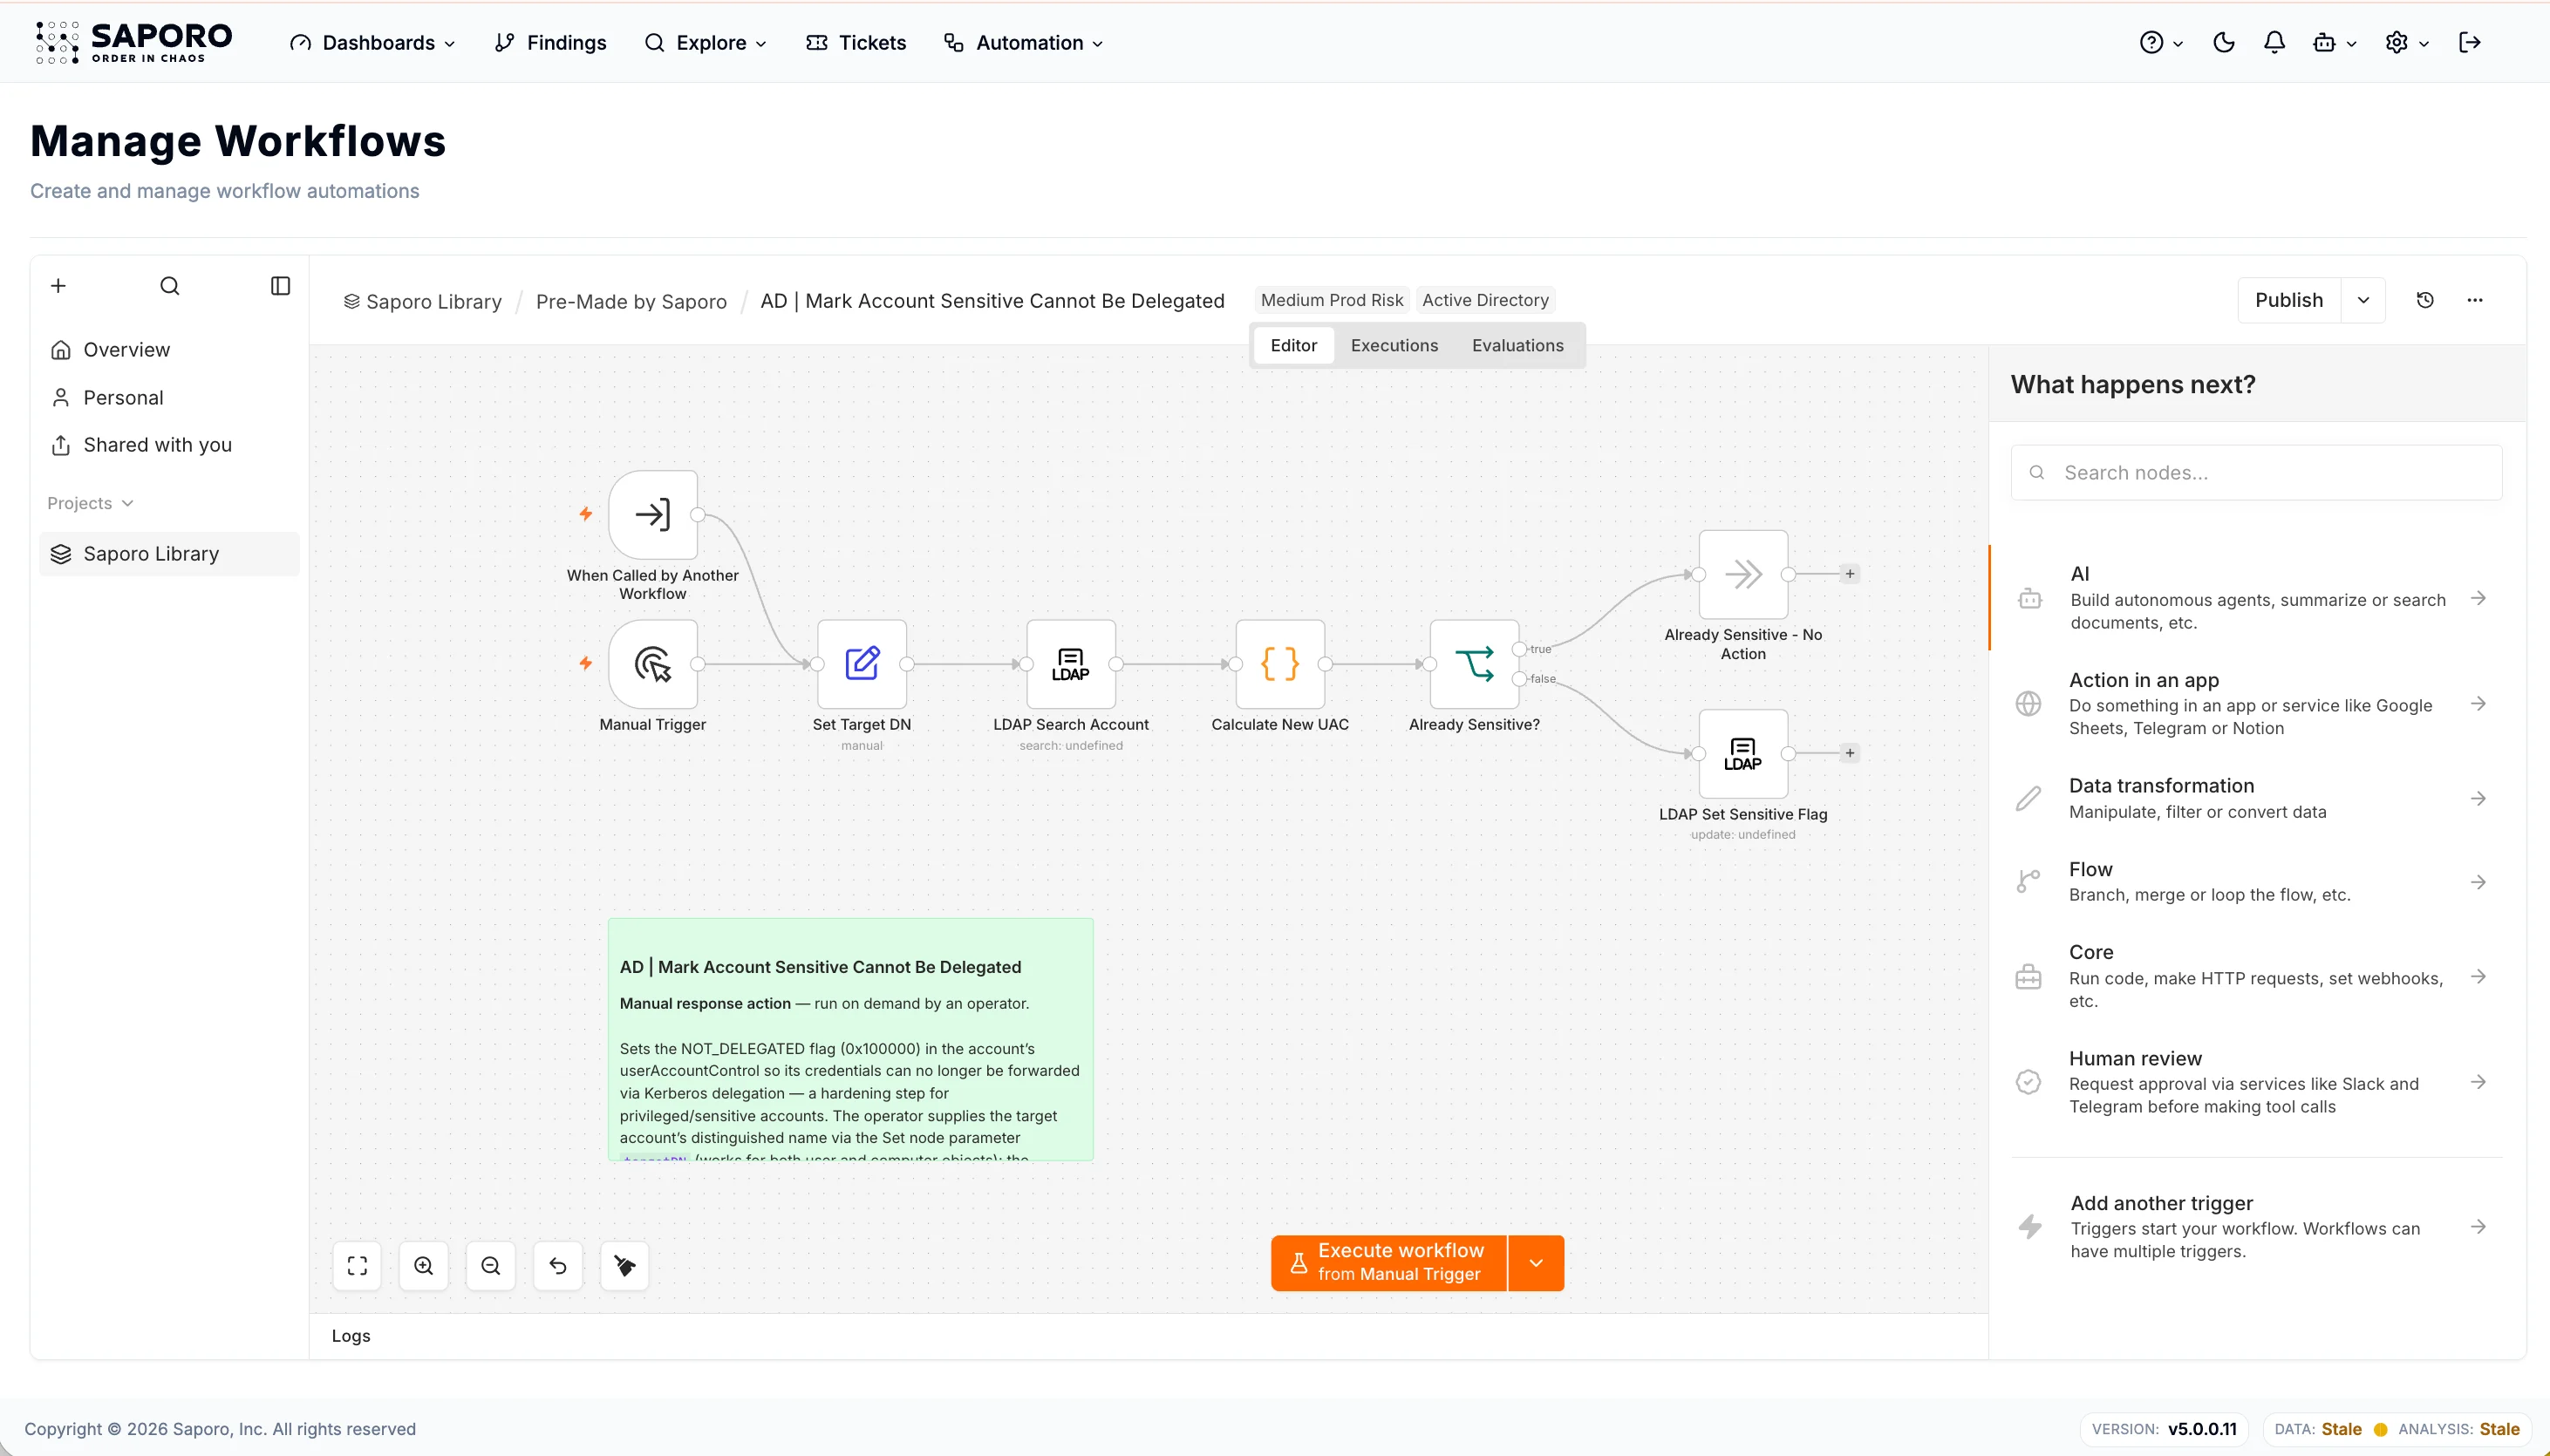
Saporo workflow editor showing an Active Directory workflow that marks an account as sensitive and cannot be delegated, with a branch that skips accounts already flagged
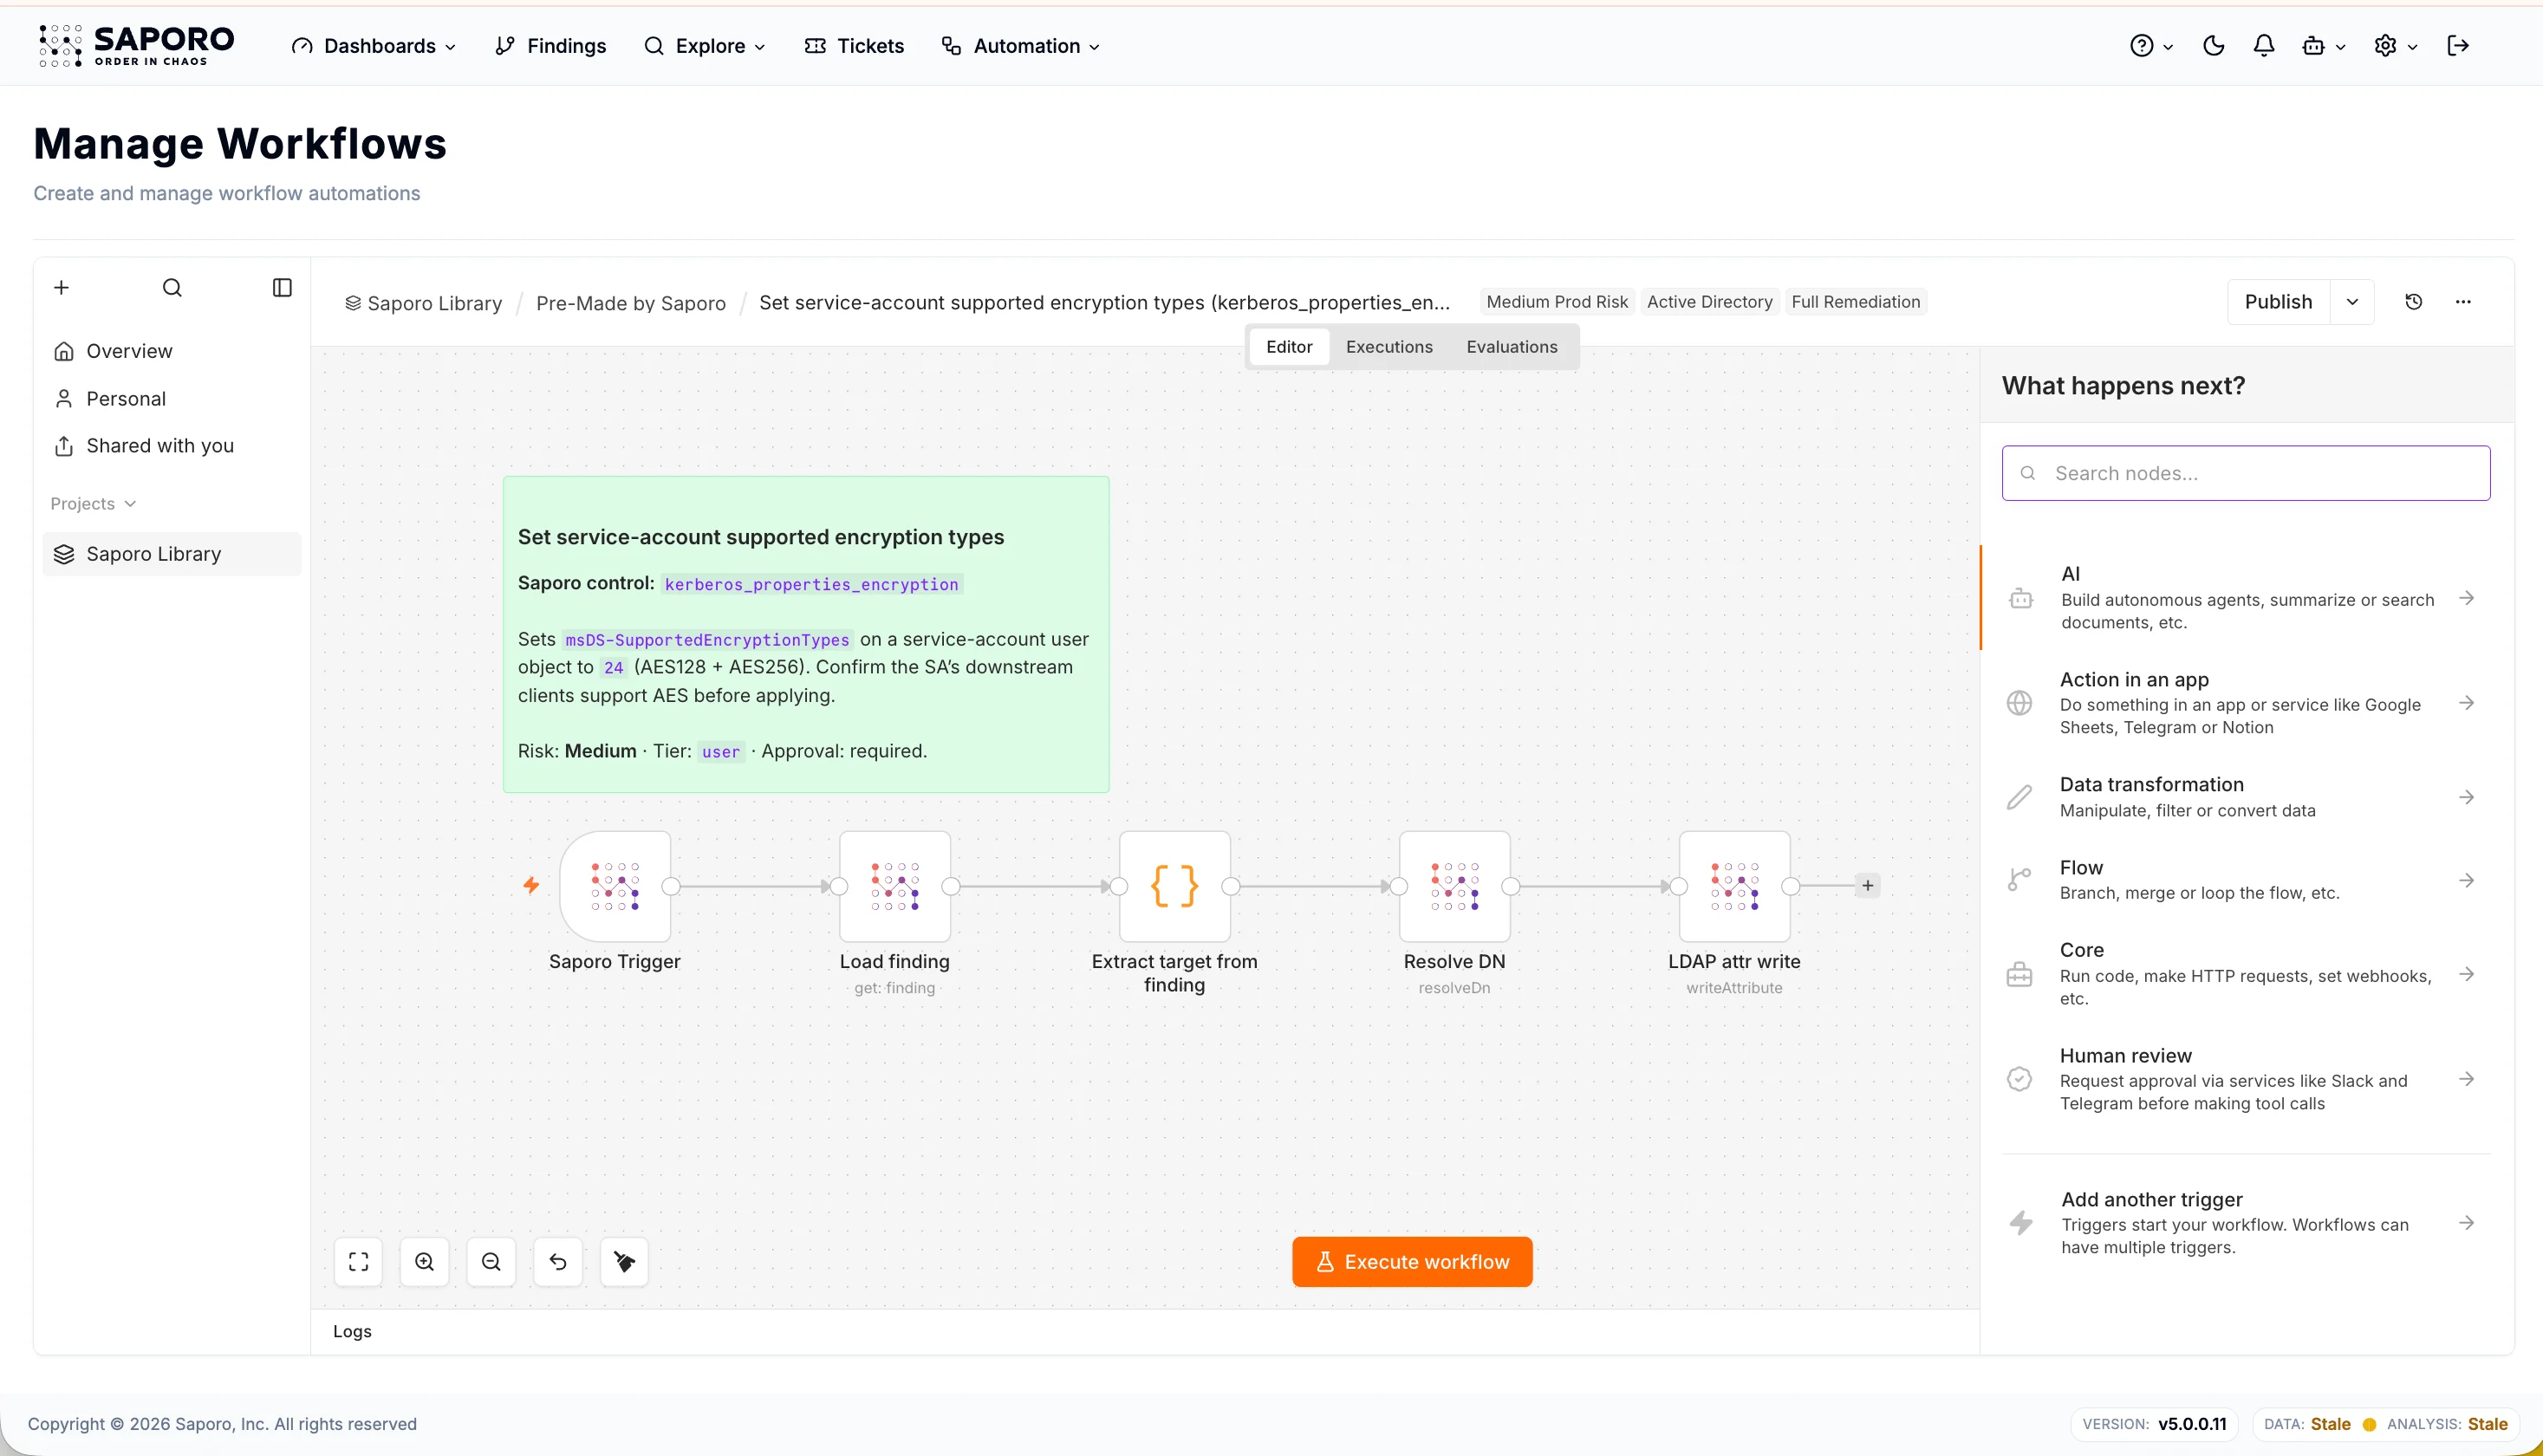
Saporo workflow editor showing a workflow that sets supported Kerberos encryption types on a service account, with approval required
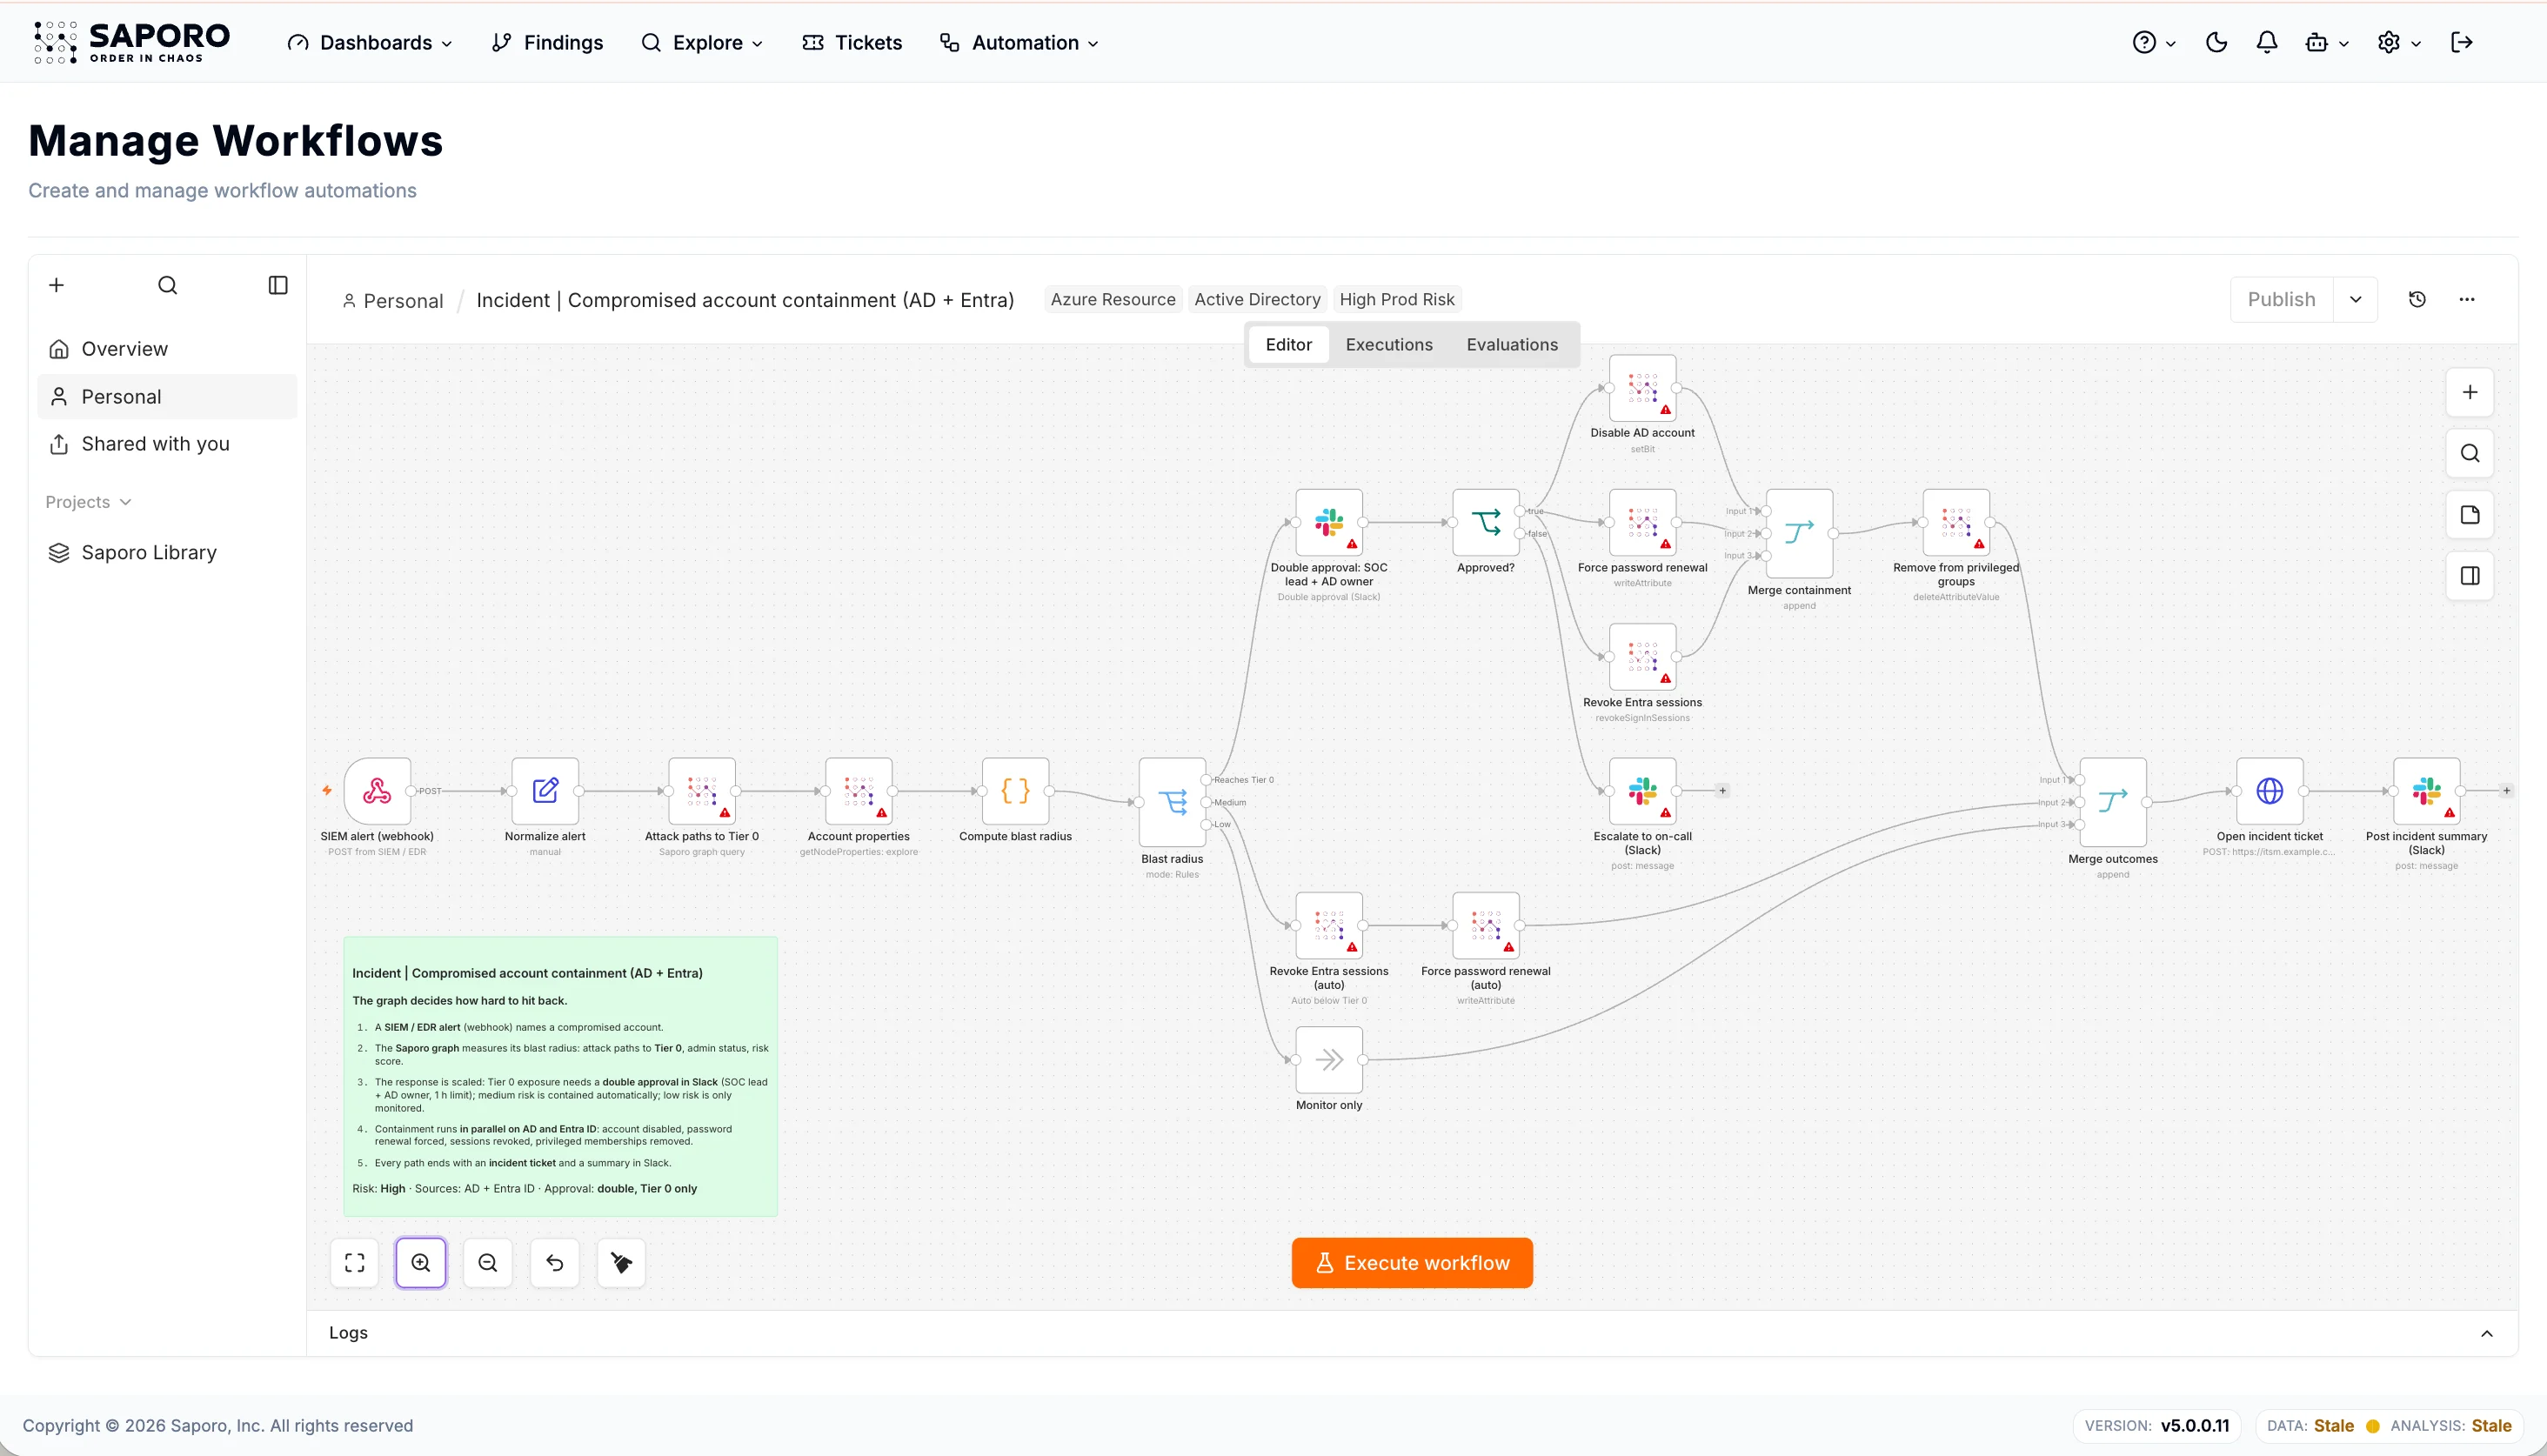
Saporo workflow for containing a compromised account across Active Directory and Entra ID, with approval steps for sensitive actions.
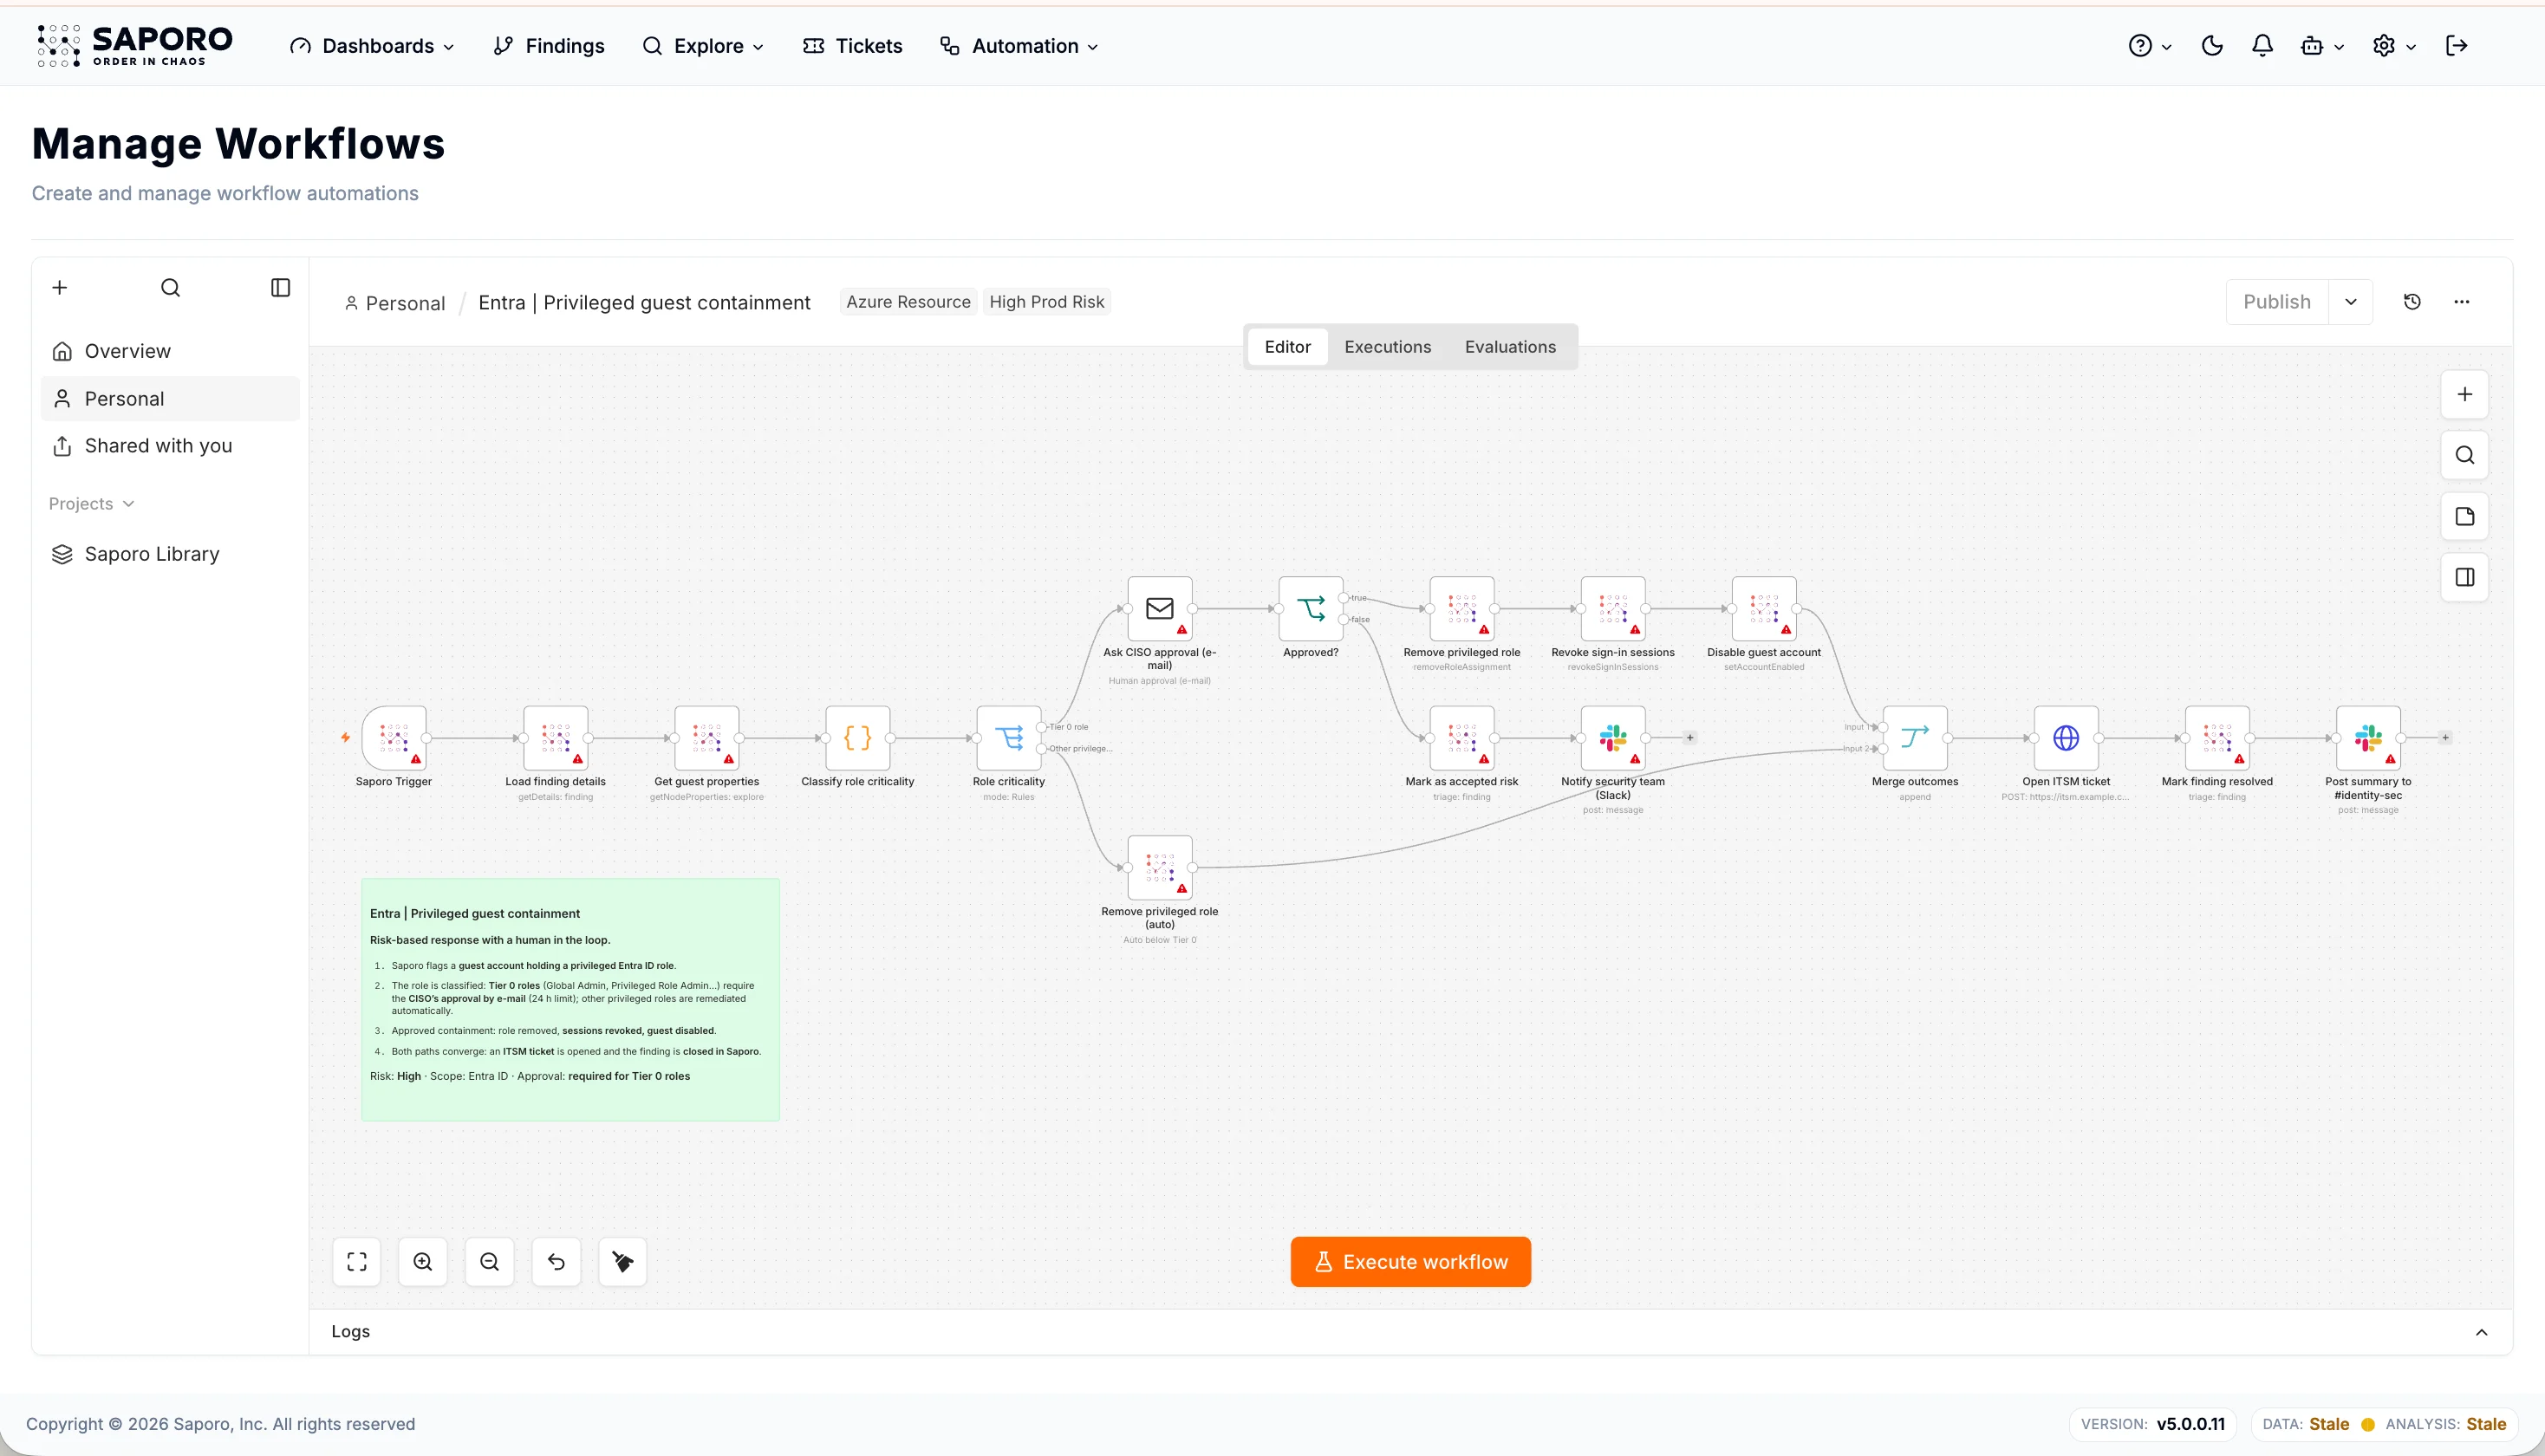
Saporo workflow editor showing an Entra ID workflow that classifies a guest's privileged role, requests CISO approval by email for Tier 0 roles, removes the role, revokes sessions, and opens an ITSM ticket
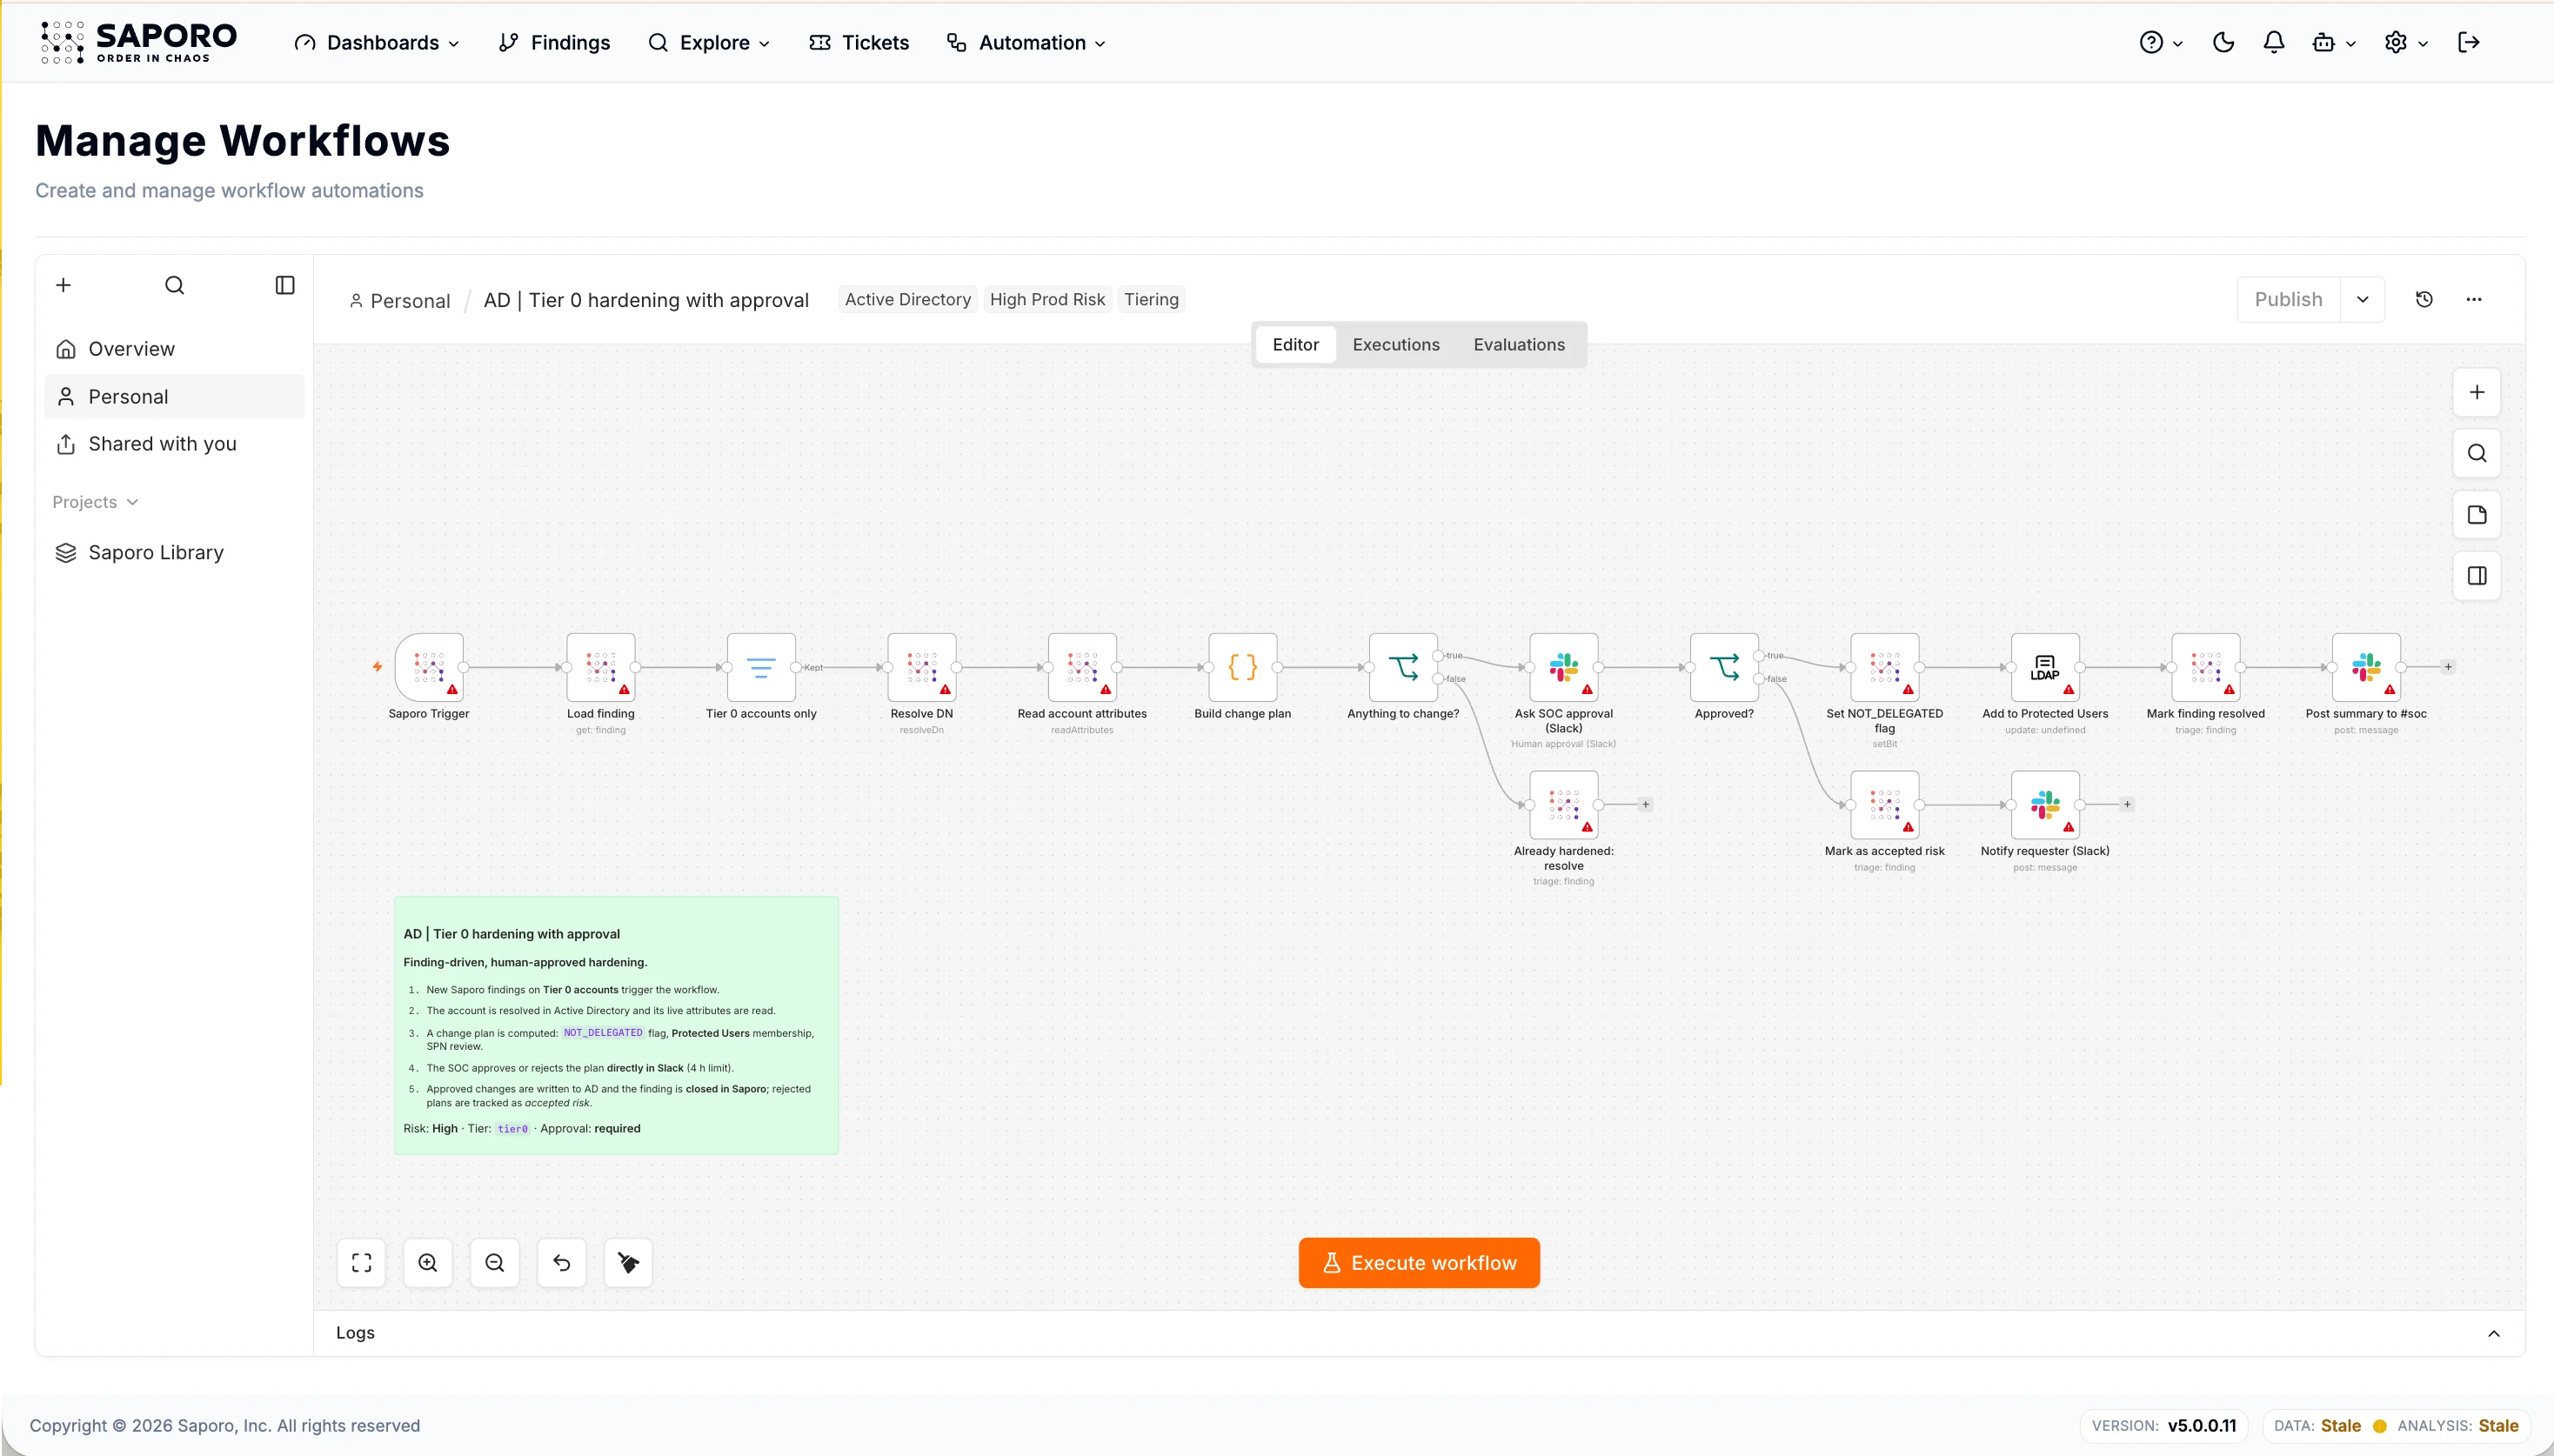
Saporo workflow for hardening Tier 0 Active Directory accounts, with SOC approval before applying the changes.
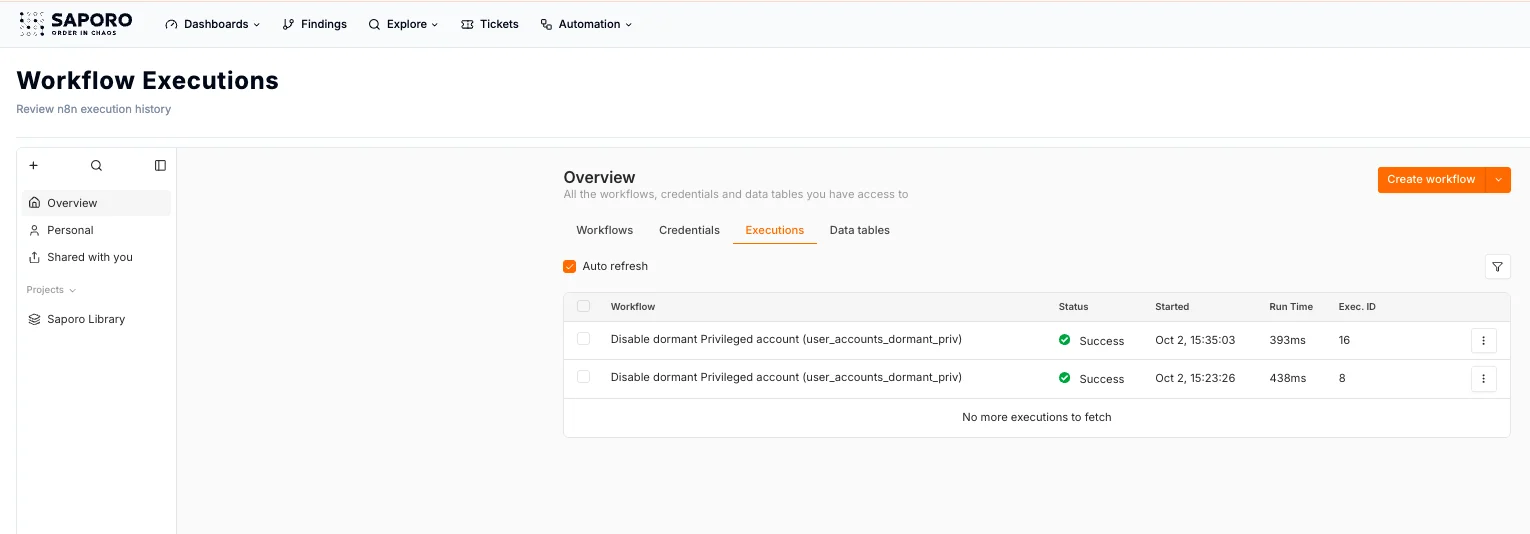
Saporo Workflow Executions view listing successful runs with start time, run time, and execution ID

Keep people in control

Place approval gates anywhere in a workflow. Routine remediation keeps moving while sensitive actions wait for a person to approve them.

  • Email
  • Microsoft Teams
  • Slack
  • ITSM
  • Multi-stage chains

Governed by design

Control who can build, run, approve, and manage workflows.

  • Granular workflow and API RBAC
  • Scoped API keys
  • Secure secret management
  • Approval gates for sensitive actions

Every run on record

An audit trail records each execution, showing what changed and when.

  • Workflow runs and status
  • Retries and failures
  • Step-by-step run details
  • Remediation coverage

Awards & recognition

  • KuppingerCole Analysts Rising Star 2026

    Rising Star 2026

    KuppingerCole Analysts

  • Sifted 250, Europe's fastest-growing startups 2025

    #82 fastest-growing EU startup

    Sifted 250, 2025

  • Prix Coup de Coeur, InCyber Forum Europe 2024

    Jury's Favorite Award

    InCyber Forum 2024

  • Tech4Trust Season 3 Winner

    Season 3 winner

    Tech4Trust, Trust Valley

  • Trust Valley Days

    Best Cyber Security Start-Up

    Trust Valley Days 2022

  • ISO 27001 certified badge

    ISO 27001 certifiedSince 2025

  • SOC 2 Type II compliance badge, powered by VantaComing soon

    SOC 2 Type IIComing soon

  • GDPR Compliant badge

    GDPR compliantSince 2022

  • ECSO Member

    ECSO memberSince 2026

Reduce identity exposure before it becomes an attack

Book a demo