Faster reporting
Export reports by framework, domain, or tenant using the latest assessed data. Reduce time spent gathering evidence and preparing for audits.
- Export by compliance framework
- Export by scope
- Reports from the latest data

Compliance Readiness
Saporo continuously assesses identity security against framework requirements and prioritizes fixes by exploitability, blast radius and impact. Automate remediation, reduce exposure and demonstrate progress between audits.
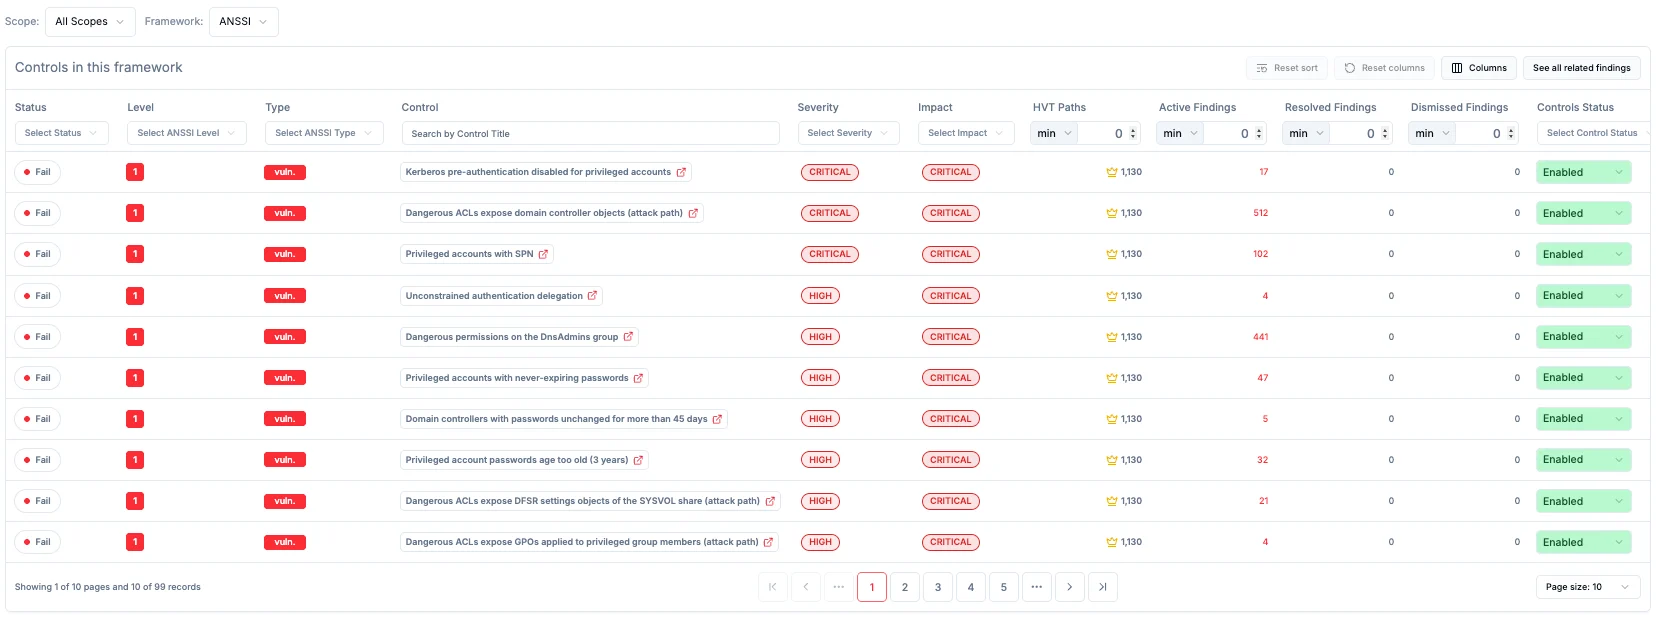
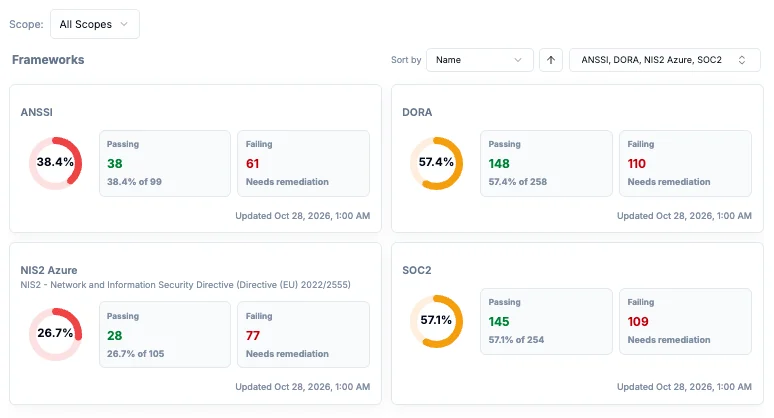
See where control gaps affect your frameworks and expose critical assets. Prioritize fixes and track remediation progress in dedicated dashboards.
Assess your posture and prioritize fixes with guided or automated remediation.
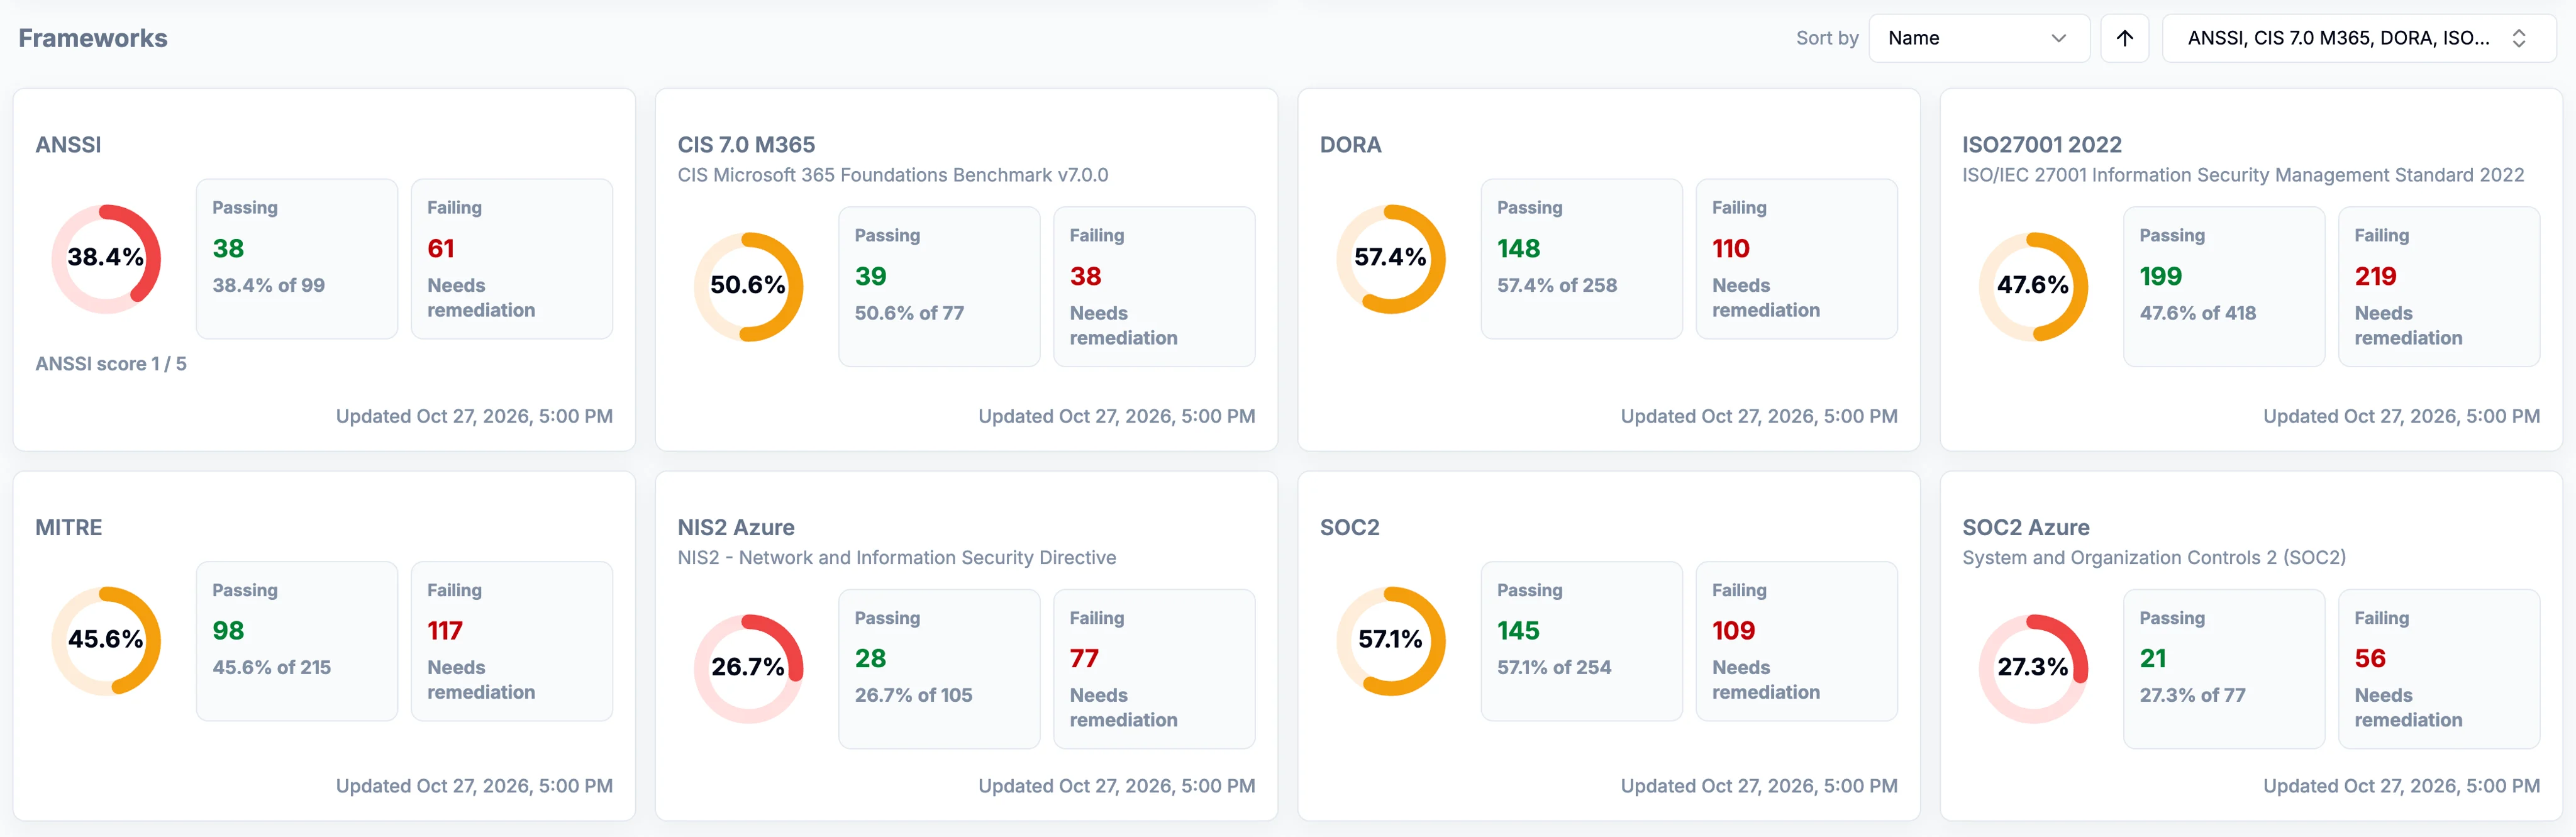
Dashboards / FrameworksExample environment and data.
New identities, permissions and configuration changes can reopen control gaps. Keep remediation priorities and leadership reports aligned with your latest assessment.
800+
Security controls prioritized by reachability and blast radius
40+
Framework versions mapped with prioritized remediation plans
Daily
Automated identity security posture assessments
Export reports by framework, domain, or tenant using the latest assessed data. Reduce time spent gathering evidence and preparing for audits.
Prioritize control gaps by risk with a clear remediation roadmap. Reduce repetitive work and save your team time by automating supported fixes.
Catch new and recurring gaps with daily checks between audits. Track remediation progress and give leadership a current view of your posture.
Customer results · Healthcare · France
After years of manual assessments, a major French hospital group still struggled to meet its ANSSI security objectives. With Saporo, the team connected control gaps to attack paths, prioritized remediation and achieved those objectives within one year.
The team now manages identity posture continuously, addressing new exposures and keeping audit reporting current.
Compliance Readiness Q&A
Prepare for audits with concrete evidence from across your on-premises and cloud environments. Saporo maps technical findings to frameworks including ISO 27001, SOC 2, CIS and ANSSI. Support access reviews and audit requests with evidence covering dormant accounts, privileged access, authentication policies, secure configuration, application permissions, audit logging and external sharing. Export reports by framework, domain or tenant, with control results and historical trends. Combine reports with screenshots of findings and configurations to substantiate your answers to auditors. Reuse relevant evidence across framework requirements and give auditors and leadership a clear view of the controls assessed, the gaps identified and progress between audits.
No. Saporo provides technical assessments, remediation tracking and reports that support your compliance program and formal audits.
More than 40 compliance framework versions, including ANSSI, ISO 27001, NIS2, MITRE ATT&CK, and CIS benchmarks for Microsoft 365 and Azure. Each framework has a dedicated view; ANSSI also shows the steps to reach the next level.
Saporo connects failed controls with permissions, access paths and attack paths to assess exploitability and potential blast radius. See how attackers could reach and exploit a weakness, then understand which identities and critical assets they could compromise from there. Prioritize fixes that remove attack opportunities, break attack paths and strengthen your control posture.
Yes. Saporo provides prebuilt (100+) and custom remediation workflows. Add human approvals for sensitive changes, coordinate work through your existing tools and verify results through subsequent analysis.







