AWS IAM & S3 EXPOSURE

Reduce identity exposure across AWS

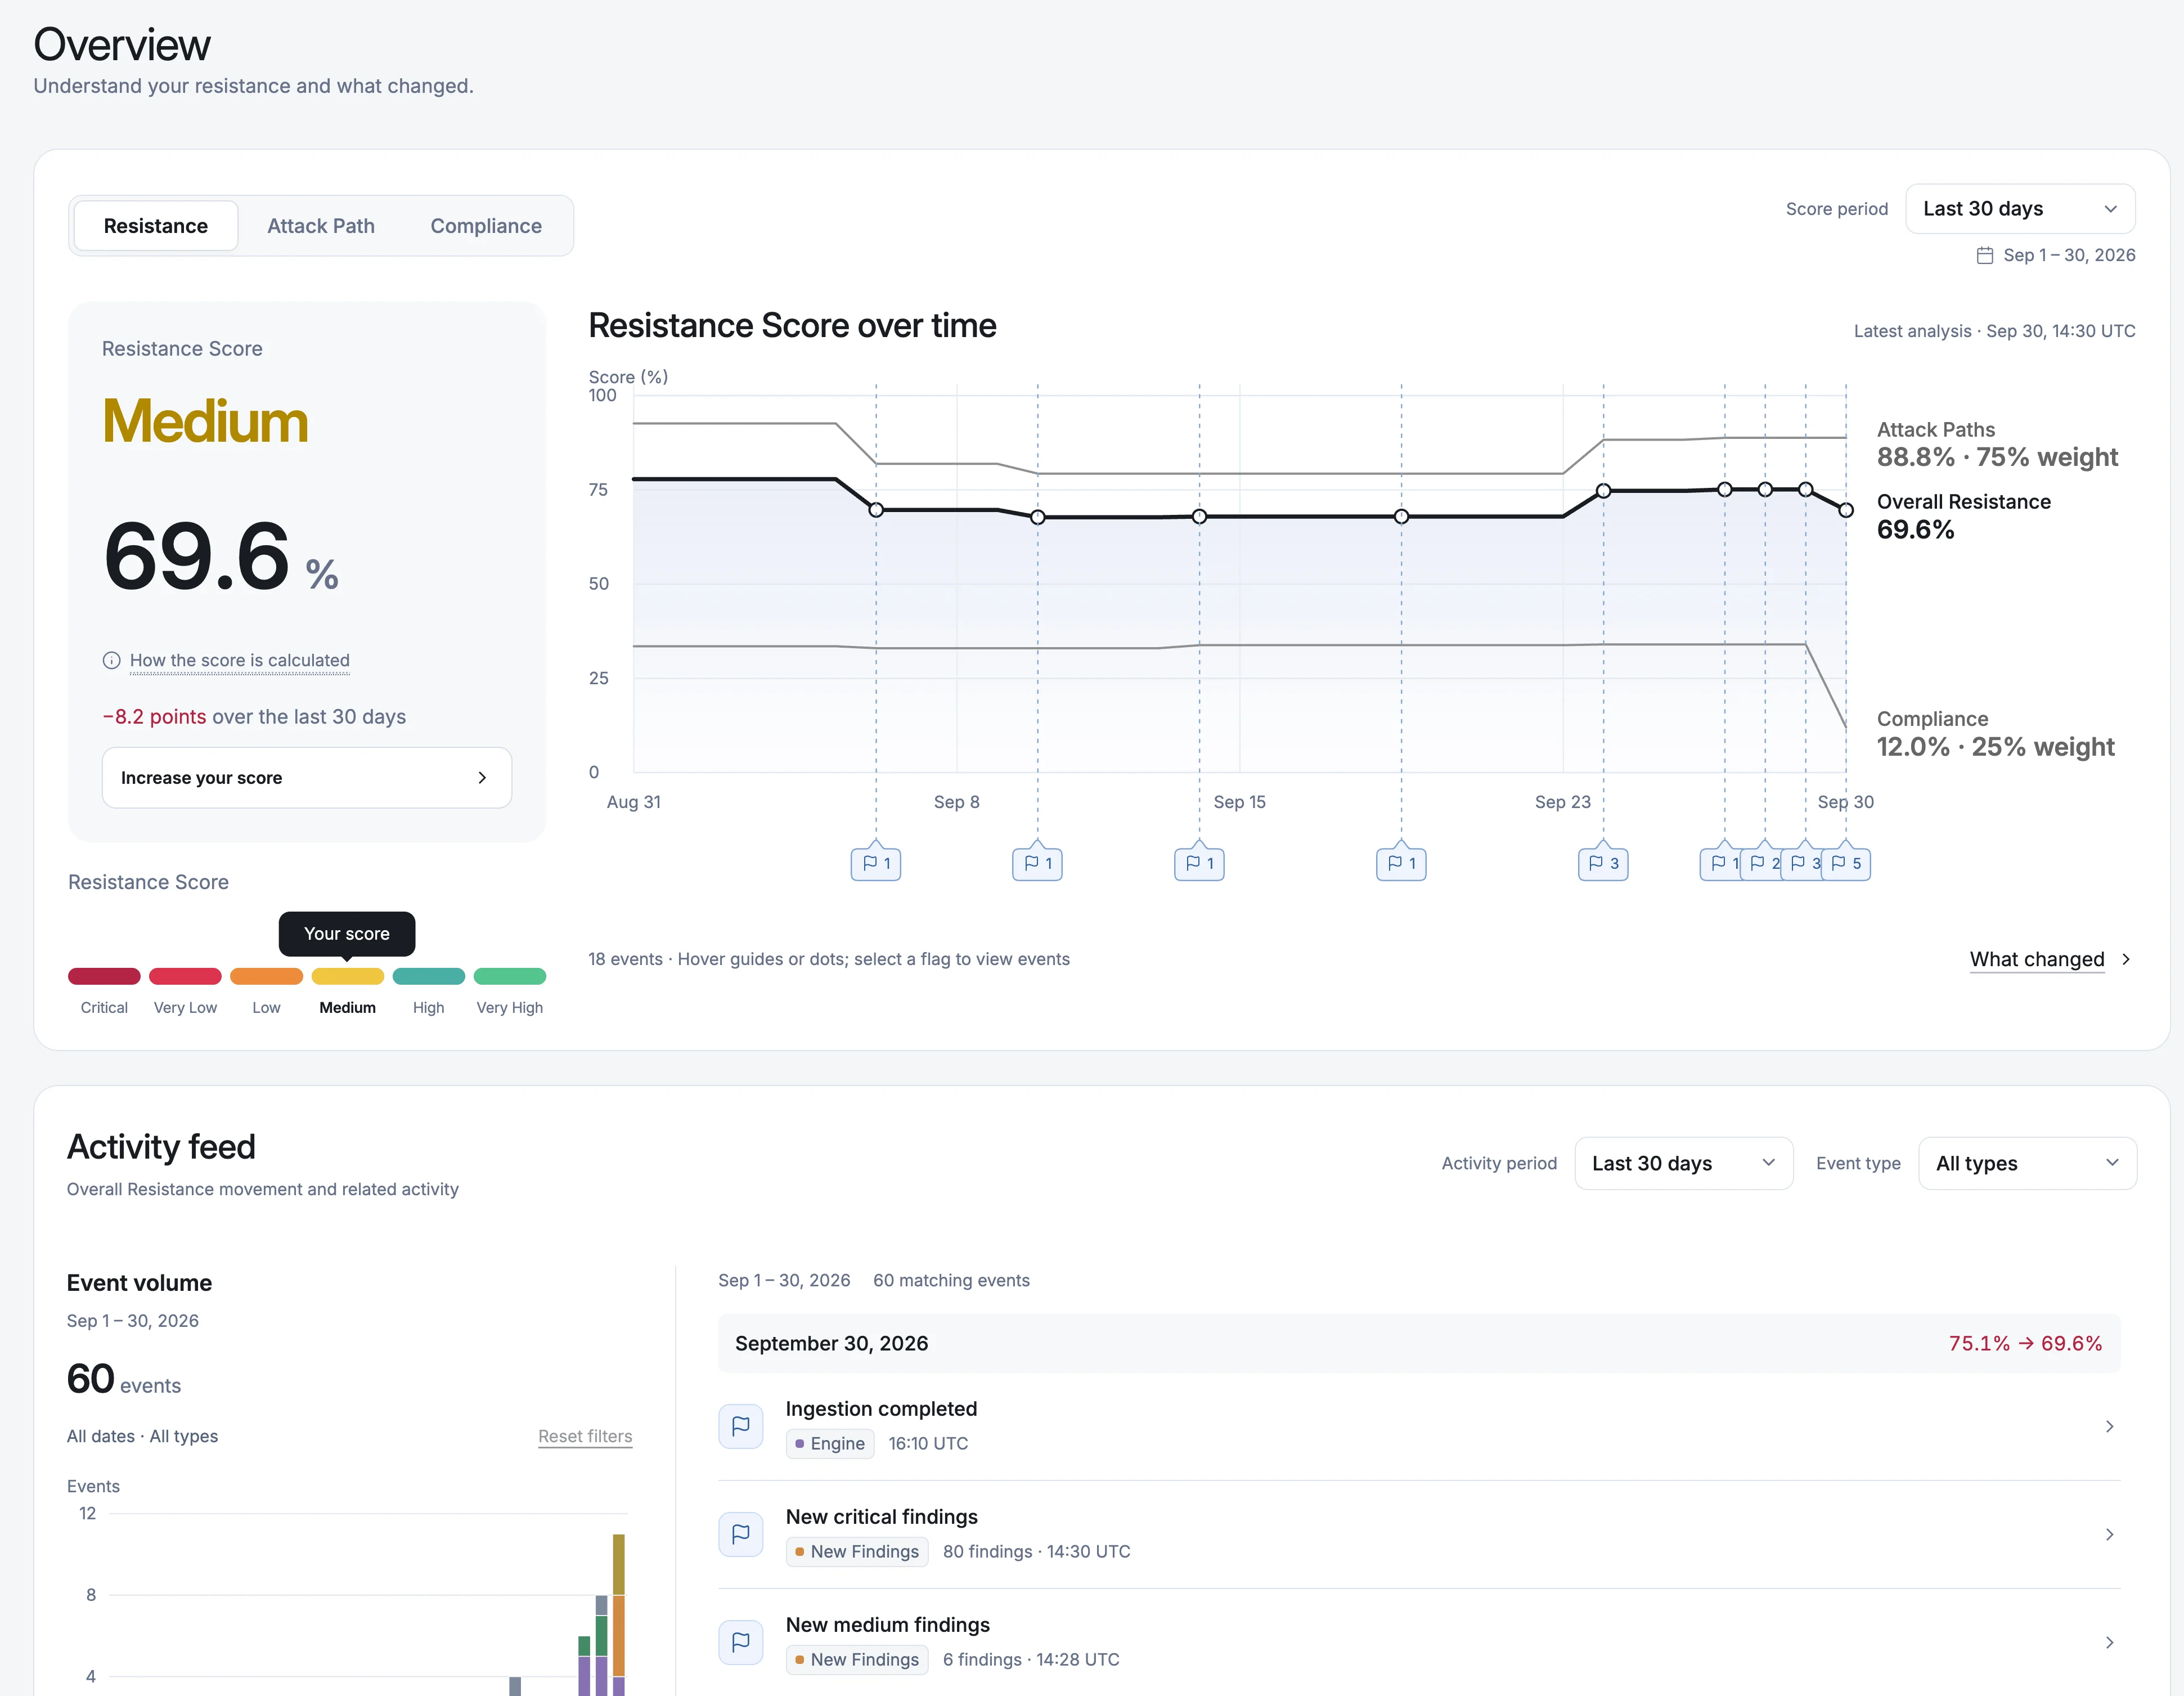
Extend your Saporo environment with focused analysis of AWS IAM and Amazon S3.

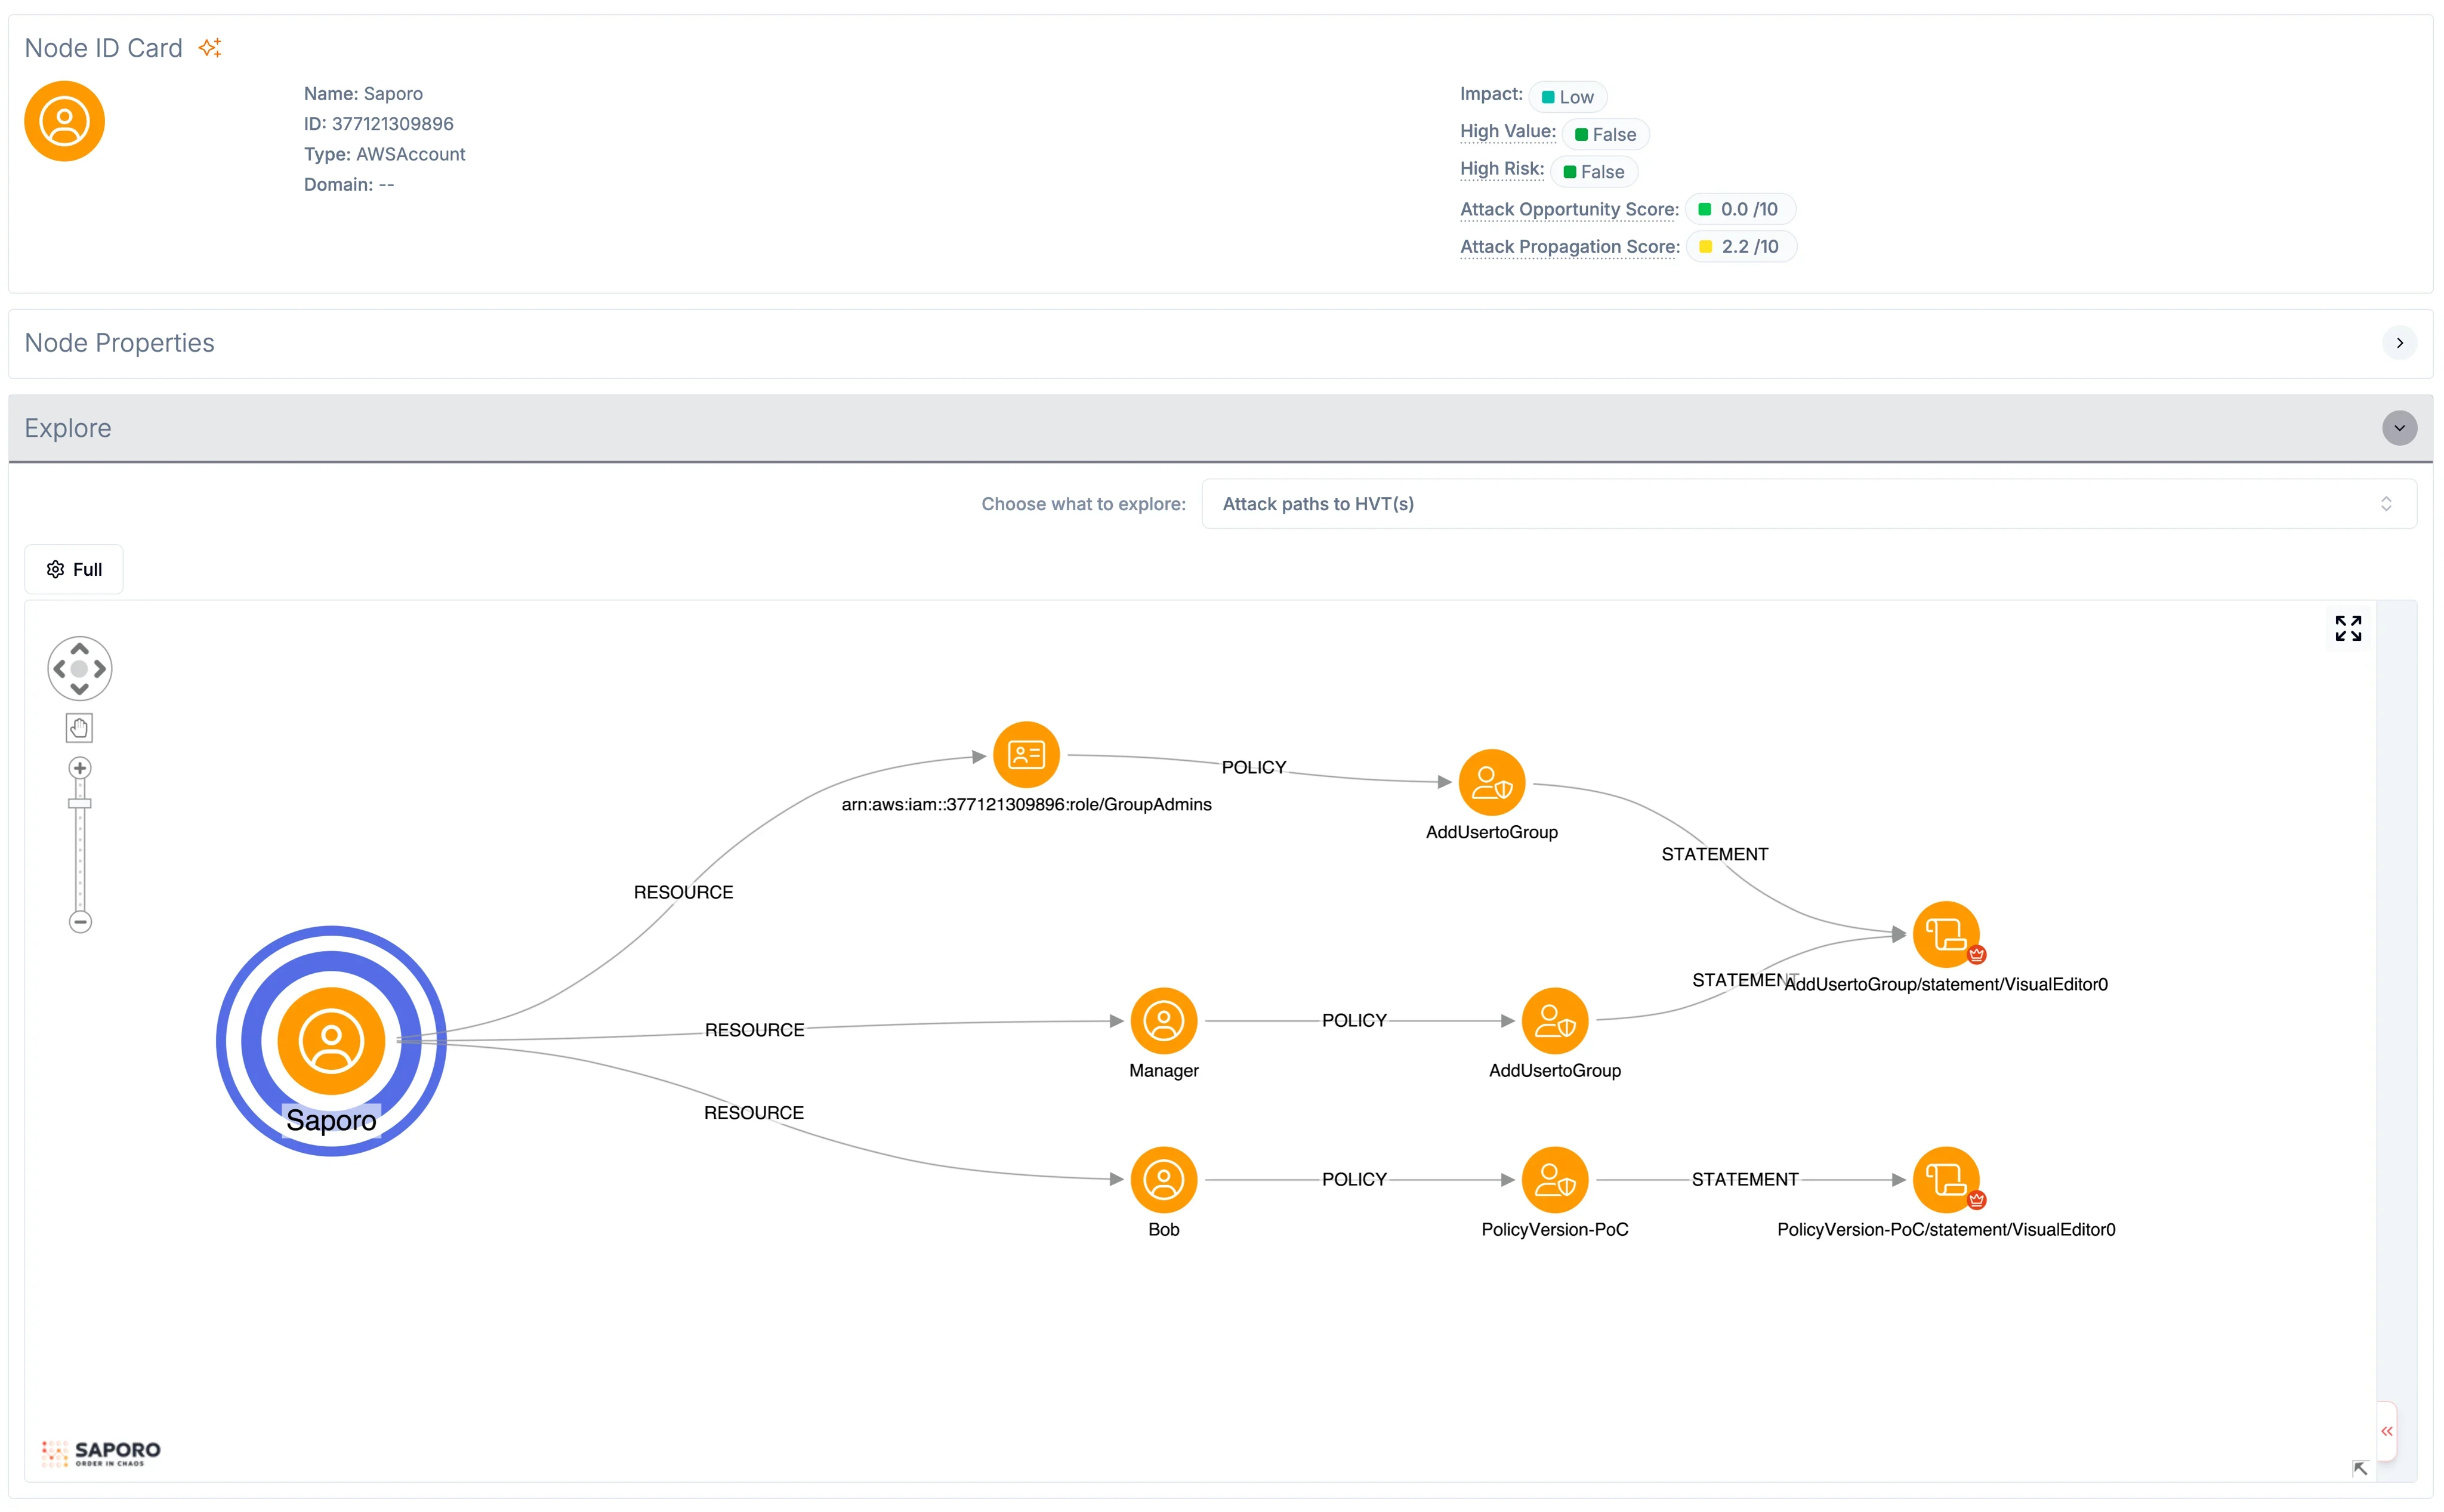
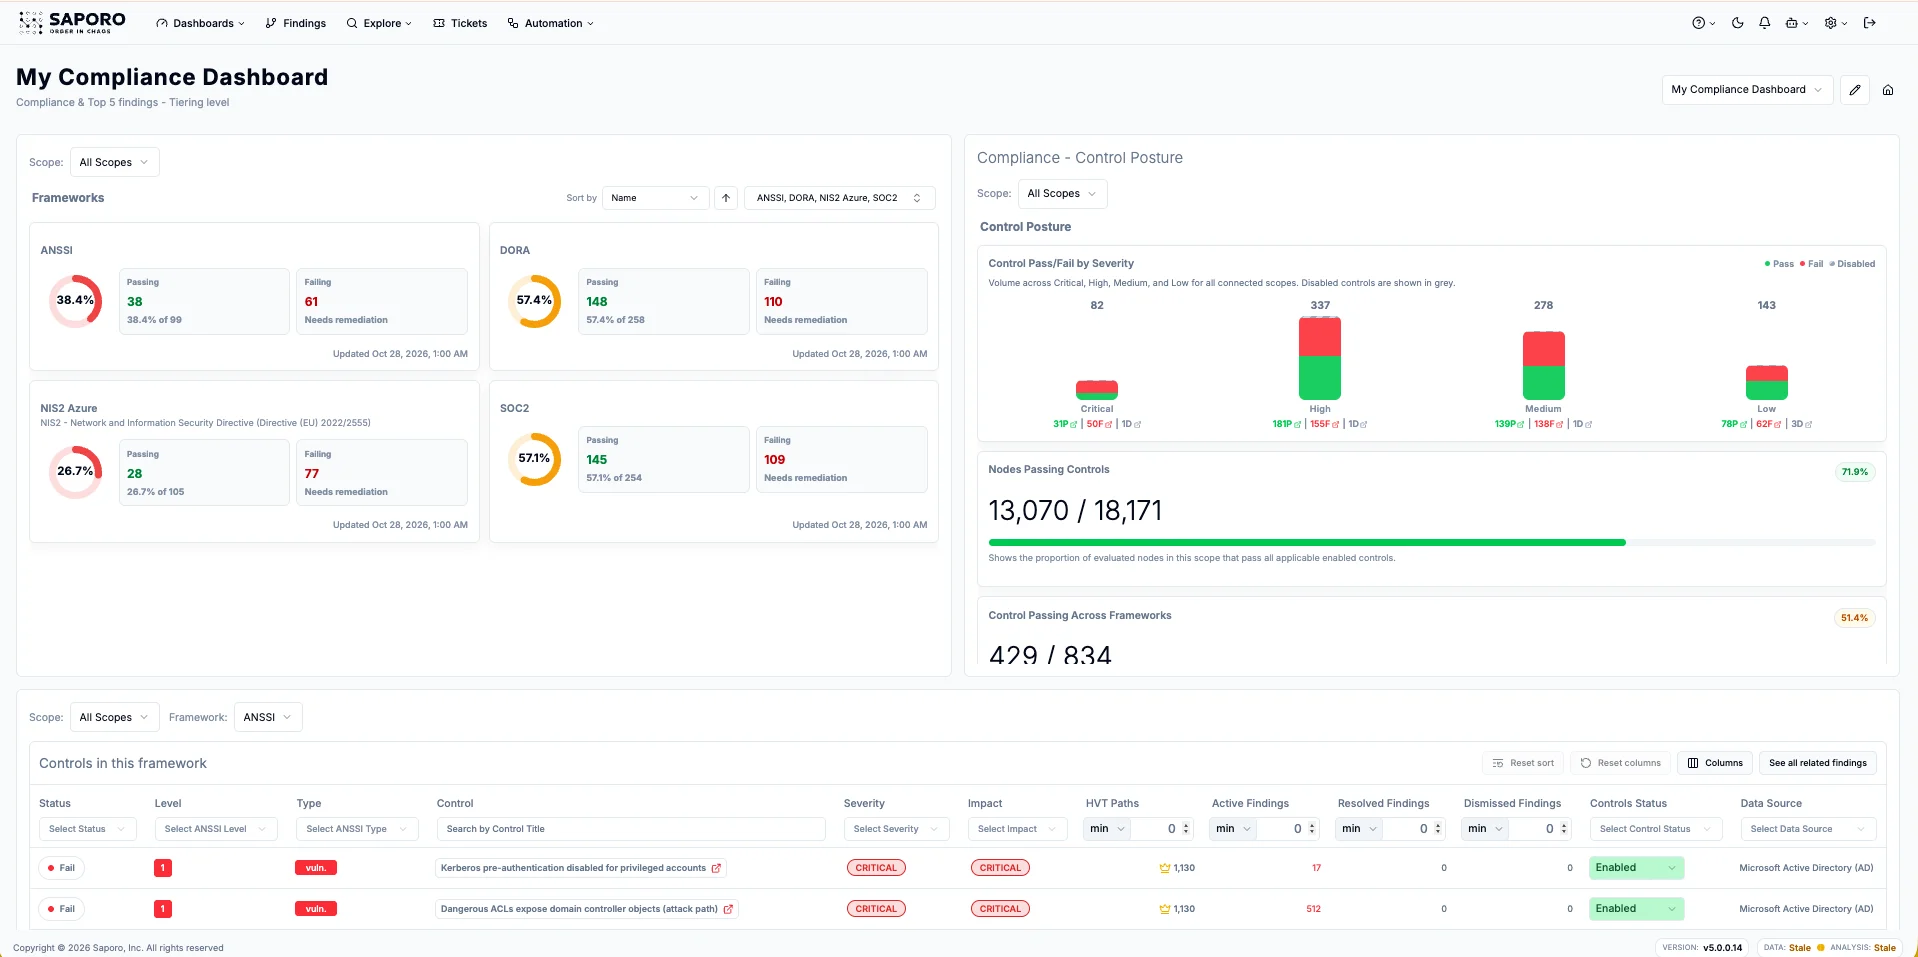
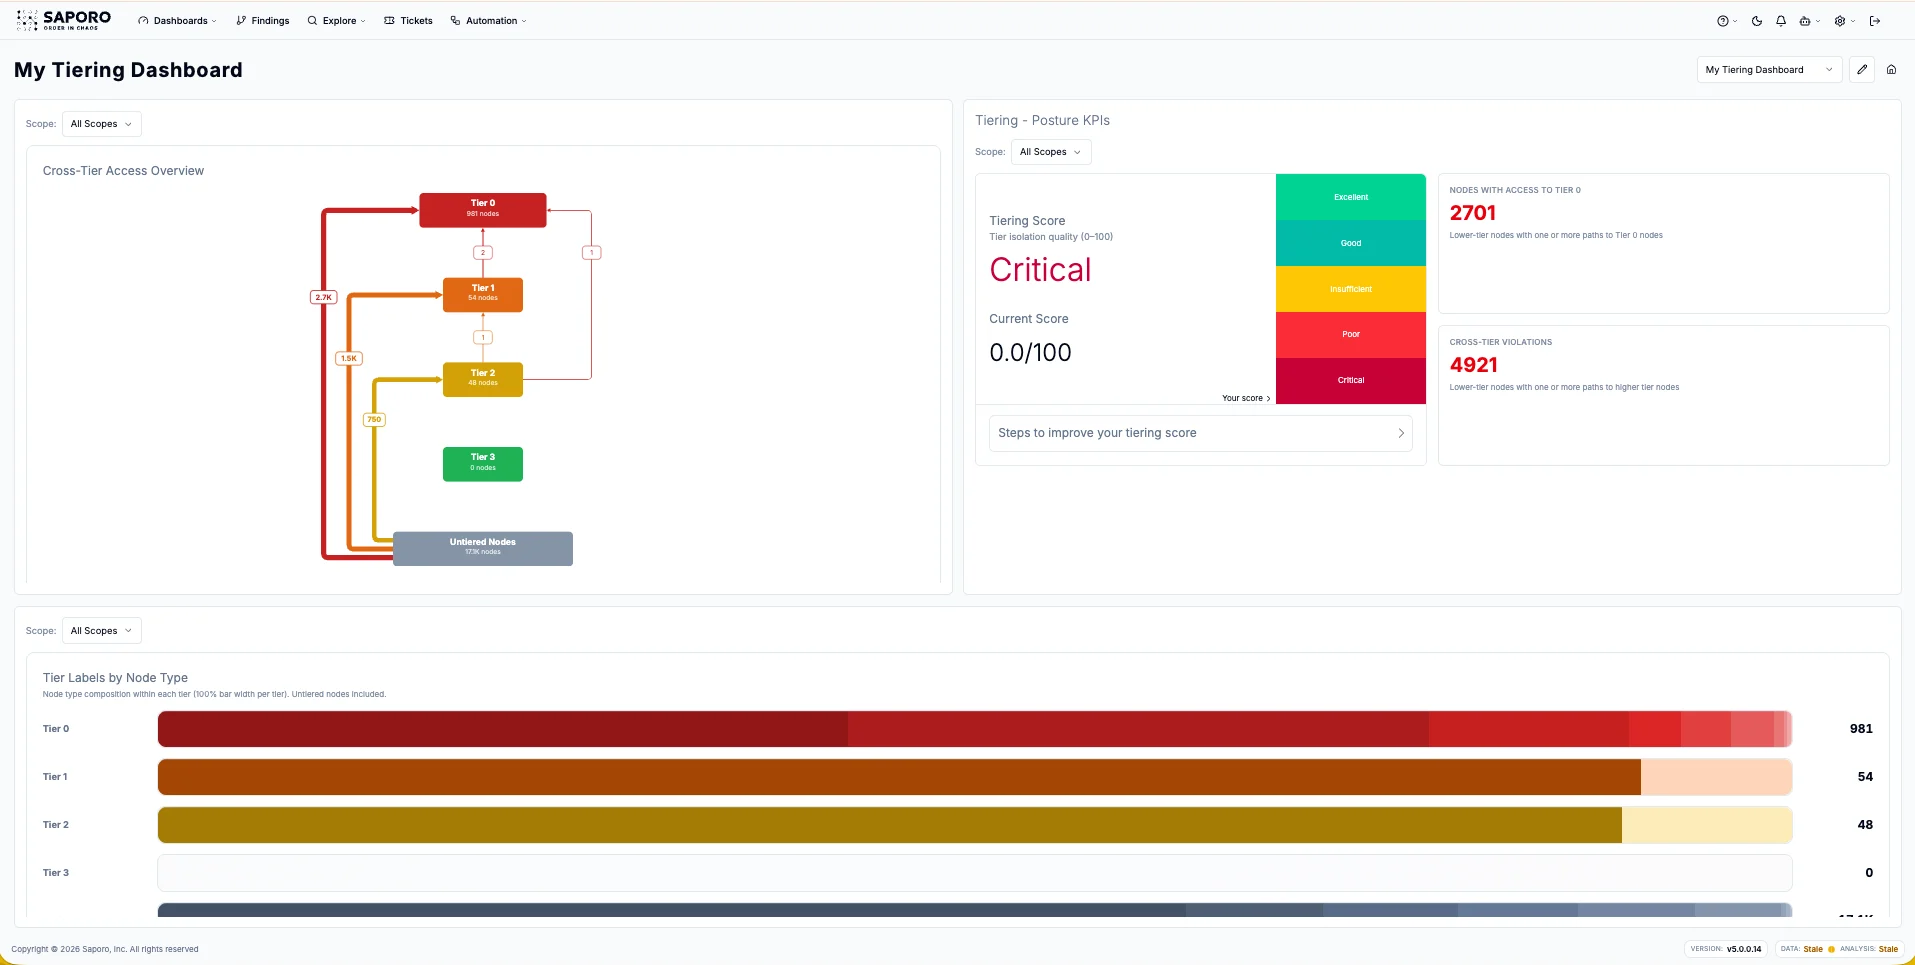
Connect identities, policies, role trust, and bucket permissions to uncover misconfigurations and attack opportunities, then prioritize changes that protect critical assets. AWS is available as a companion source, with broader coverage planned.

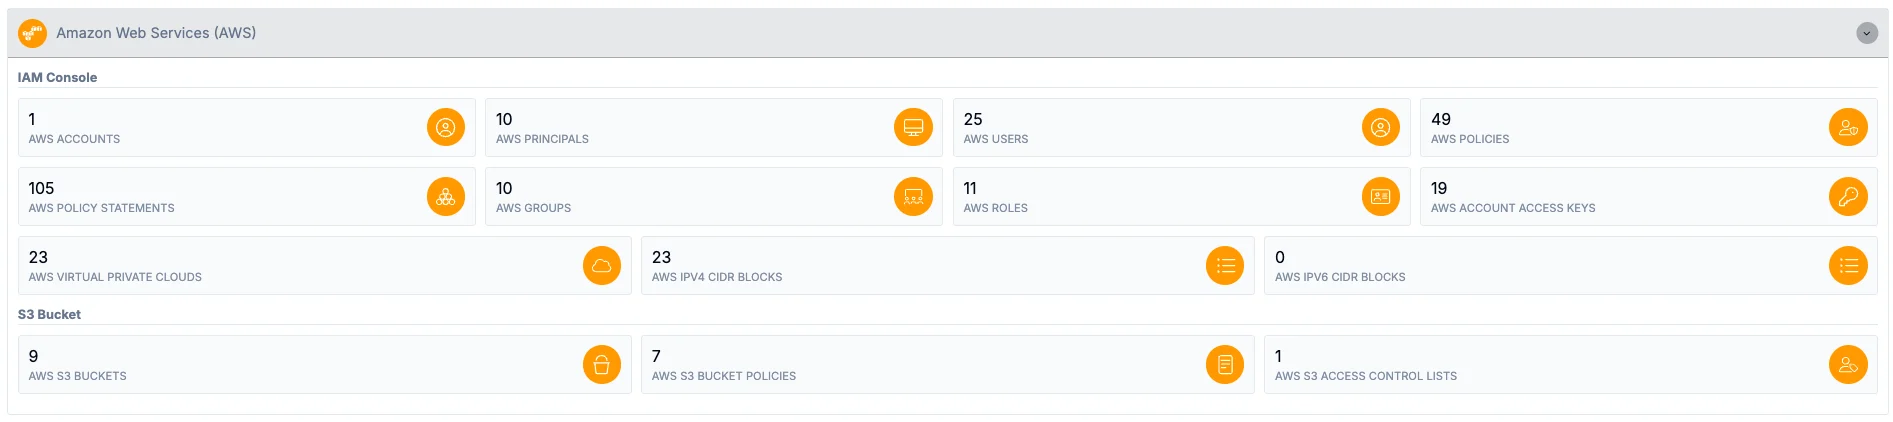
Amazon Web Services
  • IAM users
  • Roles
  • Policies
  • Role trusts
  • Access keys
  • S3 buckets

99% of users, roles, and services across 680,000+ cloud identities had excessive permissions.

Source: Unit 42 Global Incident Response Report 2026

AWS IDENTITY Q&A

What security teams ask about AWS identity exposure

We plan to expand AWS coverage beyond IAM and S3, with deeper permission analysis, additional misconfiguration controls, and identity exposure analysis for Amazon Bedrock. For Bedrock, the focus is on connecting AI agents, models, and knowledge bases to their IAM roles, permissions, and data sources. Further expansion may include compute, serverless, database, and secrets management services, helping teams uncover more attack opportunities across AWS.

Current coverage focuses on IAM users, groups, roles, policies, role trust, access key metadata, and Amazon S3 buckets, policies, and ACLs. Saporo uses supported relationships to reveal selected privilege-escalation opportunities and access to S3 resources.

AWS is currently offered as a companion source within a broader Saporo deployment. It is not sold as a standalone offering.

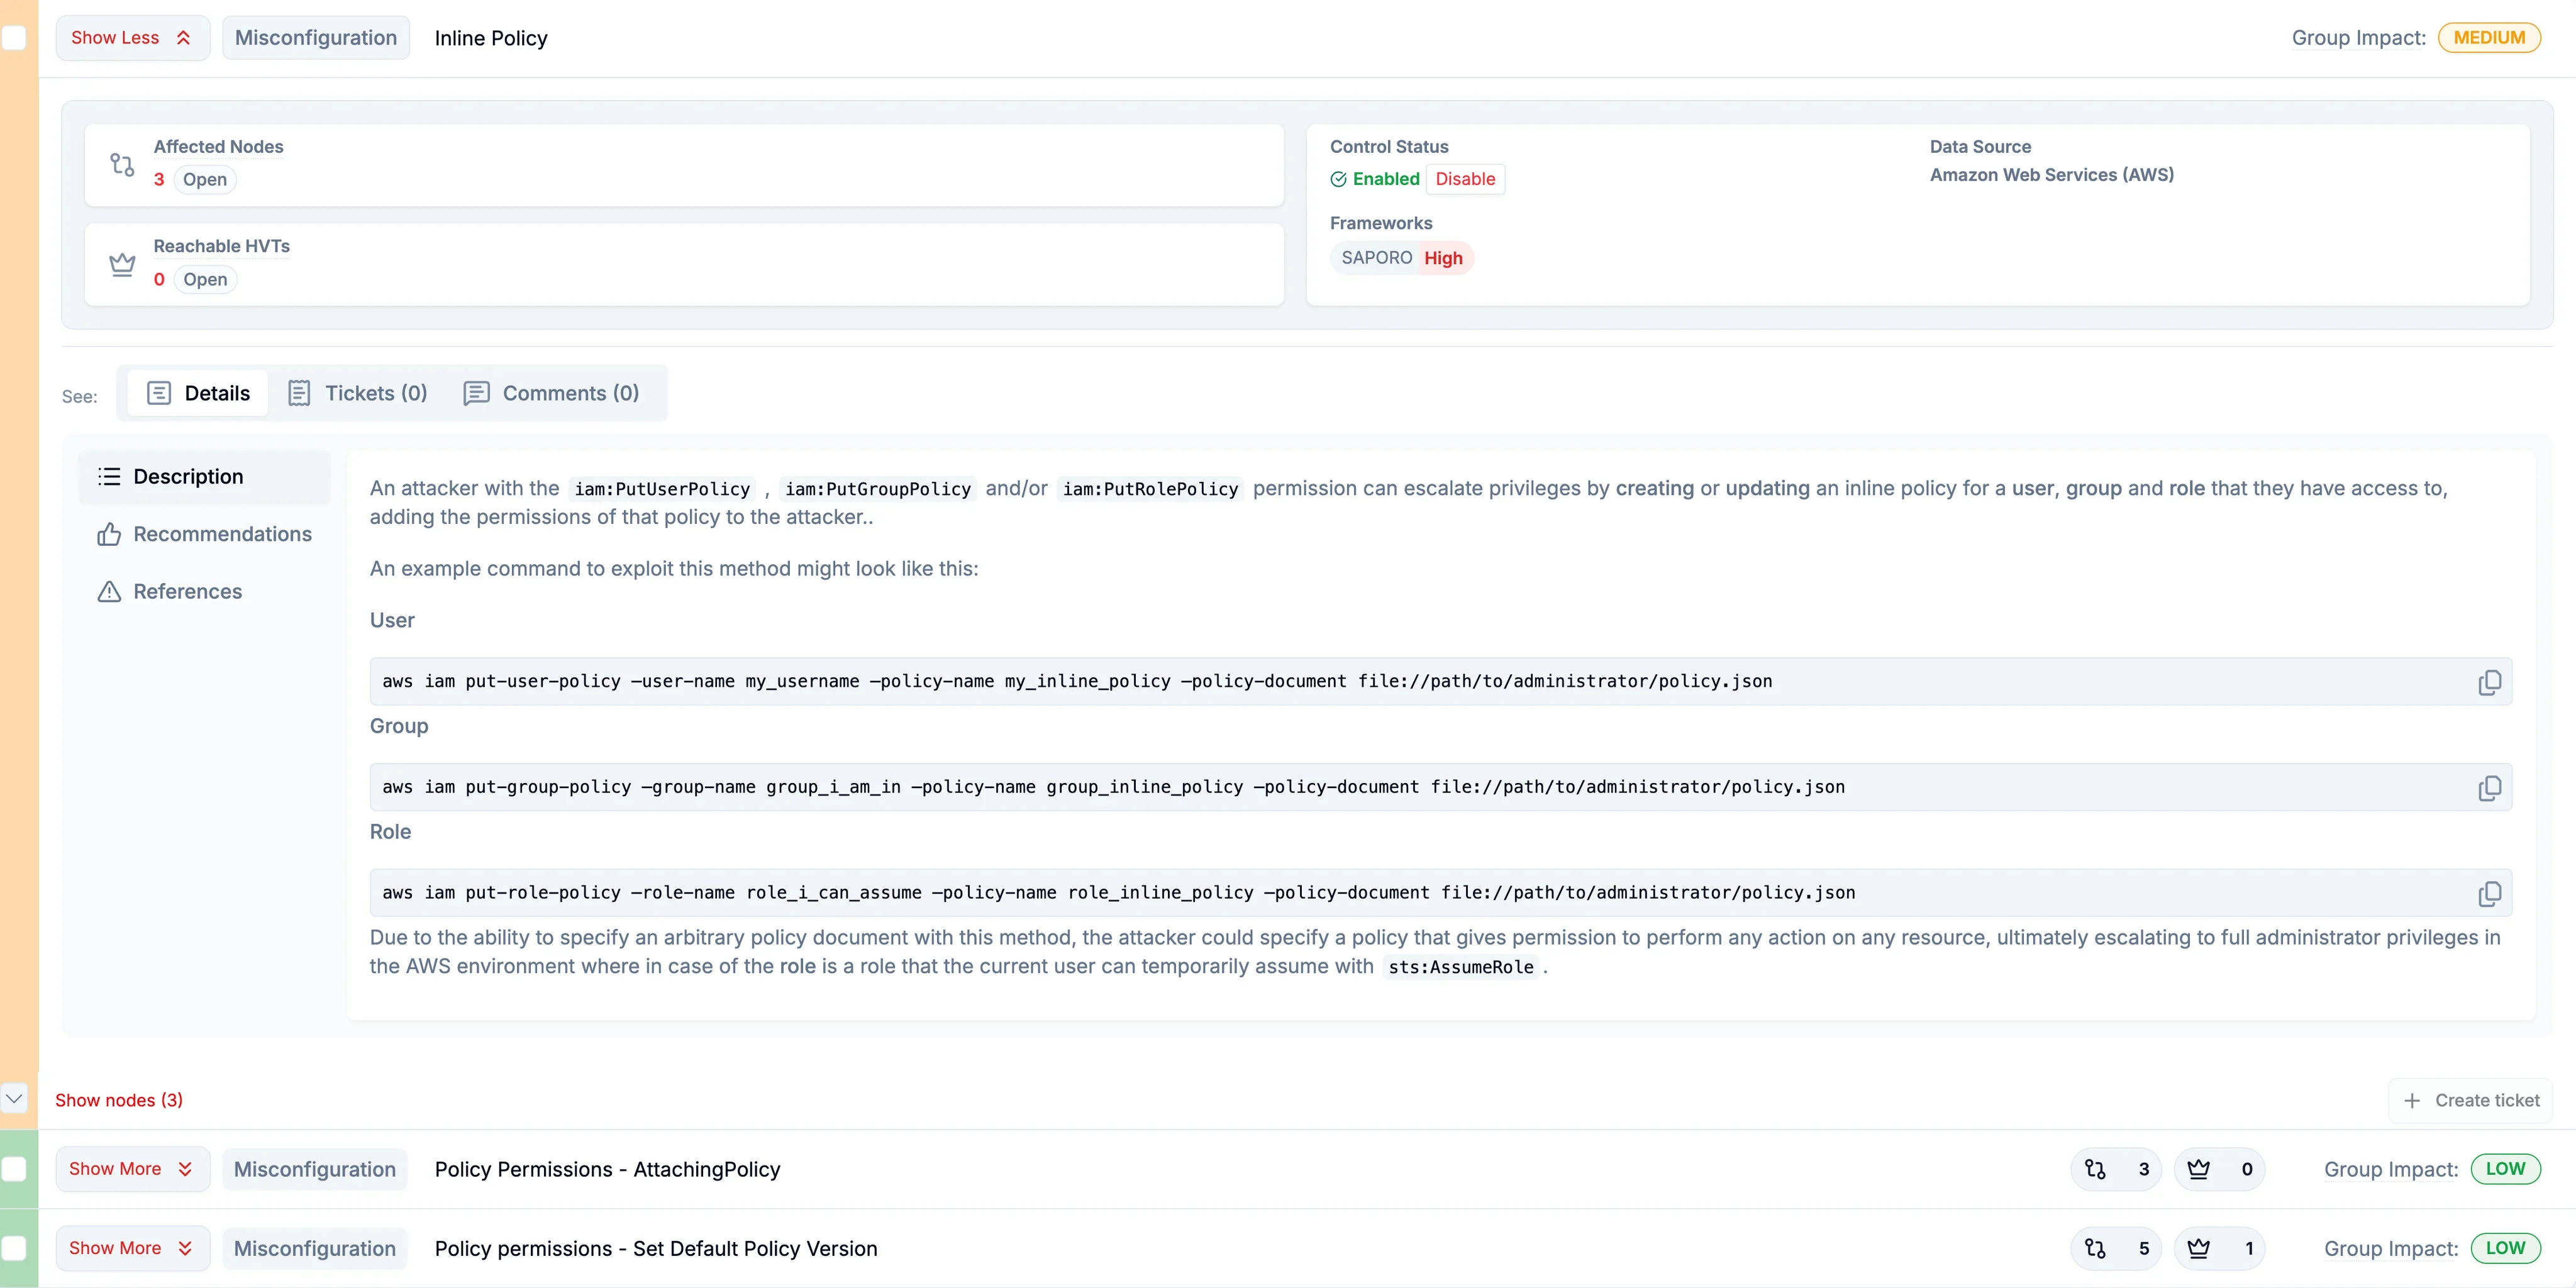
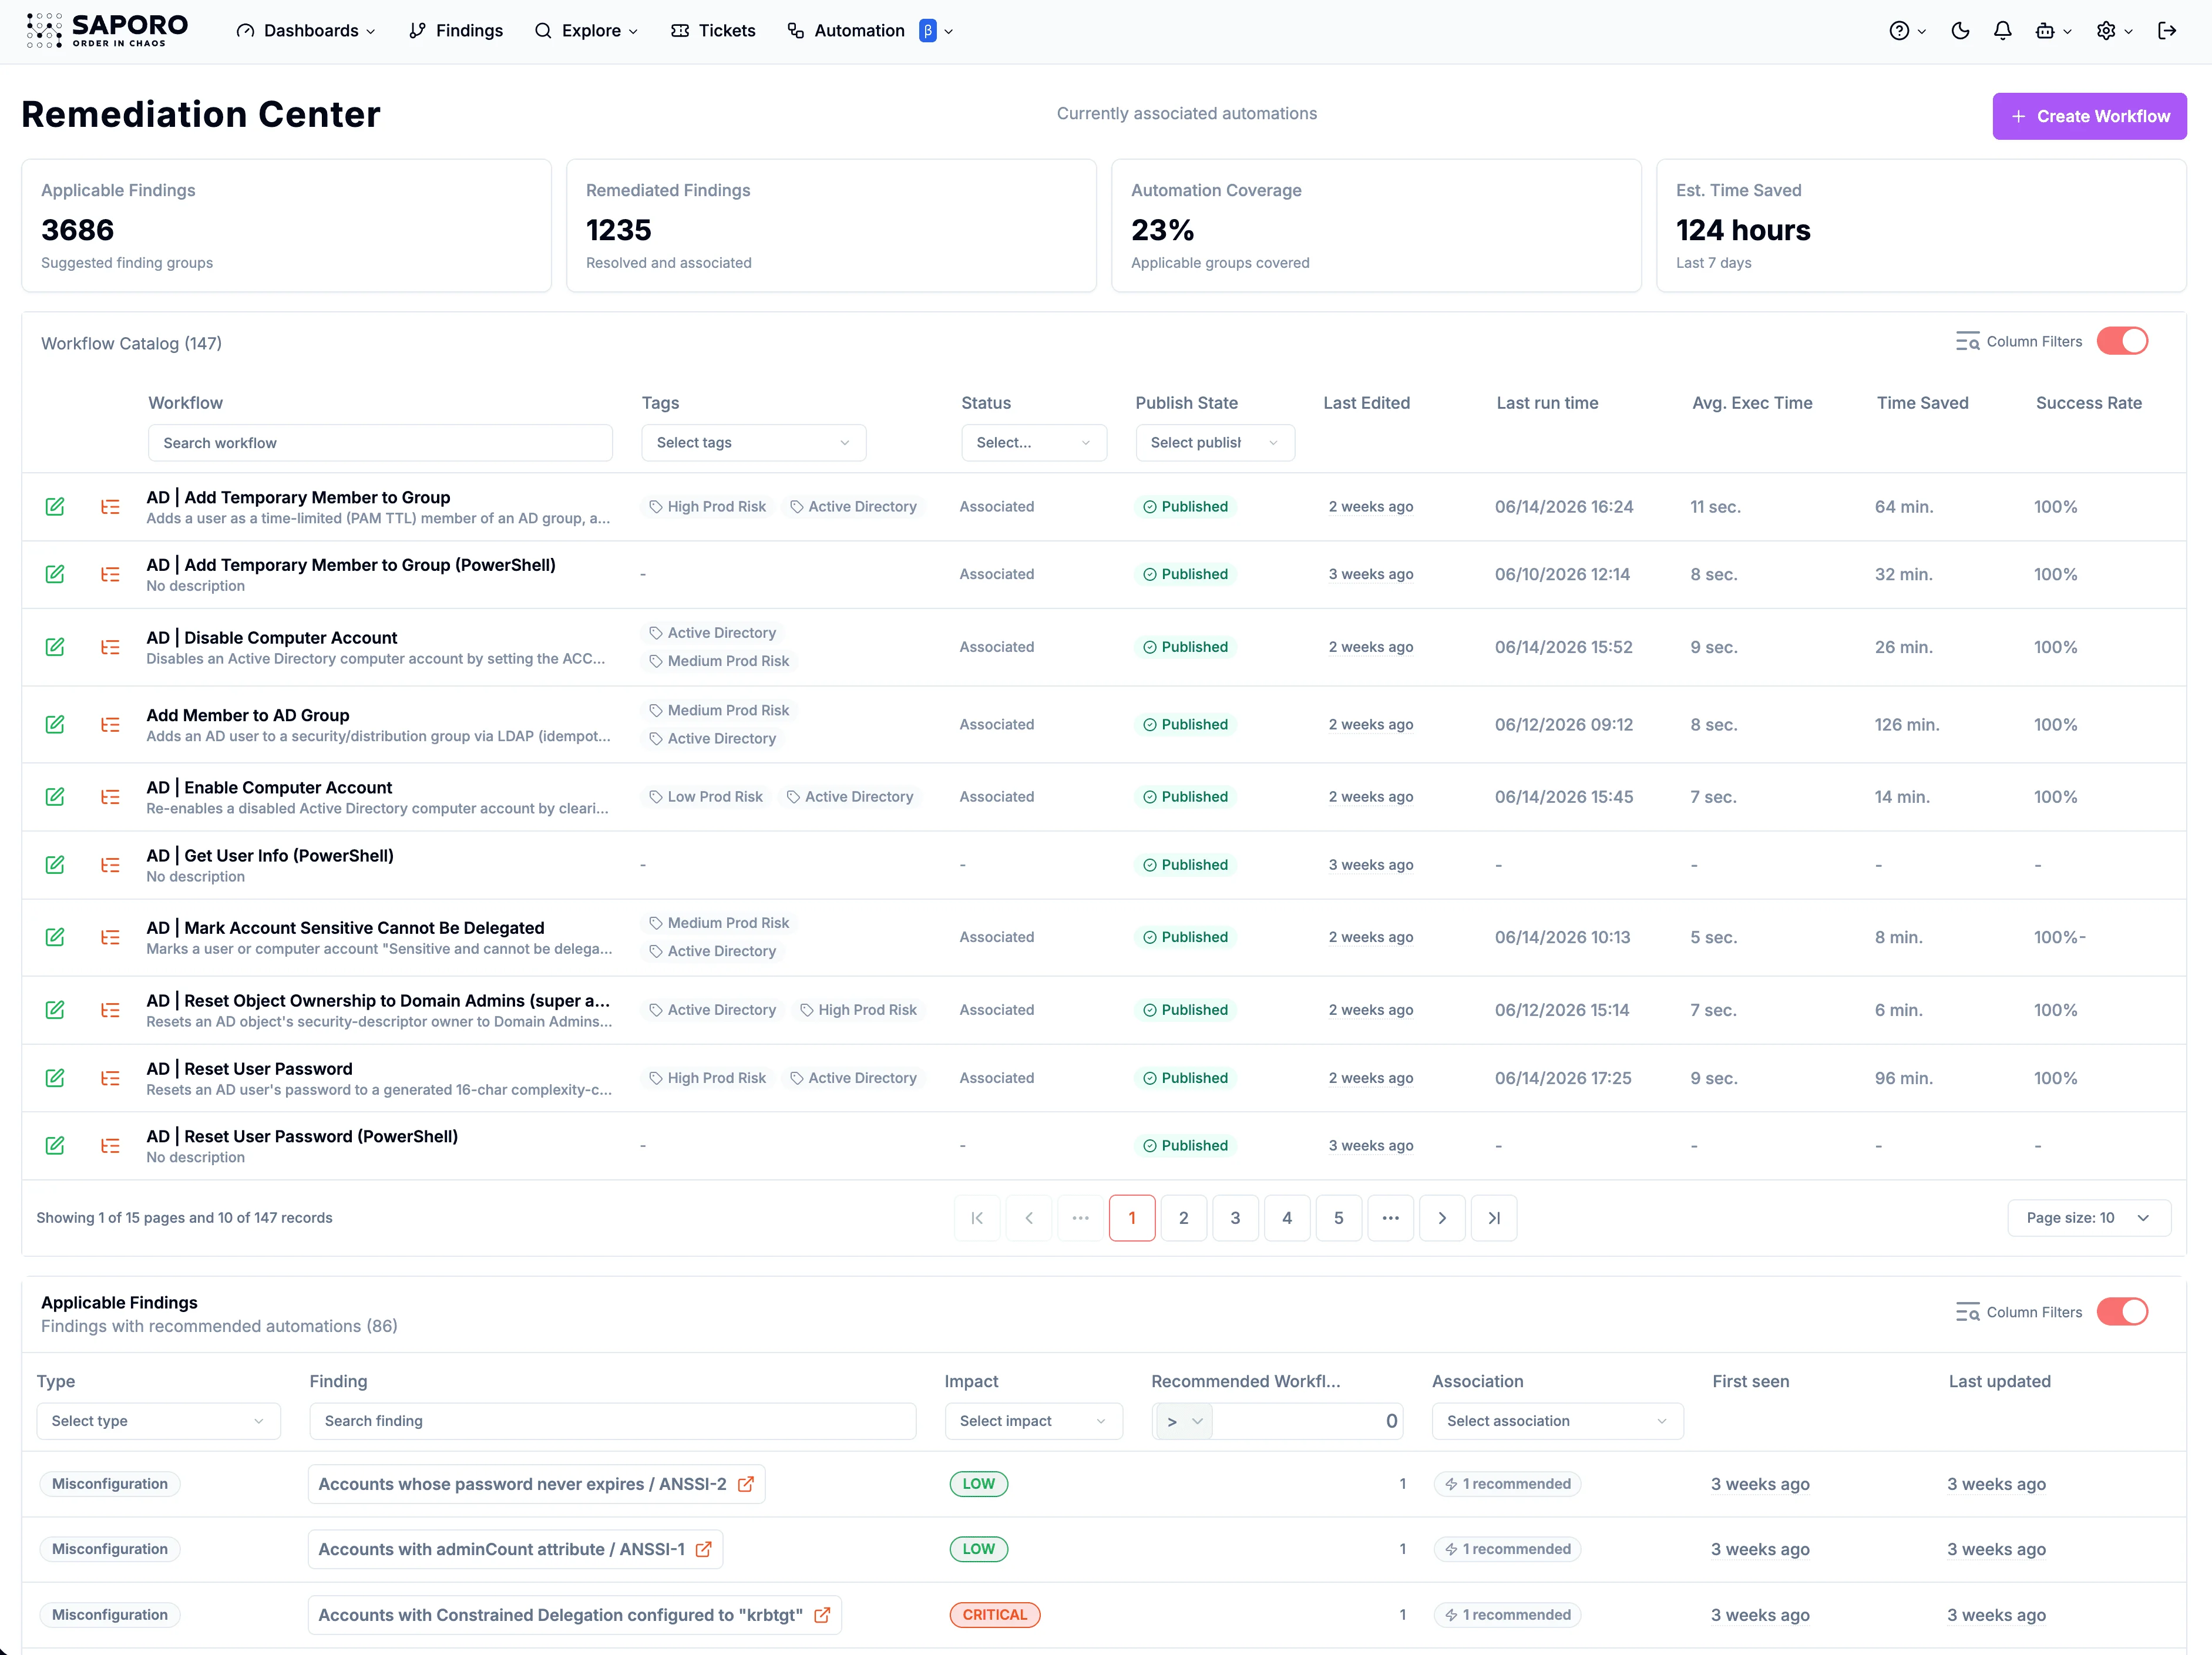
Yes. Saporo identifies selected IAM permissions and policy configurations that can enable privilege escalation, including policy attachment, access key creation, group membership changes, and policy-version changes. Supported graph relationships help teams understand the potential impact.

Saporo inventories S3 buckets, bucket policies, and ACLs, and models supported read, write, and full-access relationships. This helps teams review which identities could reach buckets designated as high-value targets.

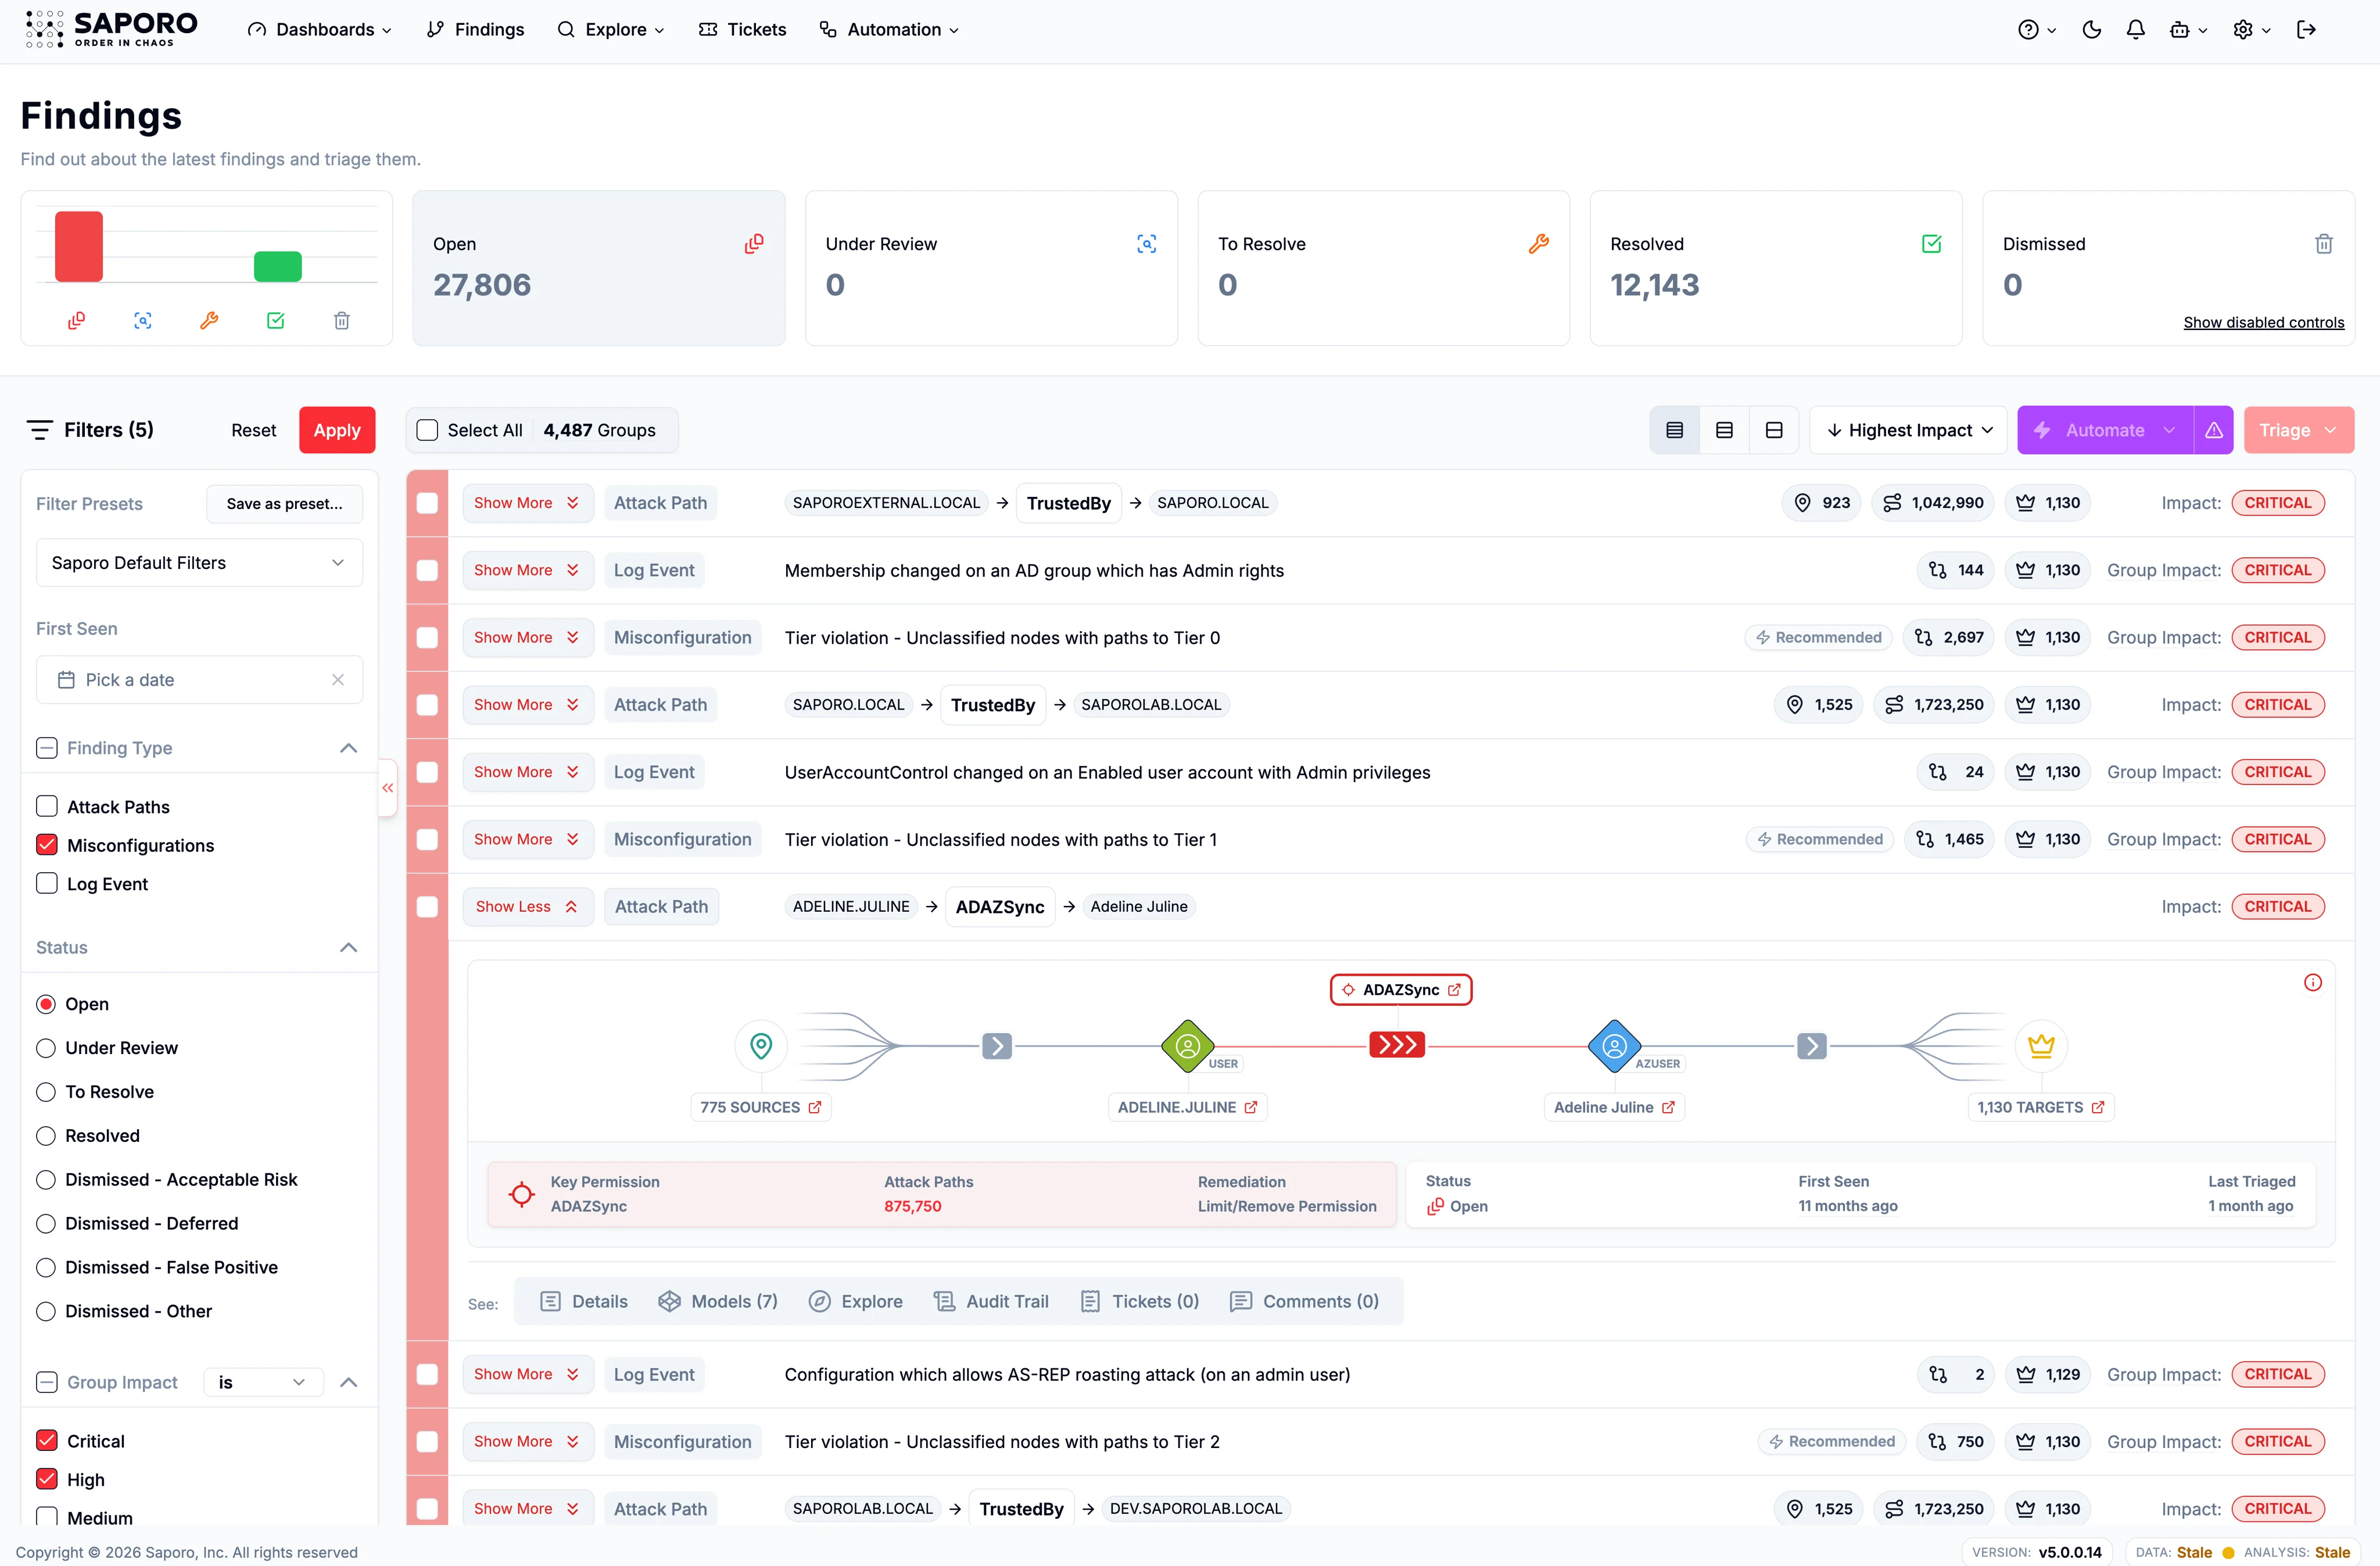
AWS adds focused IAM and S3 visibility to Saporo’s broader identity exposure analysis. Its objects, relationships, and findings can be reviewed alongside other connected identity sources in the same platform.

Reduce identity exposure before it becomes an attack

Book a demo